


Woot!
We got your request. Hang on tight and we'll get back to you!

 Assessment Management
Run structured security assessments across systems, teams, and vendors—all from one place.
 Questionnaires & Surveys
Launch structured questionnaires and collect evidence from the people closest to each control.
 Reports & Scorecards
Turn assessments into audit-ready reports and actionable insights your team can actually use.
 Inventory Management
Maintain a connected inventory of vendors, assets, and systems linked to assessments and risks.
 Exception Management
Log, track, and resolve policy exceptions so nothing falls through the cracks during audits.
 Risk Management
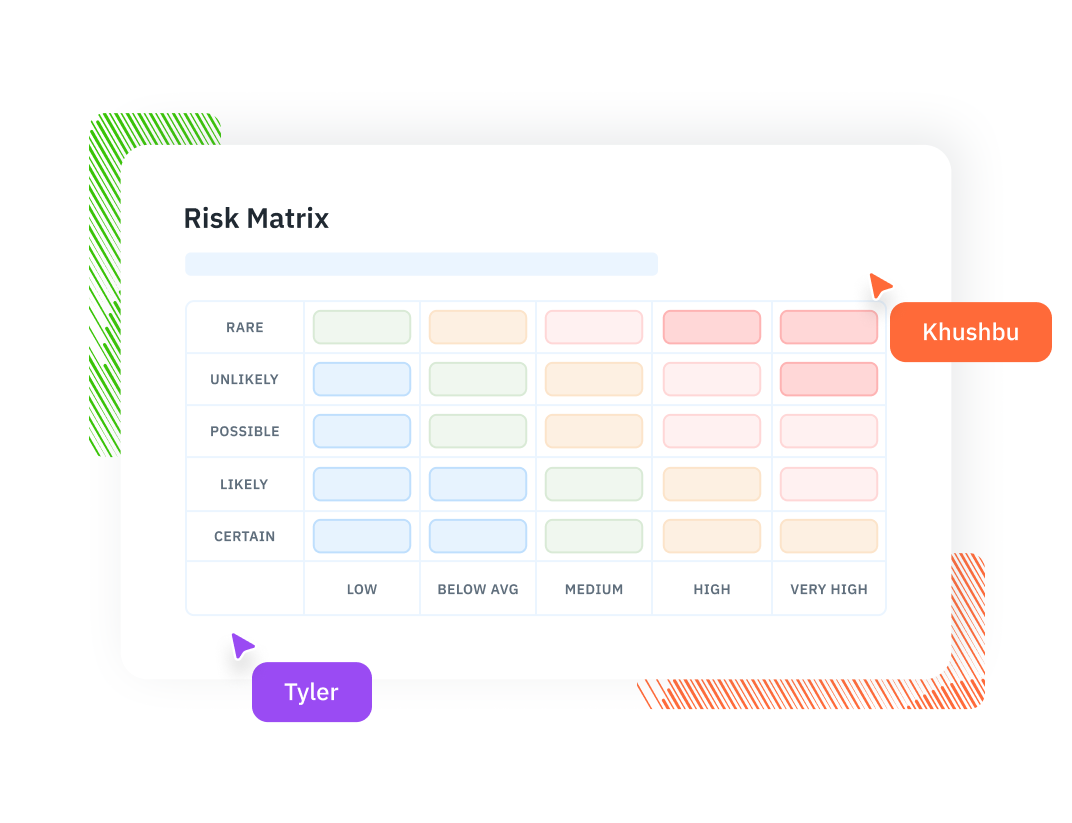
Turn assessment findings into a living risk register with owners, remediation plans, and full lineage.
 Information Security Risk Management (ISRM)
Run assessments across units and systems, maintain IT asset inventories, and collaborate on a shared risk register—all in one place.
 Third-Party Security Risk Management (TPSRM)
Track vendors, send security questionnaires, and manage third-party risk with built-in workflows and a centralized inventory.





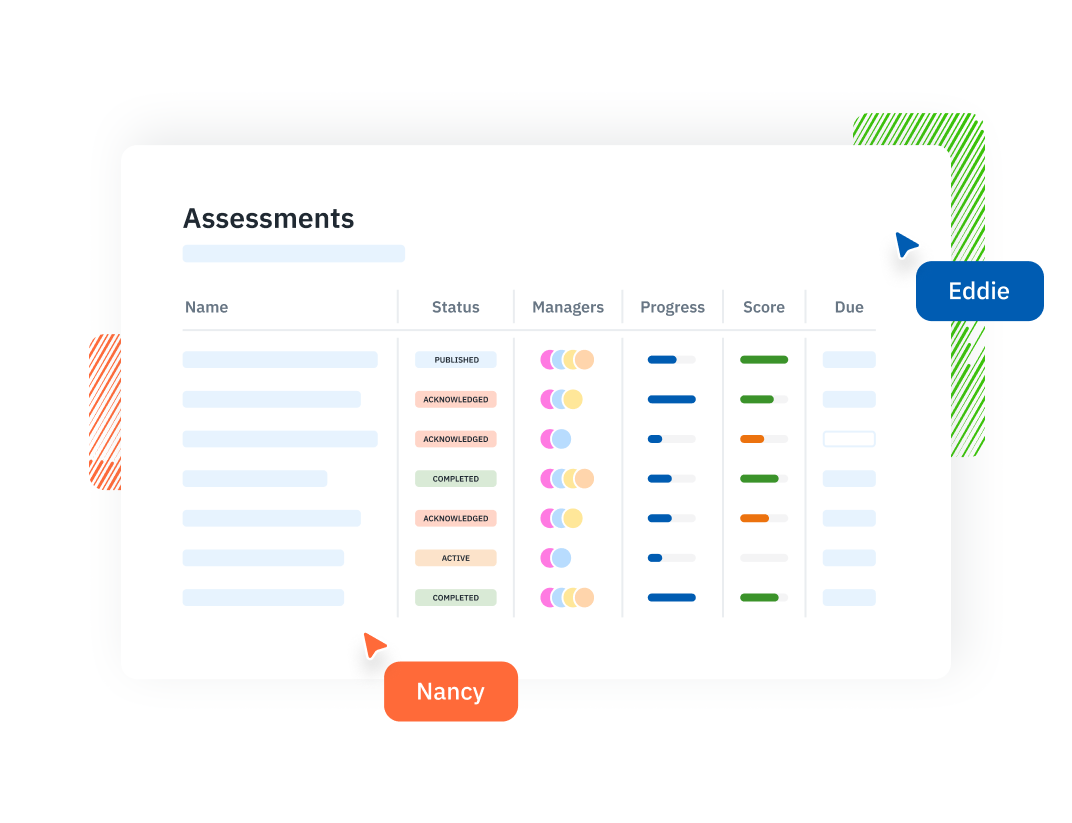
Launch assessments from prebuilt NIST 800-53 questionnaires mapped to control baselines. Questionnaires target system owners and department leads across every control family, collecting evidence inline, including access control documentation, audit logs, and configuration records. Recurring cycles keep responses and proof connected for continuous monitoring.
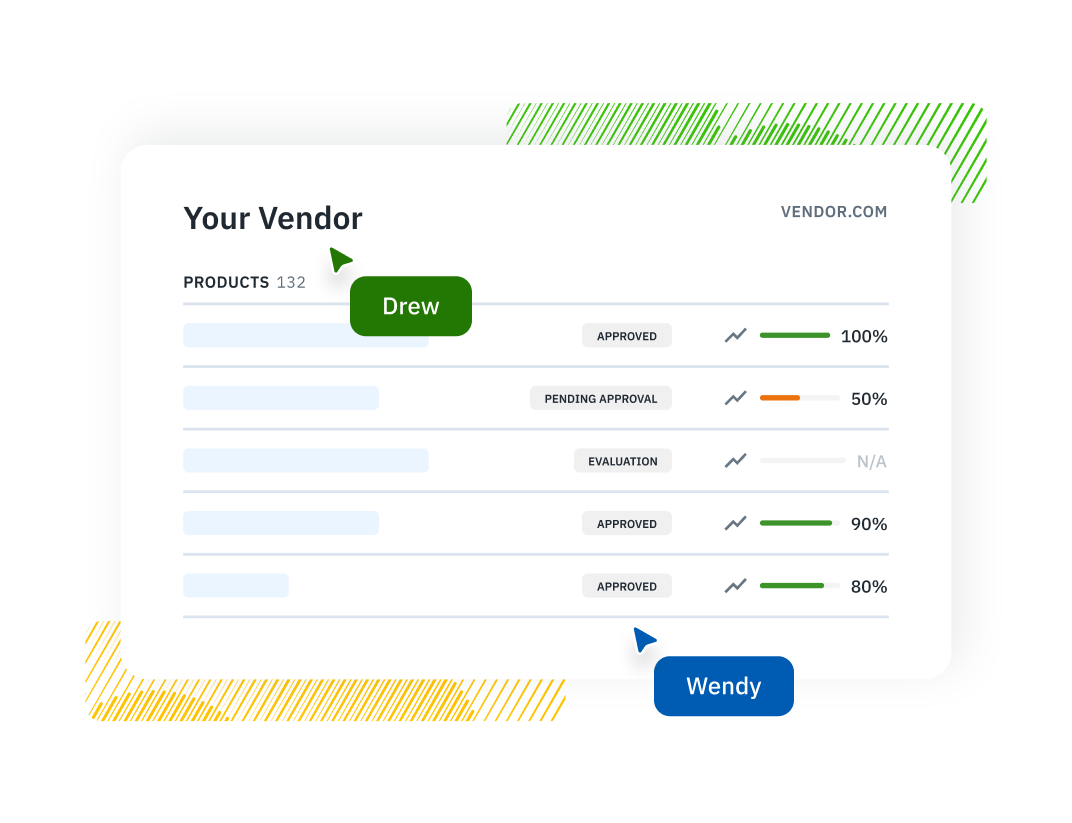
Link every system, asset, and vendor record to its assessments, risks, exceptions, and documentation. To scope a new assessment, filter by system boundary, data classification, or impact level. When vendors provide services to a system in scope, their questionnaire results link to that system's record automatically. That way, the inventory is updated as part of the assessment workflow itself.
Publish a control gap to the risk register as soon as an assessment identifies it. In Isora, every risk carries lineage — the 800-53 control it maps to, to the assessment question that surfaced it, the system it applies to, and the remediation plan. Triage findings by escalating to the register, documenting an exception with compensating controls, or closing with justification, all with an append-only audit log that records every decision.
Generate reports and scorecards to demonstrate control effectiveness across families, risk status by system, and remediation progress over time. Drill down into the underlying assessment response and evidence for every summary metric with live data. Then, export packages for authorizing officials, auditors, and oversight bodies in just a few clicks.

