





IT Vendor Risk Management Software: Compare Platforms for Vendor and Third-Party Risk
An IT vendor risk program finds out whether the companies an organization relies on can protect its data and systems. The security team keeps an inventory of vendors, sends security questionnaires, reviews evidence such as SOC 2 reports, and records the gaps it finds as tracked risks. The cycle repeats as vendors and contracts change.
Some of that work is set by regulation. The FTC’s Safeguards Rule, which implements the Gramm-Leach-Bliley Act (GLBA) for financial institutions under the FTC’s jurisdiction, requires overseeing service providers, including “periodically assessing your service providers based on the risk they present and the continued adequacy of their safeguards.” Under the HIPAA Security Rule, a covered entity may let a business associate handle electronic protected health information only if it obtains “satisfactory assurances” that the business associate “will appropriately safeguard the information.”
Vendor risk software covers two different jobs. Security ratings platforms score vendors from what can be observed from outside, with nothing required from the vendor. Assessment platforms send questionnaires, collect evidence, and record what the team found and accepted. Several products on this page do some of both, and a ratings feed and an assessment program can run together. This guide compares IT vendor risk management software against that work.
What to Look For in IT Vendor Risk Management Software
When evaluating IT vendor risk management software, the factors an organization can consider depend on its use case. Still, here’s what a platform should cover:
- Structured vendor assessments using questionnaires such as HECVAT, SIG, and CAIQ
- Questionnaire delivery, completion tracking, and collection of evidence such as SOC 2 reports
- A vendor inventory that separates high-risk from low-risk vendors, with an owner for each
- A risk register and exception tracking that follow each finding to closure
- Scoring, reports, and scorecards that leadership and auditors can read
- An interface that vendors and people outside security can use
- A way to bring external security ratings into vendor records, if the program also uses a ratings feed
- A clear implementation timeline and the internal effort it requires
Make sure to ask potential vendors about each of these capabilities, before you sign a contract.
Top IT Vendor Risk Management Tools
Isora GRC
Isora GRC is the GRC Assessment Platform™ built specifically for information security teams. It supports the full risk workflow, from assessments and questionnaires to risks, inventory, and reporting. It assesses three kinds of targets: departments, applications, and third-party vendors, each with its own question lists.
Best for: Security teams that need to operationalize IT and third-party risk management across assets, third-party vendors, and business units.
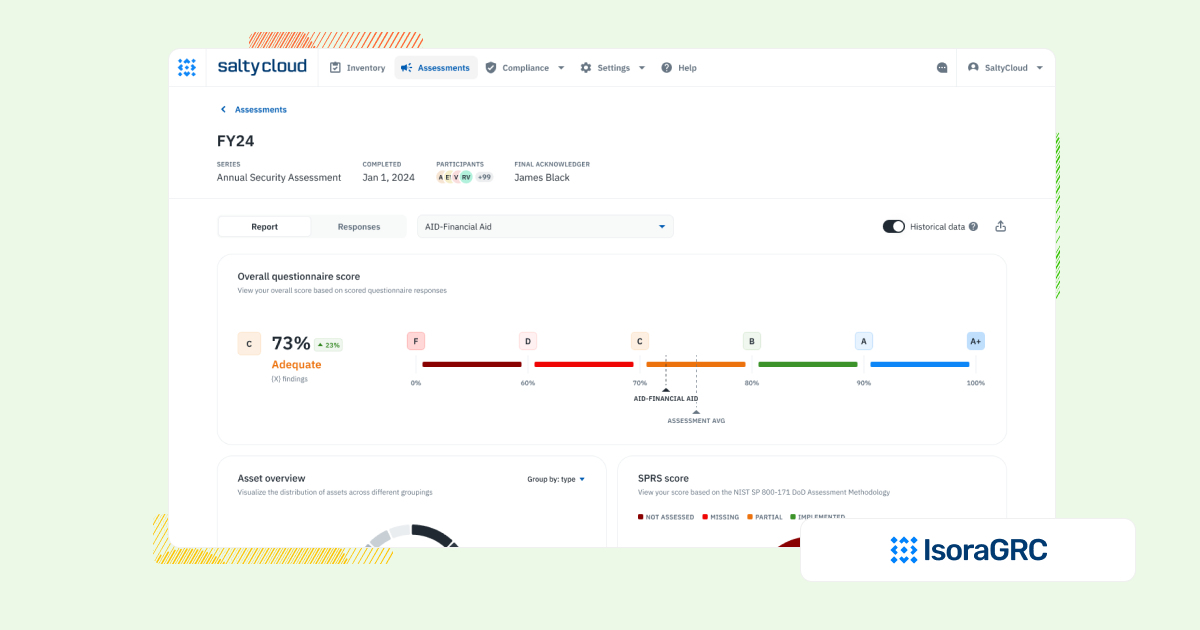
| Isora GRC | |
| Strengths | Built for workflows, not checklists
✅ Supports assessments, inventory tracking, risk registers, and exceptions in a unified experience. Designed for org-wide adoption ✅ WCAG-compliant UX built for respondents outside security, which makes risk everyone’s job. Fast time-to-value ✅ Live in days or weeks, with no-code setup and minimal lift from IT. Flexible by default ✅ Customizable assessments, scalable categories, and framework-aligned questionnaires without heavy configuration. Scales across teams and vendors ✅ Assesses internal teams and third-party vendors from one place. |
| Limitations | ⚠️ Not designed for legal, audit, or finance teams seeking one platform for enterprise-wide GRC
⚠️ May be too structured for teams looking to build one-off surveys or lightweight audits without repeatable workflows |

UpGuard
UpGuard describes itself as a cyber risk posture management platform. Its security ratings page says its algorithm produces “a security rating out of 950 for all of an organization’s internet-facing web properties,” and its Vendor Risk product lists vendor risk assessments, security questionnaire automation, remediation and exceptions, and continuous monitoring.
Best for: Teams that want an external view of vendor cybersecurity posture, with vendor assessments and questionnaires on the same platform.
| UpGuard | |
| Strengths | ✅ External risk visibility through automated scanning
✅ Lists vendor risk assessments, security questionnaire automation, remediation and exceptions, and continuous monitoring ✅ Its questionnaire library includes SIG Lite, SIG Core, and HECVAT ✅ UpGuard’s blog says its attack surface scanning supports risk registers of cyber threats |
| Limitations | ⚠️ A register for manually logged risks about your own organization is not stated in UpGuard’s help center as of September 2026 |
| Other Comparisons | UpGuard vs Vanta vs Isora GRC
Bitsight vs UpGuard vs Isora GRC UpGuard vs Whistic vs Isora GRC |
Whistic
Whistic helps organizations collect and review vendor security documentation using standard questionnaires and frameworks like SIG, CAIQ, and ISO. Its platform page says teams can “run vendor assessments, monitor change, test internal controls, and answer customer security requests on one agentic platform,” and its Trust Center Exchange lets buyers “instantly view thousands of vendor Trust Centers for faster assessments.”
Best for: Security teams focused on evidence-based vendor reviews, with internal control testing on the same platform.
| Whistic | |
| Strengths | ✅ Its vendor assessments page lists dozens of standard questionnaires and frameworks, such as SIG, CAIQ, and ISO
✅ Trust Center Exchange for faster third-party evaluations ✅ Whistic’s blog says its platform keeps vendor profiles and inventory in a centralized system of record ✅ A Whistic blog post names HECVAT among the more than 40 standard frameworks and questionnaires in its library |
| Limitations | ⚠️ A dedicated exception register is not stated on Whistic’s published surfaces as of September 2026 |
| Other Comparisons | UpGuard vs Whistic vs Isora GRC |
SecurityScorecard
SecurityScorecard gives companies security ratings for vendors by scanning their external digital footprint. Its security ratings page says TITAN AI provides “a transparent, outside-in view of security posture that correlates directly to breach likelihood,” graded on an A-F rating system. It helps prioritize vendors based on their scores.
Best for: Organizations that want a continuous, outside-in view of vendor cybersecurity health through security ratings.
| SecurityScorecard | |
| Strengths | ✅ Real-time score monitoring and alerts for vendor cyber risk
✅ Its third-party risk page lists templated questionnaire management and a centralized system of record that combines manual assessments with automated scanning ✅ SecurityScorecard’s help center documents sending questionnaires to internal teams ✅ Its guide to resolving findings describes a correction path for compensating controls that its outside-in view cannot see |
| Limitations | ⚠️ SecurityScorecard’s guide to resolving findings says its external monitoring “can only verify the effectiveness of public-facing controls,” as of October 2026
⚠️ SecurityScorecard’s pricing page prints no prices for its Watch, Assess, and Secure packages, as of October 2026 |
| Other Comparisons | Bitsight vs SecurityScorecard vs Isora GRC
RiskRecon vs SecurityScorecard vs Isora GRC |
Bitsight
Bitsight provides security ratings that its security ratings page says “are updated daily, incorporating the latest validated data from continuous internet scanning.”
Best for: Security teams that want to track external risk indicators across a large vendor network.
| Bitsight | |
| Strengths | ✅ Security ratings updated daily from continuous internet scanning
✅ Its Vendor Risk Management page says it scales third-party risk management “across thousands of vendors without adding headcount” ✅ Its third-party risk page lists AI-automated assessments mapped to frameworks including SIG Lite, NIST CSF 2.0, HECVAT, and CMMC ✅ Bitsight’s help center documents a Risk Accepted status for findings, with assignees and a status history |
| Limitations | ⚠️ The rating reflects only what the internet can see
⚠️ An internal risk register is not stated on Bitsight’s site or help center as of October 2026 |
| Other Comparisons | Bitsight vs UpGuard vs Isora GRC
Bitsight vs SecurityScorecard vs Isora GRC |
RiskRecon
RiskRecon provides continuous monitoring and security ratings. Its Mastercard page says RiskRecon “directly monitors a company’s web presence,” and RiskRecon also sells questionnaire-based RiskRecon Assessments, powered by Whistic. Its FAQ says RiskRecon “is limited to seeing only externally visible things,” and that the posture an organization presents to the world still says a lot about it.
Best for: Security teams that want to track vendor risk through automated, external cybersecurity scans.
| RiskRecon | |
| Strengths | ✅ Its asset valuation model and customizable risk policies prioritize the findings that matter to each customer
✅ Automatically produces vendor risk action plans and tracks each vendor’s progress on them ✅ RiskRecon Assessments create vendor and SOC 2 summary reports |
| Limitations | ⚠️ Exception tracking and an internal risk register are not stated on the RiskRecon pages checked, as of October 2026 |
| Other Comparisons | RiskRecon vs SecurityScorecard vs Isora GRC |
Panorays
Panorays combines external attack surface assessments with security questionnaires. Its home page says Panorays “evaluates risk across four key areas”: AI-powered questionnaires, external attack surface assessments, each vendor’s inherent risk, and the customer’s own risk policies. It also generates remediation tasks with priorities and deadlines and tracks progress in one view.
Best for: Teams looking for a blend of external security scoring and vendor questionnaires in one platform.
| Panorays | |
| Strengths | ✅ Combines security ratings with questionnaire delivery and response tracking
✅ Its questionnaire page lets customers set the weight of each question and flag questions as “deal-breakers” ✅ Its third-party cyber risk page names NIST CSF, ISO 27001, and SOC 2 among the frameworks it supports |
| Limitations | ⚠️ Exception workflows and an internal asset inventory are not stated on Panorays’ published surfaces as of September 2026 |
| Other Comparisons | Bitsight vs Panorays vs Isora GRC |
OneTrust
OneTrust offers a broad set of tools for managing privacy and third-party risk. Its Third-Party Management solution lists ways to “contextually tier and triage third parties to guide workflow priority and assessment depth,” and to screen “cyber risk ratings and breach activity from RiskRecon, SecurityScorecard, and HackNotice.”
Best for: Organizations focused on vendor privacy compliance, third-party governance, and regulatory documentation.
| OneTrust | |
| Strengths | ✅ Tiers and triages third parties to set workflow priority and assessment depth
✅ Screens cyber risk ratings and breach activity from RiskRecon, SecurityScorecard, and HackNotice ✅ Lists IT risk assessments that engage the business and collect information |
| Limitations | ⚠️ Built privacy-first and extended into GRC, third-party risk, and AI governance, so security risk is one solution among several
⚠️ OneTrust’s pricing page says each solution package has one or more usage meters, as of October 2026 |
| Other Comparisons | OneTrust vs ServiceNow GRC vs Isora GRC |
ProcessUnity
ProcessUnity is a third-party risk management platform. Its platform page says it “unifies the entire third-party risk lifecycle on one platform,” with configurable workflows from initial intake through offboarding.
Best for: Teams focused specifically on third-party risk management with dedicated vendor risk programs in place.
| ProcessUnity | |
| Strengths | ✅ Configurable workflows from initial intake through offboarding
✅ Lists a Cybersecurity Risk Management solution with an enterprise cyber risk register and a controls library mapped to 1,000+ control standards, including NIST CSF, NIST 800-53, and ISO 27001 |
| Limitations | ⚠️ Positioned primarily as a third-party risk platform
⚠️ HECVAT is not named on the ProcessUnity pages checked, as of October 2026 |
| Other Comparisons | ProcessUnity vs Allgress vs Isora GRC |
What Customers Say About Isora GRC
Security teams use Isora GRC to replace manual processes with intuitive workflows and actionable insight.
SaltyCloud makes Isora GRC, one of the products compared here. The assessments are our own, so confirm current features and pricing with each vendor before you decide.
FAQs
What is IT vendor risk management software, and why do organizations need it?
IT vendor risk management software helps a security team assess, track, and manage the security risks that come with third-party vendors. It keeps a vendor inventory, sends security questionnaires, collects evidence, scores responses, and records findings until they close. Some regulations call for this oversight. The FTC’s Safeguards Rule, for example, requires financial institutions under its jurisdiction to oversee service providers, including by periodically assessing them “based on the risk they present and the continued adequacy of their safeguards.” Isora GRC’s vendor risk page says it connects vendor questionnaires, inventory records, and risk data in one workspace, so responses, evidence, and findings stay traceable to the vendor they describe.
Why is evidence like a SOC 2 report important when evaluating vendor risk?
Questionnaire answers describe a vendor’s controls in the vendor’s own words. Documents such as a SOC 2 report or an ISO 27001 certificate give the reviewer evidence to check those answers against, and the team can record what it reviewed and accepted. Several platforms on this page support this step. Bitsight’s Vendor Risk Management page lists reviewing uploaded documents, including SOC 2 and ISO 27001 certifications, in one place, and RiskRecon Assessments create SOC 2 summary reports. In Isora GRC, vendors upload evidence alongside each question, and findings are published to the risk register with lineage back to the question that identified the gap.
What is the difference between high-risk and low-risk vendors?
A vendor’s risk level reflects what it can reach, such as the sensitivity of the data it handles and how much the organization depends on its service. Tiering lets a program match the depth of each review to that risk, which is also how the FTC’s Safeguards Rule frames service provider assessments: “based on the risk they present.” Bitsight’s Vendor Risk Management page tells customers to build tiered questionnaire sets “for different vendor criticality levels,” and OneTrust’s Third-Party Management solution lists tiering third parties “to guide workflow priority and assessment depth.” Isora GRC’s vendor risk page says vendors can be organized into groups such as risk tiers or a separate track for AI and LLM vendors, and tagged with status labels like contract in place or GLBA scope.
How does vendor inventory management support third-party risk workflows?
A vendor inventory is the list the rest of the program works from. Whistic’s blog defines it as “a complete list of every third-party your organization is working with.” When each record also holds assessment results, contracts, data classifications, and open findings, the team can see which vendors are due for review and which carry open risk. Isora GRC keeps one record per vendor with its history, covering assessment results, product deployments across organizational units, data classifications, contacts, contracts, risk ratings, and exception documentation.
Is a security rating the same as a vendor risk assessment?
No. A security rating scores a vendor from what can be observed from outside. SecurityScorecard’s guide to resolving findings says its external monitoring “can only verify the effectiveness of public-facing controls,” and RiskRecon’s FAQ says RiskRecon “is limited to seeing only externally visible things.” A vendor risk assessment records what the vendor said, the evidence it provided, and what the team accepted. The two are different jobs, and several ratings platforms on this page also sell questionnaire workflows, such as Bitsight’s Vendor Risk Management product, SecurityScorecard’s TITAN Assess, and RiskRecon Assessments. Where the main problem is vendors rather than internal units, a dedicated vendor risk platform adds continuous external monitoring, larger questionnaire libraries, and portfolio reporting. Isora GRC’s vendor risk page treats external ratings and risk signals as one input and says monitoring tools and Isora can work together.
For a framework to evaluate GRC platforms before a demo, download our GRC Buyer’s Guide for Information Security Teams.


This content is for informational purposes only and does not constitute legal or compliance advice. See our full disclaimer.
