




Hyperproof Alternatives: Compare GRC Platforms for IT and Vendor Risk
Hyperproof is a modern compliance operations platform designed to simplify frameworks like SOC 2, ISO 27001, and NIST. It helps teams collect evidence, manage tasks, and stay audit-ready. Its Risk Management product lists a risk register, risk assessments and continuous risk monitoring.
For security teams tasked with assessing vendors, tracking internal risk, or managing exceptions, Hyperproof’s pages list vendor assessments and a risk register. Hyperproof’s Policy Management product also lists policy exception tracking, including who requested and who accepted each exception.
Hyperproof describes itself as an AI-powered GRC platform, with products for compliance, risk management, audit, third-party risk and policy management.
Why Teams Look for Hyperproof Alternatives
Teams look for an alternative to Hyperproof after running into one or more common limitations.
| Common Limitation | Why It’s a Problem | What to Look for Instead |
| Built for multi-framework compliance programs | HECVAT is not among the frameworks listed on Hyperproof’s frameworks page, as of October 2026 | Purpose-built for IT and third-party risk workflows |
What to Look for in a Hyperproof Alternative
When evaluating a Hyperproof alternative, the factors an organization can consider depend on its use case. Still, here’s what an alternative should cover:
- Tools for running internal and external assessments
- Built-in exception tracking and centralized risk registers
- Support for vendor inventories and third-party risk assessments
- A platform that enables collaboration, not just documentation
- Designed to support the full risk lifecycle—not just audits
Make sure to ask potential vendors about each of these capabilities, before you sign a contract.
Top Hyperproof Alternatives
Hyperproof vs. Isora GRC
Isora GRC is the GRC Assessment Platform™ built specifically for information security teams. It supports the full risk workflow, from assessments and questionnaires to risks, inventory, and reporting.
Best for: Security teams that need to operationalize IT and third-party risk management across assets, third-party vendors, and business units.
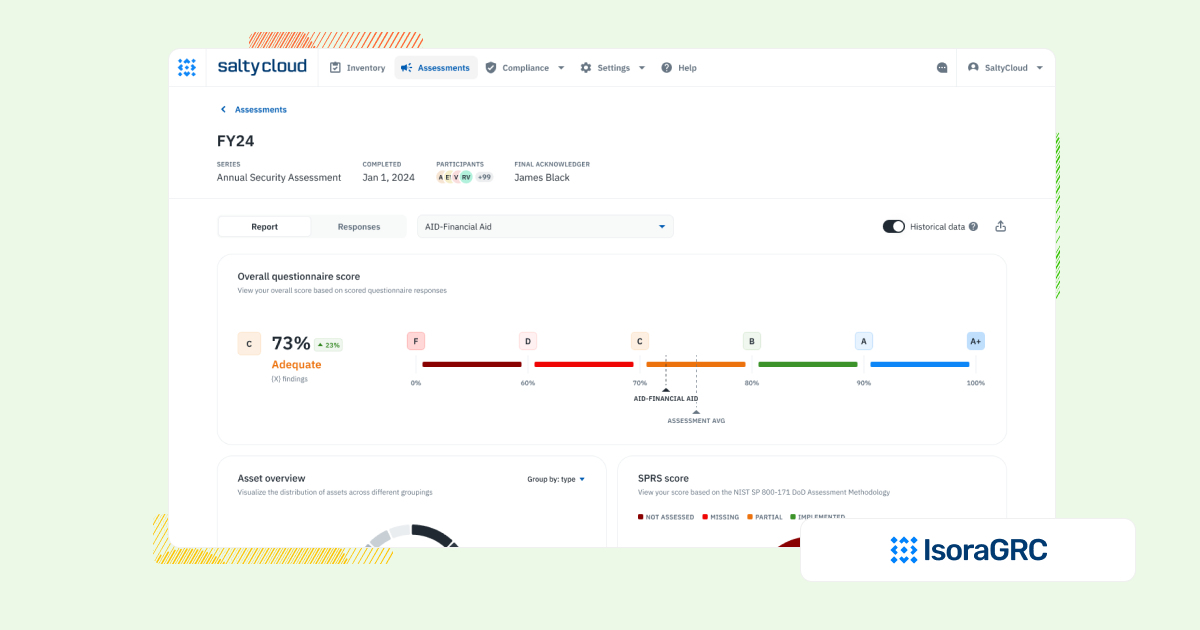
| Isora GRC | |
| Strengths | Built for workflows, not checklists
✅ Supports assessments, inventory tracking, risk registers, and exceptions in a unified experience. Designed for org-wide adoption ✅ WCAG-compliant UX built for respondents outside security, which makes risk everyone’s job. Fast time-to-value ✅ Live in days or weeks, with no-code setup and minimal lift from IT. Flexible by default ✅ Customizable assessments and framework-aligned questionnaires without heavy configuration. Scales across teams and vendors ✅ Assesses internal teams and third-party vendors from one place. |
| Limitations | ⚠️ Not designed for legal, audit, or finance teams seeking one platform for enterprise-wide GRC
⚠️ May be too structured for teams looking to build one-off surveys or lightweight audits without repeatable workflows |
Hyperproof vs. Drata
Drata is a compliance automation tool built to help companies streamline audits. It offers strong integrations and evidence collection, and its help center documents a risk register, risk assessments and vendor security reviews. Its help center also documents personnel exclusions for approved compliance exceptions, with a business rationale and an optional end date.
Best for: Startups and growing teams that want to automate SOC 2, ISO 27001, and similar frameworks.
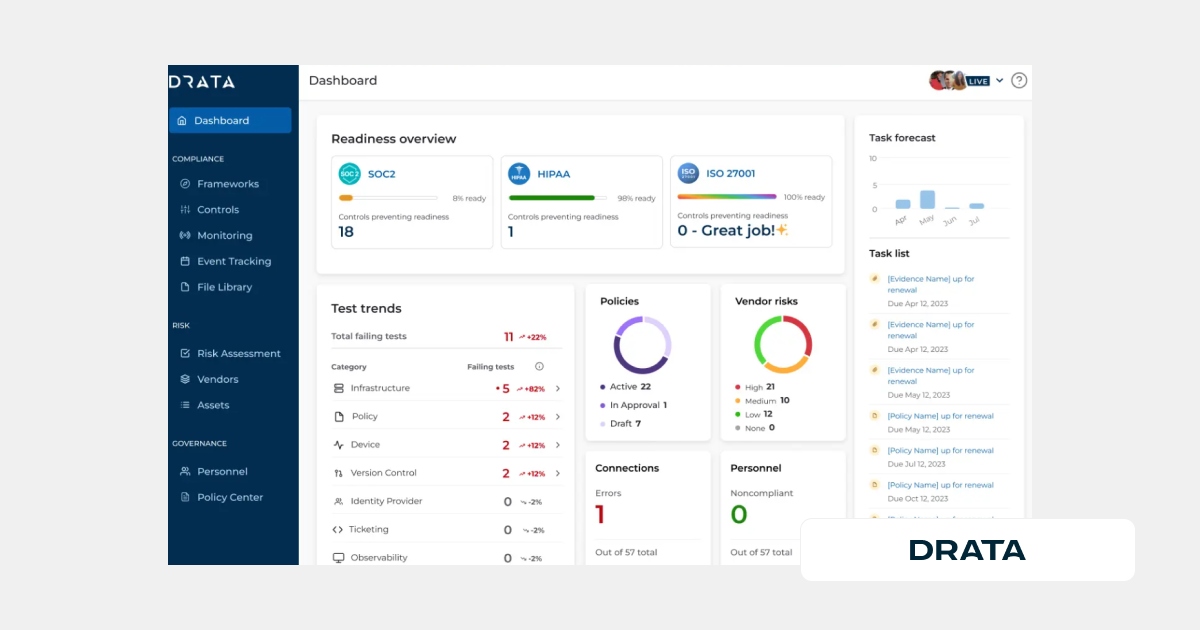
| Drata | |
| Strengths | ✅ Fast-track audit prep with automated control monitoring
✅ Supports multiple frameworks including SOC 2, ISO, and HIPAA ✅ Drata’s help center documents assets, risk registers and vendor reviews, as of September 2026 ✅ Drata’s help center documents exclusions that record approved compliance exceptions with a business rationale, as of September 2026 |
| Limitations | ⚠️ Drata’s published framework list leaves out HECVAT, GLBA, TX-RAMP and StateRAMP/GovRAMP, as of October 2026
⚠️ Pricing runs across two platform tracks plus add-on modules, so a quote has to be read line by line |
| Other Comparisons | Drata vs OneTrust vs Isora GRC |
Hyperproof vs. Vanta
Vanta helps companies automate audit evidence collection and meet compliance goals. Like Hyperproof, it helps teams get ready for compliance audits. Its Risk Management product lists a risk register with owners and treatment plans, and its Third Party Risk Management product lists a vendor inventory.
Best for: Small teams and startups looking to get compliant fast with minimal manual work.
| Vanta | |
| Strengths | ✅ Automated integrations and fast audit preparation
✅ Templates for frameworks like SOC 2 and ISO 27001 ✅ Lists continuous risk monitoring and third-party risk management, and Vanta’s ISO 27001 page lists routing exceptions for approval, as of September 2026 |
| Limitations | ⚠️ Vanta’s published framework list leaves out HECVAT, GLBA, TX-RAMP and StateRAMP/GovRAMP, as of October 2026
⚠️ Vanta’s help center lists risk registers by business unit as an Advanced Risk Management feature, available only as an upgrade or add-on, as of October 2026 |
| Other Comparisons | OneTrust vs Vanta vs Isora GRC |
Hyperproof vs. Optro
Optro (formerly AuditBoard) is built to help audit and compliance teams manage controls and prepare for audits. It is useful for documentation and SOX. Its Cyber Risk Management and TPRM products list asset-level assessments, vendor questionnaires and risk acceptance with documented sign-offs.
Best for: Internal audit teams focused on tracking controls, collecting evidence, and managing audits.
| Optro | |
| Strengths | ✅ Simple, effective tools for control documentation and audit workflows
✅ Ideal for SOX and internal audit teams ✅ Lists Cyber Risk Management and TPRM products, with asset inventories, configurable risk assessments and risk acceptance with sign-offs, as of September 2026 |
| Limitations | ⚠️ Optro’s pricing page asks buyers to request pricing and lists no price, as of October 2026
⚠️ HECVAT is not named on the Optro product pages checked, as of October 2026 |
| Other Comparisons | AuditBoard vs ServiceNow GRC vs Isora GRC |
Hyperproof vs. OneTrust GRC
OneTrust GRC extends its privacy platform with governance and vendor risk features. It also lists IT risk management with real-time risk mapping, an asset inventory, and policy exception tracking with automated follow-up.
Best for: Legal and compliance teams managing privacy frameworks, vendor risk documentation, and regulatory reporting.
| OneTrust GRC | |
| Strengths | ✅ Supports privacy compliance and vendor risk documentation
✅ Includes out-of-the-box templates for third-party risk assessments ✅ Lists IT risk management with real-time risk mapping, plus risk assessments, exception tracking and owners across internal and external teams, as of September 2026 |
| Limitations | ⚠️ OneTrust’s pricing page says each solution package has one or more usage meters, as of October 2026 |
| Other Comparisons | OneTrust vs ServiceNow GRC vs Isora GRC |
Hyperproof vs. LogicGate
LogicGate is a flexible, no-code platform that allows teams to design their own GRC workflows. It can be adapted to many risk use cases, and its Applications catalog lists cyber risk, third-party risk and exceptions management applications.
Best for: Teams that want full control over their risk workflows.
| LogicGate | |
| Strengths | ✅ Customizable workflows for IT, vendor, and compliance risk programs
✅ Supports frameworks like NIST and ISO with flexible mapping ✅ Lists prebuilt applications for cyber risk, exceptions management and third-party risk, as of September 2026 |
| Limitations | ⚠️ Prebuilt cyber and third-party risk Applications are licensed separately and run by Power Users, whom LogicGate calls platform administrators |
| Other Comparisons | LogicGate vs Archer IRM vs Isora GRC |
Hyperproof vs. ZenGRC
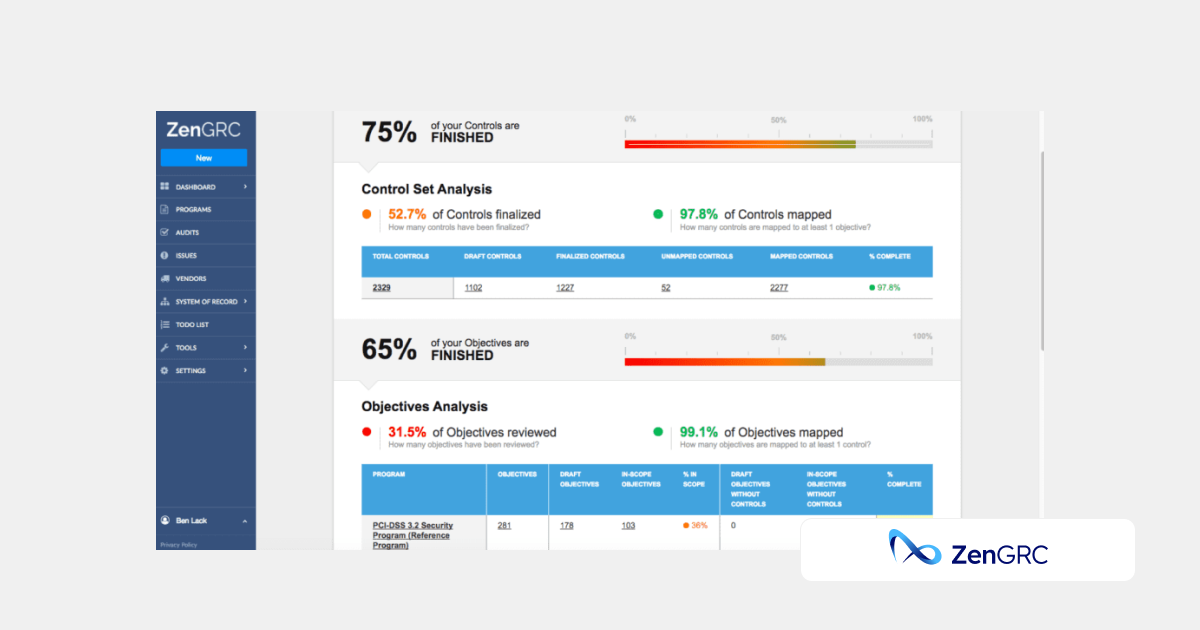
ZenGRC is a GRC platform for managing audits and organizing compliance evidence. It also lists Risk Management and Vendor Management modules with automated workflows. ZenGRC’s API documentation lists Data Assets, Systems and Exceptions objects, as of September 2026.
Best for: Small teams starting out with compliance tracking and audit readiness.
| ZenGRC | |
| Strengths | ✅ Simple setup and UI for compliance documentation
✅ Templates for SOC 2, ISO 27001, and other common frameworks ✅ Lists Risk Management and Vendor Management modules, as of September 2026 |
| Limitations | ⚠️ ZenGRC does not publish a fixed public price list. Its pricing post says each quote is a custom single flat rate with no separate fees for users, frameworks, or vendors, as of October 2026 |
| Other Comparisons | ZenGRC vs AuditBoard vs Isora GRC |
Hyperproof vs. Onspring
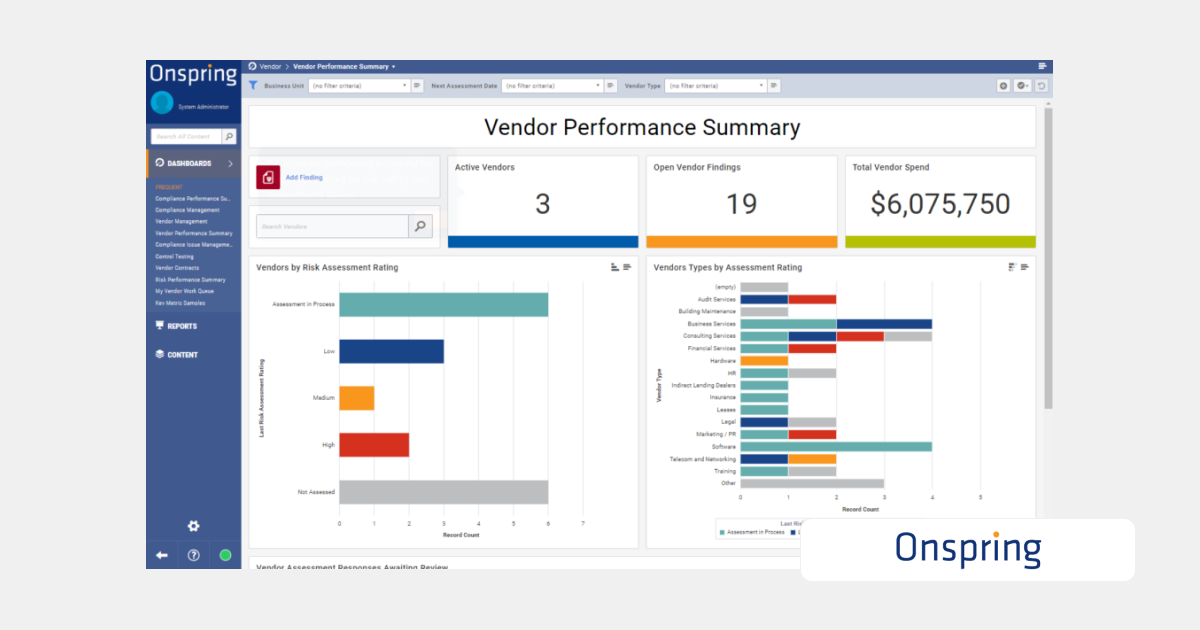
Onspring offers a no-code platform to design custom governance workflows. It lists Risk Management and Third-Party Risk Management products, with automated risk assessment workflows and exception and risk acceptance management. Onspring states that prebuilt risk register content for your industry is not included.
Best for: Legal, audit, or compliance teams that need a customizable, no-code GRC platform.
| Onspring | |
| Strengths | ✅ Customizable for a wide range of GRC use cases
✅ No-code environment ideal for non-technical process owners ✅ Lists Risk Management and Third-Party Risk Management products |
| Limitations | ⚠️ Onspring’s FAQ says it does not include risk register content for your industry, as of October 2026 |
| Other Comparisons | Onspring vs AuditBoard vs Isora GRC |
Hyperproof vs. Archer IRM
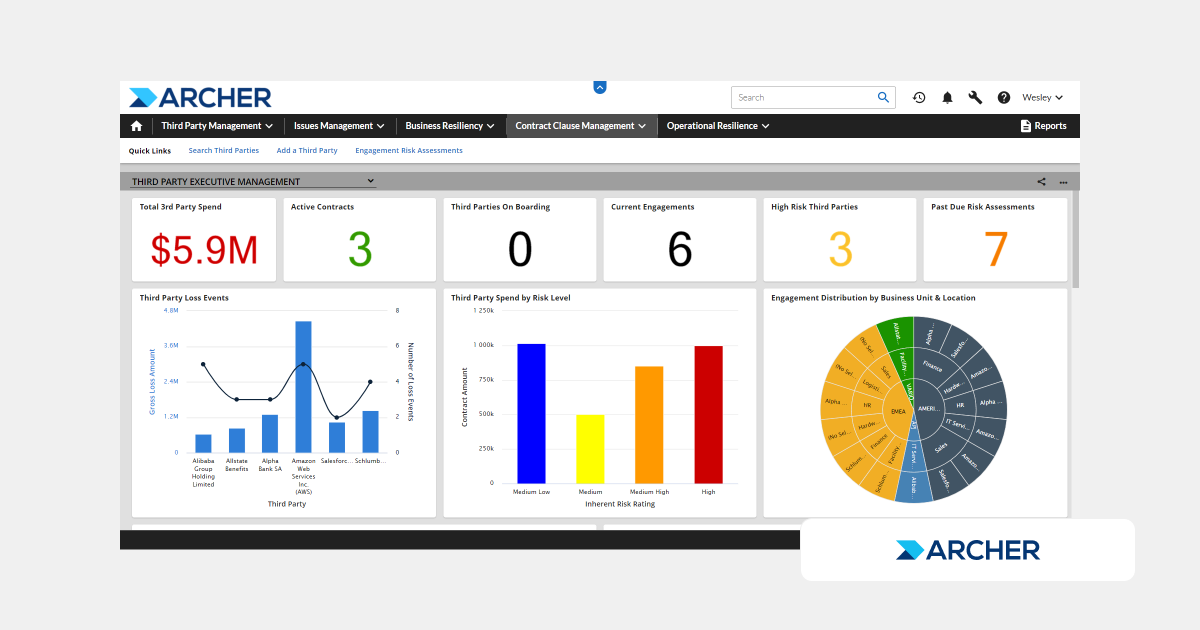
Archer IRM is an enterprise GRC platform known for its configurability and regulatory alignment. It supports audits, and it lists IT and security risk management with a risk register, plus third-party governance with vendor questionnaires.
Best for: Large enterprises managing broad GRC programs with formal audit and compliance oversight.
| Archer IRM | |
| Strengths | ✅ Enterprise-grade governance capabilities across compliance, audit, and risk
✅ Lists industry solutions for financial services, healthcare, energy, and the public sector ✅ Lists IT risk and vendor management workflows, and Archer’s pricing page lists exceptions tracked to expiry, as of September 2026 |
| Limitations | ⚠️ Archer says pricing scales with modules, users, and deployment model, as of October 2026 |
| Other Comparisons | Archer IRM vs ServiceNow GRC vs Isora GRC
LogicGate vs Archer IRM vs Isora GRC ZenGRC vs Archer IRM vs Isora GRC |
What Customers Say About Isora GRC
Security teams use Isora GRC to replace manual processes with intuitive workflows and actionable insight.
SaltyCloud makes Isora GRC, one of the products compared here. The assessments are our own, so confirm current features and pricing with each vendor before you decide.
FAQs
What are some alternatives to Hyperproof?
Hyperproof is part of the compliance automation category—tools that help manage audits and framework alignment. Alternatives like Isora GRC provide structured workflows for internal and vendor risk assessments, exception tracking, and collaborative risk management across the organization.
Why do teams switch from Hyperproof to platforms like Isora GRC?
Hyperproof helps with evidence collection and audit prep, and it also lists vendor assessments, a risk register and policy exception tracking as of September 2026. Isora GRC offers tools designed for IT and third-party risk.
Does Isora GRC replace tools like Hyperproof or complement them?
Isora GRC fits teams that need to assess the departments and systems the security team does not operate, and it can run alongside a compliance automation platform like Hyperproof. Isora connects assessment delivery, risk tracking, and remediation in one workspace.
Which platform is better for tracking exceptions and third-party risk?
Hyperproof lists policy exception tracking and a third-party risk management product with AI-assisted vendor assessments as of September 2026. Isora GRC was built for both—providing workflows for logging, assigning, and resolving exceptions while also managing vendor inventories and third-party risk assessments.
What should I look for in a Hyperproof alternative?
Look for a platform that supports risk workflows, not just audit tasks. Key features include internal and external assessments, risk registers, exception tracking, and organization-wide collaboration. Isora GRC is designed to support all of that without heavy configuration.
For a framework to evaluate GRC platforms before a demo, download our GRC Buyer’s Guide for Information Security Teams.


This content is for informational purposes only and does not constitute legal or compliance advice. See our full disclaimer.
 Other Relevant Content
