




Whistic Alternatives: Compare Platforms for Vendor and Third-Party Risk
Whistic is designed to streamline the exchange of security questionnaires between companies and vendors. It’s useful for sharing profiles and answering assessments quickly, and it also lists vendor assessments, continuous monitoring, and internal control testing.
Whistic runs vendor assessments and manages internal controls on the same platform. Whistic’s blog says its platform keeps vendor profiles and inventory in a centralized system of record. A dedicated exception register is not stated on Whistic’s published surfaces as of September 2026.
Whistic describes its platform as running the full risk lifecycle as one connected workflow, including a Trust Center for document sharing.
Why Teams Look for Whistic Alternatives
Teams look for an alternative to Whistic after running into one or more common limitations.
| Common Limitation | Why It’s a Problem | What to Look for Instead |
| Inventory scoped to third parties | Whistic’s blog defines the vendor inventory as “a complete list of every third-party your organization is working with,” as of October 2026 | One inventory of vendors, internal systems, and departments with integrated risk tracking |
| Exceptions sit inside assessment decisions | A dedicated exception register is not stated on Whistic’s published surfaces as of September 2026 | Exception management tied to both internal and vendor risk |
What to Look for in a Whistic Alternative
When evaluating a Whistic alternative, the factors an organization can consider depend on its use case. Still, here’s what an alternative should cover:
- Ability to send and manage vendor assessments across frameworks (SIG, HECVAT, etc.)
- Centralized vendor inventories and issue tracking
- Exception workflows that help teams resolve risk—not just identify it
- Tools that support both third-party and internal security workflows
- Collaboration features that increase visibility and accountability across the organization
Make sure to ask potential vendors about each of these capabilities, before you sign a contract.
Top Whistic Alternatives
Whistic vs. Isora GRC
Isora GRC is the GRC Assessment Platform™ built specifically for information security teams. It supports the full risk workflow, from assessments and questionnaires to risks, inventory, and reporting.
Best for: Security teams that need to operationalize IT and third-party risk management across assets, third-party vendors, and business units.
| Isora GRC | |
| Strengths | Built for workflows, not checklists
✅ Supports assessments, inventory tracking, risk registers, and exceptions in a unified experience. Designed for org-wide adoption ✅ WCAG-compliant UX built for respondents outside security, which makes risk everyone’s job. Fast time-to-value ✅ Live in days or weeks, with no-code setup and minimal lift from IT. Flexible by default ✅ Customizable assessments, scalable categories, and framework-aligned questionnaires without heavy configuration. Scales across teams and vendors ✅ Assesses internal teams and third-party vendors from one place. |
| Limitations | ⚠️ Not designed for legal, audit, or finance teams seeking one platform for enterprise-wide GRC
⚠️ May be too structured for teams looking to build one-off surveys or lightweight audits without repeatable workflows |

Whistic vs. UpGuard
UpGuard helps monitor vendors using automated scanning and external risk scoring. It’s useful for identifying surface-level risk, and it also lists vendor risk assessments, questionnaire automation, and remediation tracking.
Best for: Security teams that want fast, external views of vendor risk posture.
| UpGuard | |
| Strengths | ✅ External risk visibility through automated scanning
✅ Easy to get started for surface-level monitoring ✅ UpGuard’s blog says its attack surface scanning supports risk registers of cyber threats |
| Limitations | ⚠️ A register for manually logged risks about your own organization is not stated in UpGuard’s help center as of September 2026 |
| Other Comparisons | UpGuard vs Vanta vs Isora GRC
Bitsight vs UpGuard vs Isora GRC UpGuard vs Whistic vs Isora GRC |
Whistic vs. SecurityScorecard
SecurityScorecard monitors vendors from the outside in to generate risk scores. It’s great for spotting third-party risk trends, and it also lists templated questionnaires and Action Plans that assign owners and track progress.
Best for: Organizations that want to continuously track external vendor risk using automated ratings.
| SecurityScorecard | |
| Strengths | ✅ Real-time vendor scoring with broad coverage
✅ Integrates easily into procurement workflows |
| Limitations | ⚠️ Exception workflows are not stated on SecurityScorecard’s published surfaces as of September 2026 |
| Other Comparisons | Bitsight vs SecurityScorecard vs Isora GRC
RiskRecon vs SecurityScorecard vs Isora GRC |
Whistic vs. Bitsight
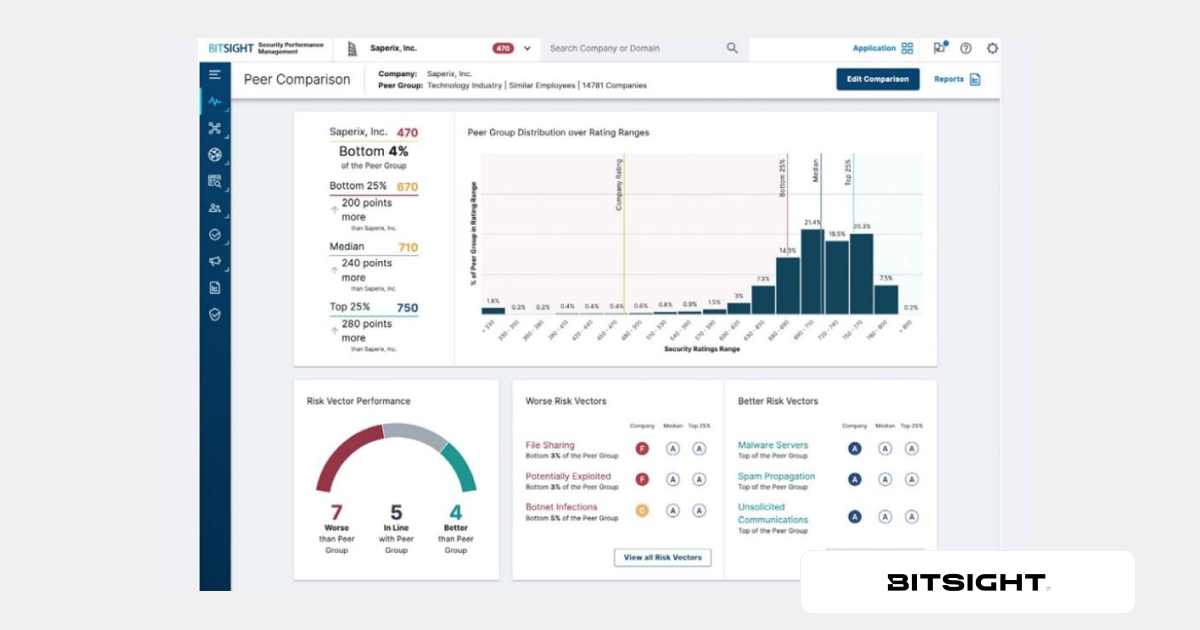
Bitsight provides external security ratings and benchmarks vendor posture across risk categories. It’s good for surface-level monitoring, and it also lists vendor assessments, a third-party inventory, and remediation tracking.
Best for: Teams that want to evaluate vendors based on external cybersecurity posture and score comparisons.
| Bitsight | |
| Strengths | ✅ Clear, standardized security ratings across thousands of vendors
✅ Easy to incorporate into risk reporting and procurement processes ✅ Bitsight’s help center documents a Risk Accepted status for findings, with assignees and a status history |
| Limitations | ⚠️ An internal risk register is not stated on Bitsight’s site or help center as of September 2026 |
| Other Comparisons | Bitsight vs UpGuard vs Isora GRC
Bitsight vs SecurityScorecard vs Isora GRC |
Whistic vs. RiskRecon
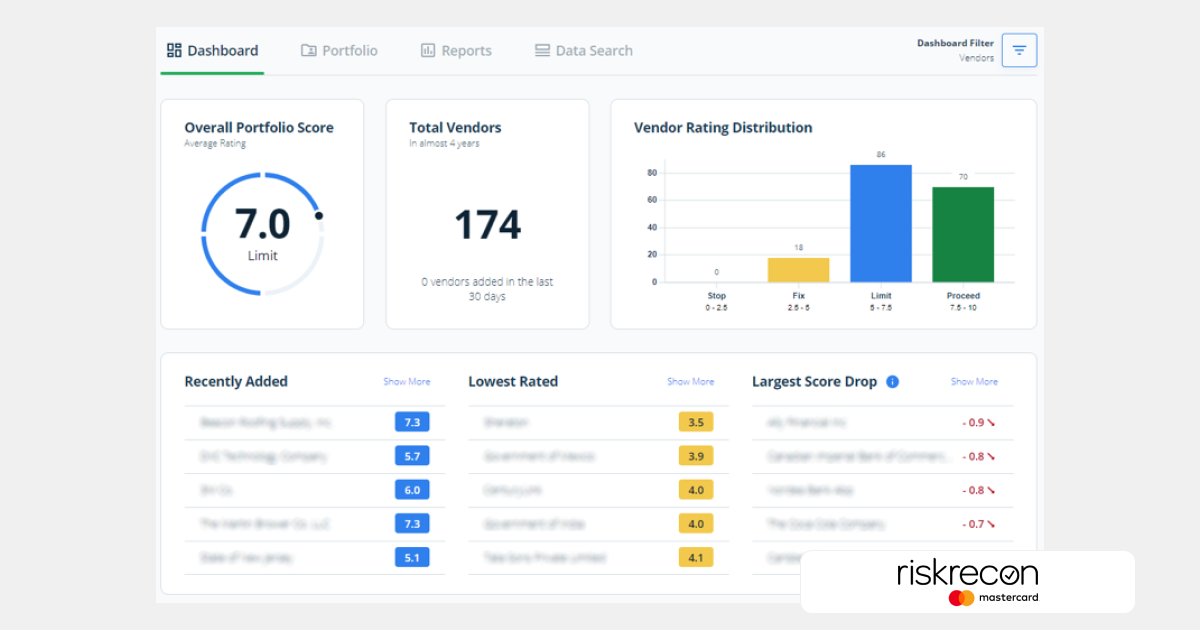
RiskRecon uses externally visible data to provide vendor cyber risk ratings. It’s useful for monitoring changes in external posture, and it also sells questionnaire-based RiskRecon Assessments and produces vendor risk action plans.
Best for: Security teams that need quick external snapshots of vendor risk.
| RiskRecon | |
| Strengths | ✅ Continuous vendor scoring with risk prioritization
✅ Simple and visual risk summaries |
| Limitations | ⚠️ Internal workflows and exception management are not stated on RiskRecon’s published surfaces as of September 2026 |
| Other Comparisons | RiskRecon vs SecurityScorecard vs Isora GRC |
Whistic vs. Panorays
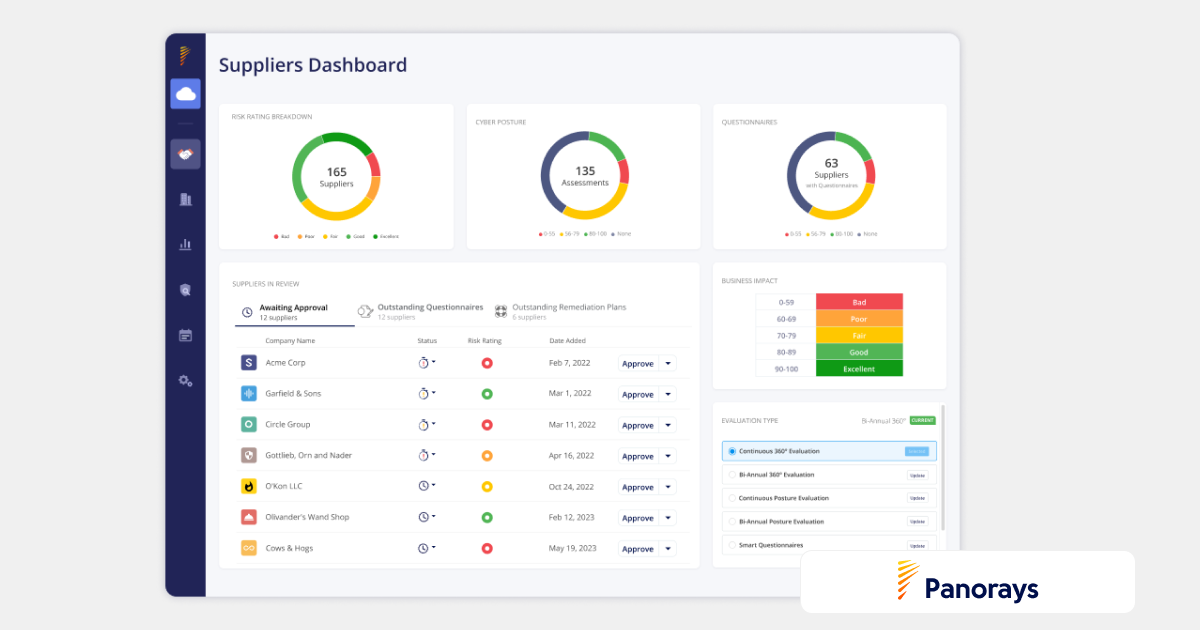
Panorays combines external vendor risk monitoring with customizable questionnaires. It helps teams onboard vendors and check surface-level security posture, and it generates remediation tasks with priorities and deadlines.
Best for: Organizations that want to pair external vendor scores with customizable vendor questionnaires.
| Panorays | |
| Strengths | ✅ Merges ratings with built-in assessment questionnaires
✅ Speeds up vendor onboarding and initial reviews |
| Limitations | ⚠️ Exception workflows and an internal asset inventory are not stated on Panorays’ published surfaces as of September 2026 |
| Other Comparisons | Bitsight vs Panorays vs Isora GRC |
Whistic vs. Black Kite
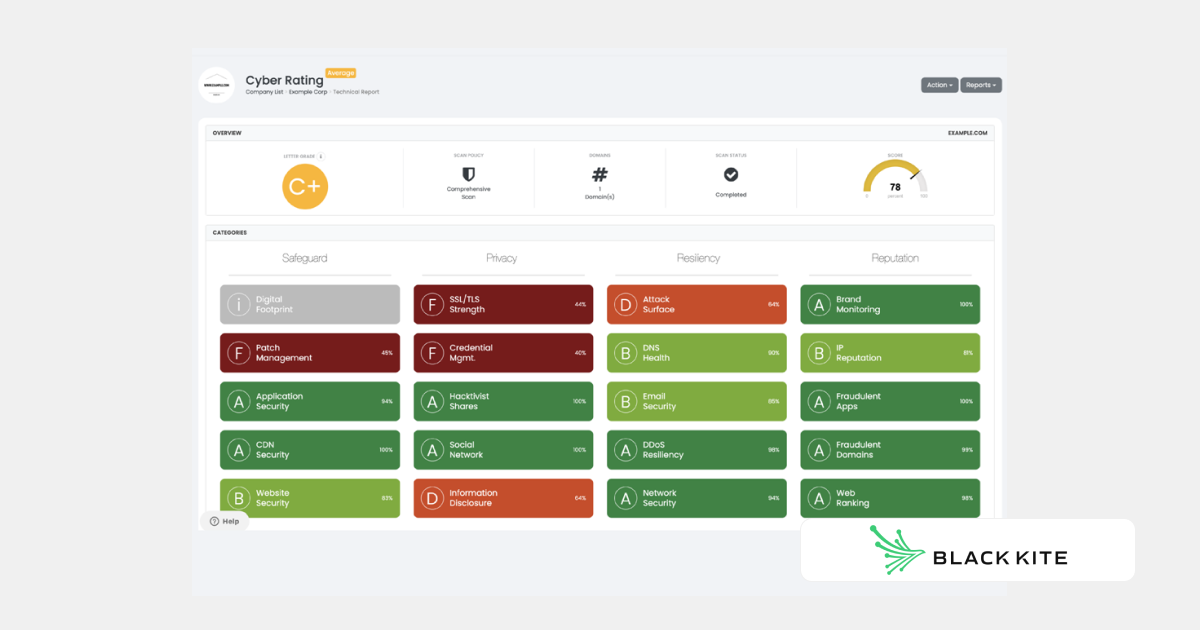
Black Kite gives vendors external security ratings and estimates the potential financial impact of a cyber attack. It also lists AI questionnaire management and a vendor inventory.
Best for: Teams that want to translate vendor cyber risk into business impact terms like financial exposure.
| Black Kite | |
| Strengths | ✅ Business-focused vendor risk scoring
✅ Quantifies financial exposure using Open FAIR™ methodologies |
| Limitations | ⚠️ Internal assessments and exception handling are not stated on Black Kite’s published surfaces as of September 2026 |
| Other Comparisons | Black Kite vs Bitsight vs Isora GRC |
Whistic vs. Prevalent
Prevalent, now a Mitratech product, is a full-featured vendor risk management platform that combines assessments, continuous monitoring, and remediation. It goes beyond surface-level scoring and supports deeper workflows.
Best for: Organizations that want to issue assessments, collect evidence, and monitor vendor risk all in one place.
| Prevalent | |
| Strengths | ✅ Issues vendor questionnaires and tracks remediation
✅ Includes pre-built templates and external threat data |
| Limitations | ⚠️ Focused on vendor risk, not broader internal risk workflows |
Whistic vs. ProcessUnity
ProcessUnity helps organizations manage onboarding, due diligence, assessments, and ongoing monitoring in one platform. It’s structured and scalable.
Best for: Security and risk teams looking to centralize and automate vendor risk across the full lifecycle.
| ProcessUnity | |
| Strengths | ✅ Supports vendor assessments and remediation tracking
✅ Scalable for mature TPRM programs with custom workflows ✅ Lists a Cybersecurity Risk Management solution for internal programs |
| Limitations | ⚠️ Positioned primarily as a third-party risk platform
⚠️ HECVAT is not named on the ProcessUnity pages checked, as of October 2026 |
| Other Comparisons | ProcessUnity vs Allgress vs Isora GRC |
What Customers Say About Isora GRC
Security teams use Isora GRC to replace manual processes with intuitive workflows and actionable insight.
SaltyCloud makes Isora GRC, one of the products compared here. The assessments are our own, so confirm current features and pricing with each vendor before you decide.
FAQs
What are some alternatives to Whistic?
Whistic is a third-party risk platform that runs vendor assessments, tests internal controls, and shares security profiles through a Trust Center. Alternatives like Isora GRC let security teams send assessments, collect responses, track exceptions, and maintain centralized vendor inventories.
Why do teams switch from Whistic to platforms like Isora GRC?
Whistic runs vendor assessments through a staged review workflow that routes each assessment to internal approvers. Isora GRC fits teams that need control over assessment delivery, risk tracking, and remediation follow-up.
Does Isora GRC replace tools like Whistic or complement them?
Isora GRC fits teams that assess vendors alongside their own departments and systems. Isora enables you to issue assessments, maintain vendor records, log exceptions, and collaborate with internal stakeholders—all in one platform.
Which platform is better for tracking vendor risk across the organization?
Whistic lets teams collaborate with internal stakeholders on vendor reviews. Whistic’s blog says its platform keeps vendor profiles and inventory in a centralized system of record. Isora GRC is built for information security teams, with questionnaires written for respondents outside security.
What should I look for in a Whistic alternative?
A strong alternative should let you assess vendors, track risks and exceptions, maintain an inventory, and collaborate across teams. Isora GRC delivers all of that in one streamlined platform.
For a framework to evaluate GRC platforms before a demo, download our GRC Buyer’s Guide for Information Security Teams.


This content is for informational purposes only and does not constitute legal or compliance advice. See our full disclaimer.
 Other Relevant Content
