IT Risk Management Software for Banks and Credit Unions
The GRC Assessment Platform™ for banks and credit unions

Isora GRC gives security teams one connected workspace to operationalize regulatory compliance for banks and credit unions, with assessments mapped to the GLBA Safeguards Rule, FFIEC guidance, and NIST, service provider inventories and due diligence records, risk tracking through remediation, and examination-ready reporting drawn from that same record, all in one place.

Trusted by established organizations & partners
https://vt.eduhttps://www.af.milhttps://utexas.eduhttps://yale.eduhttps://www.tdi.texas.govhttps://www.ttuhsc.eduhttps://aws.amazon.comhttps://www.osu.eduhttps://www.wilcotx.govhttps://www.utoronto.cahttps://www.tdcj.texas.govhttps://www.uchicago.edu/enhttps://www.utah.eduhttps://dir.texas.govhttps://www.dps.texas.govhttps://www.berkeley.eduhttps://www.techstars.comhttps://cccs.eduhttps://www.iwu.eduhttps://msu.eduhttps://www.auburn.eduhttps://www.stthomas.eduhttps://www.getezmoney.comhttps://www.sait.cahttps://www.ubc.cahttps://www.cuanschutz.eduhttps://www.tjc.eduhttps://marymount.eduhttps://www.umt.eduhttps://www.pdx.eduhttps://www.tccd.eduhttps://ltu.eduhttps://morantechnology.comhttps://www.merit.eduhttps://www.tccd.eduhttps://www.gonzaga.eduhttps://www.bhc.eduhttps://www.dallascollege.edu

Problem

Banks and credit unions manage several frameworks at once

Banks and credit unions face requirements from the GLBA Safeguards Rule, FFIEC guidance, PCI-DSS, NIST frameworks, and state rules like NYDFS 23 NYCRR 500 at once. But the assessments, vendor questionnaires, and risk register that serve them are maintained separately. Often, assembling proof for an examination takes days or weeks.
Solution

One platform for the IT risk management lifecycle
Isora GRC brings the compliance workflows financial organizations need into one workspace, with regulatory assessments, vendor oversight, risk tracking, and examination reporting. In Isora, the compliance record is a byproduct of doing the work, so tracing a finding from assessment through remediation to current status draws from live data.
Assessment Management
Assess against GLBA, FFIEC, and NIST on a recurring cycle

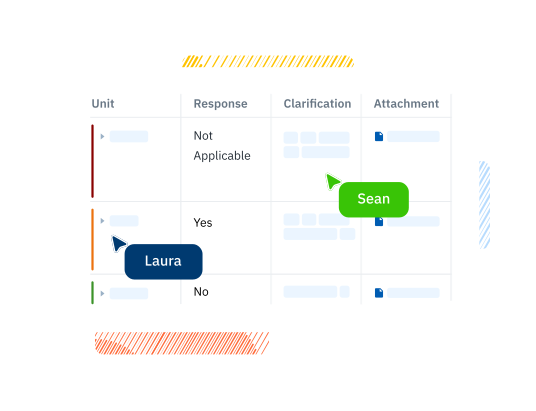
Launch assessments using prebuilt GLBA and NIST questionnaires mapped to Safeguards Rule requirements, with custom questionnaires for FFIEC guidance and PCI-DSS. Target every department, branch, and system that handles customer financial information, and collect evidence inline so any response traces back to its supporting documentation. In Isora, recurring cycles keep assessments running between examinations.
Learn More
Inventory Management
Document vendor oversight for examiners

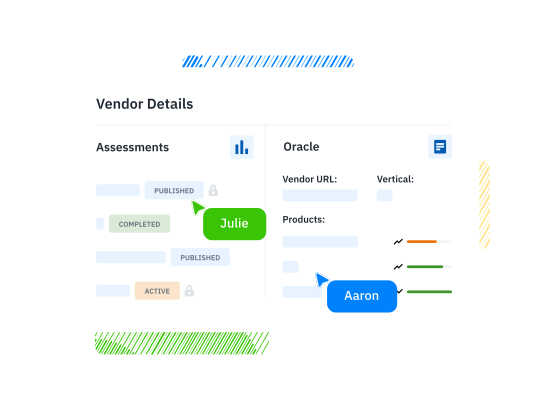
Maintain a vendor inventory with linked questionnaires, assessment results, risk ratings, and contract documentation, where each record carries its assessment history, product deployments, and data classifications. When examiners ask which vendors access customer PII and when they were last assessed, the answer is just one search away.
Learn More
Risk Management
Track risks from examination to documented remediation

Document risks, assign owners, set due dates, and track mitigation efforts with a unified register that improves visibility and accountability across teams.

Learn More
Reports & Scorecards
Report live data at examinations

Generate reports showing assessment completion, control effectiveness, risk ratings, and remediation progress across the institution, and share them with examiners, auditors, the board, or compliance committees. In Isora, the numbers are always current because they pull from live assessment data.

Learn More
Let’s Chat
See the GRC Assessment Platform in action
Isora GRC is the GRC Assessment Platform™ that gives security teams one connected workspace to run assessments, manage vendors and assets, track risks, and prove compliance.
Book a Demo
Latest News
Our latest content
Stay ahead of the curve with our latest research on a diverse range of topics exploring the ever-changing world of governance, risk, and compliance.

GLBA Safeguards Rule: What It Requires and How to Comply The GLBA Safeguards Rule is the most operationally demanding component of the...

GLBA Compliance Checklist: Everything You Need to Track A GLBA compliance checklist is a structured tracking tool that helps financial institutions...

Third-Party Risk Management Software: Tools, Platforms & How to Choose Third-party risk management (TPRM) software is the system a security...

Third-Party Risk Management Frameworks: How to Build and Govern a TPRM Program A third-party risk management (TPRM) framework is the structure an...

Vendor Risk Assessment: How to Evaluate Third-Party Risk A vendor risk assessment is the process of evaluating the security, financial, operational,...

Supplier Risk Management: How to Assess, Tier, and Monitor Supplier Risk Supplier risk management is how security teams identify, score, and monitor...

Frequently Asked Questions
IT Risk Management Software for Banks & Credit Unions FAQ
Find the answers you need here, or chat with us.
Contact Sales
Which regulatory frameworks does Isora support for banks and credit unions?

Isora GRC supports the frameworks financial institutions manage, including the GLBA Safeguards Rule, FFIEC guidance, NIST 800-53, NIST CSF, PCI-DSS, and state banking regulations such as NYDFS 23 NYCRR 500. In Isora, all frameworks share the same workspace, inventories, and risk register, so overlapping requirements reuse the same data.

How does Isora help with Safeguards Rule compliance?

Isora includes prebuilt GLBA questionnaires mapped to Safeguards Rule requirements. Teams can assess across departments and vendors, collect evidence inline, track findings through remediation, and produce the documented compliance evidence FTC examiners expect, all in one connected workspace.

Can Isora manage vendor due diligence for service providers?

Yes. Isora maintains a centralized vendor inventory with linked questionnaires, assessment results, risk ratings, and contract documentation. The documented oversight the GLBA Safeguards Rule requires is also built into the assessment workflow.

How long does Isora take to deploy at a financial institution?

Isora GRC deploys in weeks with no-code setup, minimal IT lift, and no outside consultants. Prebuilt GLBA questionnaires mean a first Safeguards Rule assessment goes out without months of configuration, which matters when the next examination is already on the calendar.

How does Isora compare to enterprise GRC tools for financial institutions?

Enterprise GRC platforms (Archer, ServiceNow GRC) require months of configuration and consultant-driven setup. Many financial institutions purchase these tools and keep preparing for examinations in spreadsheets. Isora deploys in weeks with prebuilt templates and an interface designed for the people who complete assessments as well as the people who manage them.

Can Isora support multi-framework compliance across banking regulations?

Yes. Financial institutions typically manage GLBA, FFIEC, NIST, PCI-DSS, and state requirements simultaneously. Isora supports all of these in the same workspace. The same vendor inventory, risk register, and reporting infrastructure serves every framework, so a new regulatory requirement reuses the existing setup.