




Archer IRM Alternatives: Compare GRC Platforms for IT and Vendor Risk
Archer IRM is an enterprise GRC platform. Built to support enterprise-wide governance, it offers deep configurability across risk, compliance, and audit programs.
Archer IRM’s IT & Security Risk Management use case includes an asset catalog, risk register and owned findings. According to its public sector page, most enterprise deployments go live in 8–12 weeks.
Tools like Archer IRM are part of a category of all-in-one GRC platforms. When managing assessments, inventories, and risk management across teams, you may need something more focused.
Why Teams Look for Archer Alternatives
Teams look for an alternative to Archer IRM after running into one or more common limitations.
| Common Limitation | Why It’s a Problem | What to Look for Instead |
| Built for broad GRC use, with IT and security risk as one of many use cases | Archer states that your team maps its own workflow during scoping | Purpose-built for IT and vendor risk |
| Heavy reliance on configuration | Each Archer application is configured by the customer, which makes configuration effort part of the purchase | Structured, out-of-the-box workflows |
What to Look for in an Archer IRM Alternative
When evaluating an Archer IRM alternative, the factors an organization can consider depend on its use case. Still, here’s what an alternative should cover:
- Support for internal and vendor assessments
- Centralized asset and vendor inventories
- Built-in exception and risk tracking
- Fast deployment and lightweight admin overhead
- Collaboration features for both technical and business users
- Usability across teams—not just GRC specialists
Make sure to ask potential vendors about each of these capabilities, before you sign a contract.
Top Archer IRM Alternatives
Archer IRM vs. Isora GRC
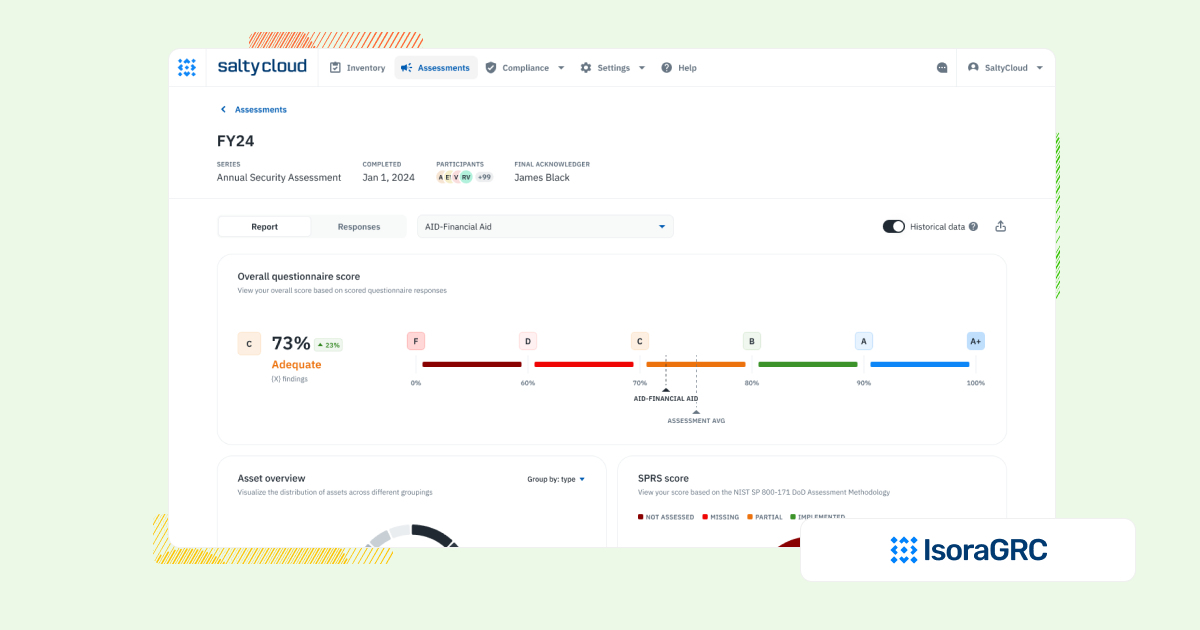
Isora GRC is the GRC Assessment Platform™ built specifically for information security teams. It supports the full risk workflow, from assessments and questionnaires to risks, inventory, and reporting.
Best for: Security teams that need to operationalize IT and third-party risk management across assets, third-party vendors, and business units.
| Isora GRC | |
| Strengths | Built for workflows, not checklists
✅ Supports assessments, inventory tracking, risk registers, and exceptions in a unified experience. Designed for org-wide adoption ✅ WCAG-compliant UX built for respondents outside security, which makes risk everyone’s job. Fast time-to-value ✅ Live in days or weeks, with no-code setup and minimal lift from IT. Flexible by default ✅ Customizable assessments and framework-aligned questionnaires without heavy configuration. Scales across teams and vendors ✅ Assesses internal teams and third-party vendors from one place. |
| Limitations | ⚠️ Not designed for legal, audit, or finance teams seeking one platform for enterprise-wide GRC
⚠️ May be too structured for teams looking to build one-off surveys or lightweight audits without repeatable workflows |
Archer IRM vs. ServiceNow GRC
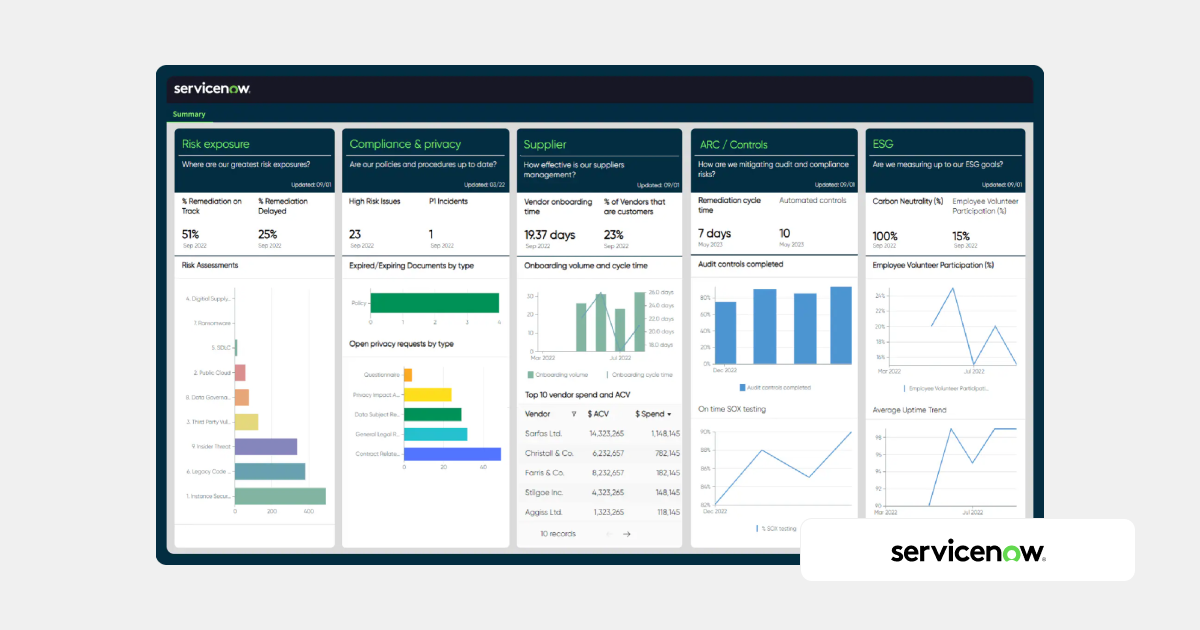
ServiceNow GRC extends the ServiceNow platform to include risk, compliance, and audit functions. It’s a logical next step for teams already invested in the ServiceNow ecosystem.
Best for: Organizations already using ServiceNow for IT operations that want to expand into risk and compliance management.
| ServiceNow GRC | |
| Strengths | ✅ Integrates smoothly with ServiceNow ITSM and other business processes
✅ Supports structured workflows for policy, compliance, and risk events |
| Limitations | ⚠️ IRM’s depth across inventory, risk and compliance assumes a populated configuration management database (CMDB) |
| Other Comparisons | Archer IRM vs ServiceNow GRC vs Isora GRC
OneTrust vs ServiceNow GRC vs Isora GRC |
Archer IRM vs. MetricStream
MetricStream is a comprehensive enterprise GRC platform used across industries to manage governance, risk, and compliance at scale. Consider MetricStream if you need a broad, enterprise-wide GRC platform. Its IT & Cyber Risk Management product lists IT risk assessments, an asset and threat repository and closed-loop issue remediation.
Best for: Large organizations with multiple departments that need a centralized GRC system for broad regulatory and risk oversight.
| MetricStream | |
| Strengths | ✅ Supports large-scale compliance efforts and regulatory frameworks like NIST 800-53
✅ Centralizes audit, risk, and policy management across business units ✅ Lists IT risk assessments, an asset and threat repository and closed-loop remediation, and MetricStream says its Survey Management software manages surveys across business units and locations, as of September 2026 |
| Limitations | ⚠️ A MetricStream press release says one insurer implemented policy management in 6 weeks and two more products in 6–8 weeks each. |
| Other Comparisons | MetricStream vs SAP GRC vs Isora GRC |
Archer IRM vs. SAP GRC
SAP GRC is designed to help businesses manage risk, controls, and compliance across SAP’s business software. It is tightly integrated with SAP, and SAP describes it as a modular suite organized around enterprise risk and compliance, identity and access governance, cybersecurity and data protection, and international trade management, available on premises, in the cloud or hybrid.
Best for: Organizations already deeply invested in SAP systems that want to manage risk and compliance directly within that ecosystem.
| SAP GRC | |
| Strengths | ✅ Strong integration with SAP’s financial, operational, and audit systems
✅ Useful for enforcing policies and controls across enterprise applications ✅ SAP describes a dashboard-driven interface for cloud access governance and AI assistants for GRC tasks |
| Limitations | ⚠️ Supported security frameworks are not named on SAP’s GRC product page, as of October 2026 |
| Other Comparisons | MetricStream vs SAP GRC vs Isora GRC |
Archer IRM vs. LogicGate
LogicGate is a flexible GRC platform that allows teams to create tailored workflows for risk, compliance, and vendor oversight. Its site lists purpose-built Applications for cyber risk, third-party risk, asset management and exceptions management.
Best for: Security or compliance teams that want to build custom risk workflows and have the resources to manage them over time.
| LogicGate | |
| Strengths | ✅ Highly customizable platform for building risk and compliance workflows
✅ Supports common frameworks like NIST and ISO through built-in controls ✅ No-code configuration ✅ Lists Reporting & Analytics as a platform feature |
| Limitations | |
| Other Comparisons | LogicGate vs Archer IRM vs Isora GRC |
Archer IRM vs. OneTrust GRC
OneTrust GRC provides a broad set of tools for privacy, compliance, and third-party risk management. Its Tech Risk and Compliance solution lists IT Risk Management, an asset inventory and issue workflows from intake through remediation.
Best for: Teams focused on privacy, third-party risk, and regulatory compliance rather than full internal IT risk programs.
| Category | Details |
| Strengths | ✅ Strong coverage of privacy regulations and vendor compliance requirements
✅ Includes out-of-the-box templates for third-party risk assessments ✅ Lists IT Risk Management, an evergreen asset inventory and exception tracking under its Tech Risk and Compliance solution ✅ OneTrust describes configurable assessment logic and automated issue workflows. Its Tech Risk and Compliance page lists UI-driven configuration without the need for IT resources, as of September 2026 |
| Limitations | ⚠️ OneTrust’s pricing page says each solution package has one or more usage meters, as of October 2026 |
| Other Comparisons | OneTrust vs ServiceNow GRC vs Isora GRC |
Archer IRM vs. Optro
Optro (formerly AuditBoard) is designed for audit professionals and control owners, offering tools to manage evidence collection, track compliance, and link controls to risks. It also lists IT & Cyber Risk Management and Third-Party Risk Management products with asset-level and automated vendor assessments. Optro says its risk and control self-assessment lets first-line stakeholders assess the risks most relevant to their business units.
Best for: Audit and compliance teams that need a streamlined platform to manage controls, documentation, and internal audits.
| Optro | |
| Strengths | ✅ Great for audit tracking, control documentation, and evidence management
✅ Supports collaboration between audit and compliance teams ✅ Lists IT & Cyber Risk Management with asset-level assessments and Third-Party Risk Management with automated vendor assessments, and describes risk and control self-assessments for business units ✅ Optro describes a configurable assessment process with out-of-the-box templates, and its FAQ calls the platform highly configurable, as of September 2026 |
| Limitations | ⚠️ Optro’s pricing page asks buyers to request pricing and lists no price, as of October 2026
⚠️ HECVAT is not named on the Optro product pages checked, as of October 2026 |
| Other Comparisons | AuditBoard vs ServiceNow GRC vs Isora GRC |
Archer IRM vs. ZenGRC
ZenGRC helps teams get organized for audits and compliance, with prebuilt templates for frameworks like SOC 2 and ISO. It lists Risk Management and Vendor Management modules with third-party risk assessments, questionnaires and continuous monitoring through a vendor portal.
Best for: Teams looking for a lightweight platform to manage audits, policies, and basic compliance tasks.
| ZenGRC | |
| Strengths | ✅ Interface for audit and policy tracking that ZenGRC describes as intuitive
✅ Prebuilt templates for common compliance frameworks ✅ Lists Risk Management, Vendor Management, Compliance and Audit Management modules, with vendor risk assessments, questionnaires and continuous vendor monitoring ✅ ZenGRC announced pre-loaded risk registers, its API documentation lists an Exceptions object, and its frameworks page lists an inventory of all systems, as of September 2026 |
| Limitations | ⚠️ ZenGRC does not publish a fixed public price list, according to its pricing post, as of October 2026 |
| Other Comparisons | ZenGRC vs AuditBoard vs Isora GRC |
Archer IRM vs. Onspring
Onspring is a highly configurable GRC platform that allows users to build tailored workflows without coding. It is a strong fit for audit or legal teams that need control over process design, and it lists Risk Management and Third-Party Risk Management products with a centralized risk register, automated assessment workflows and a third-party lifecycle from inventory and tiering through questionnaires to offboarding.
Best for: Teams that want a no-code platform to build customized audit, risk, and compliance processes across departments.
| Onspring | |
| Strengths | ✅ No-code customization allows for flexible risk, audit, and compliance workflows
✅ Works well for departments like legal, internal audit, and compliance that need structured processes |
| Limitations | ⚠️ Onspring states customers can implement on their own after administrator training, and that most choose to have Onspring implement for them because that service is included with some licensing models, as of October 2026
⚠️ May be overkill for security teams that want focused IT risk and vendor assessment tools |
| Other Comparisons | Onspring vs AuditBoard vs Isora GRC |
What Customers Say About Isora GRC
Security teams use Isora GRC to replace manual processes with intuitive workflows and actionable insight.
SaltyCloud makes Isora GRC, one of the products compared here. The assessments are our own, so confirm current features and pricing with each vendor before you decide.
FAQs
What are some alternatives to Archer IRM?
Archer IRM is part of a category of all-in-one GRC platforms—broad tools built for enterprise governance. Alternatives like Isora GRC provide structured, purpose-built workflows for managing IT and third-party risk without the complexity of heavy configuration.
Why do teams switch from Archer IRM to platforms like Isora GRC?
Teams move to Isora GRC when they need to manage risk assessments, inventories, and exceptions in a faster, more collaborative way.
Does Isora GRC replace tools like Archer IRM or complement them?
Isora GRC fits teams that need to run recurring internal security assessment programs across their own departments and systems. Archer is designed for broad enterprise governance, while Isora focuses on the specific workflows security teams use every day. That focus makes it easier to operationalize risk management without layering on another tool.
Which platform is better for managing IT risk assessments and exceptions?
Archer IRM supports assessments, and its IT risk use case links risks to assets and controls with owned, dated findings. Its third-party program sends questionnaires to vendors by secure link. Isora GRC offers built-in workflows for issuing assessments, collecting responses, tracking exceptions, and maintaining a risk register. All of this sits in a platform designed for adoption across the organization.
What should I look for in an Archer IRM alternative?
Look for a platform that supports structured risk workflows out of the box, including internal and vendor assessments, exception tracking, and inventory management. You’ll also want fast deployment, usability across teams, and minimal administrative overhead. Isora GRC was built with these exact needs in mind.
For a framework to evaluate GRC platforms before a demo, download our GRC Buyer’s Guide for Information Security Teams.


This content is for informational purposes only and does not constitute legal or compliance advice. See our full disclaimer.
 Other Relevant Content
