




Vanta Alternatives: Compare GRC Platforms for IT and Vendor Risk
Vanta is a compliance automation platform known for helping startups and scale-ups get through SOC 2 and ISO 27001 audits quickly. It automates evidence collection through integrations and agent-based tracking. Vanta also lists Risk Management and Third Party Risk Management products on its site.
For security teams looking to assess risk across departments and vendors, manage inventories, or track exceptions, Vanta’s Risk Management product lists a risk register with risk owners, treatment plans and continuous risk monitoring, and its Third Party Risk Management product lists a centralized vendor inventory and vendor security reviews. Vanta’s ISO 27001 page lists routing exceptions for approval. Questionnaire-based assessments of your own departments and units are not stated in its help center as of September 2026. Those are the parts of an IT risk management program to check before choosing it.
Vanta is part of the security compliance automation category—tools whose lead products are compliance frameworks such as SOC 2 and ISO 27001. Vanta also lists Risk Management and Third Party Risk Management products.
Why Teams Look for Vanta Alternatives
Teams look for an alternative to Vanta after running into one or more common limitations.
| Common Limitation | Why It’s a Problem | What to Look for Instead |
| Audit-first design | Vanta’s help center lists risk registers by business unit as an Advanced Risk Management feature, available as an upgrade or add-on | Purpose-built for security risk management |
| Unit-level questionnaires not stated | Questionnaire-based assessments of decentralized units are not stated on Vanta’s published surfaces as of September 2026 | Flexible assessments across internal and external teams |
| Frameworks outside its list | Vanta’s published framework list leaves out HECVAT, GLBA, TX-RAMP and StateRAMP/GovRAMP, as of October 2026 | Prebuilt HECVAT questionnaires and content for the frameworks your sector reports against |
What to Look for in a Vanta Alternative
When evaluating a Vanta alternative, the factors an organization can consider depend on its use case. Still, here’s what an alternative should cover:
- Structured assessment workflows for internal teams and vendors
- Risk tracking and exception tracking that goes beyond audit prep
- Tools that support collaborative, ongoing risk management
- Fast deployment without being locked into a rigid ecosystem
- A platform designed to grow with your security and compliance maturity
Make sure to ask potential vendors about each of these capabilities, before you sign a contract.
Top Vanta Alternatives
Vanta vs. Isora GRC
Isora GRC is the GRC Assessment Platform™ built specifically for information security teams. It supports the full risk workflow, from assessments and questionnaires to risks, inventory, and reporting.
Best for: Security teams that need to operationalize IT and third-party risk management across assets, third-party vendors, and business units.
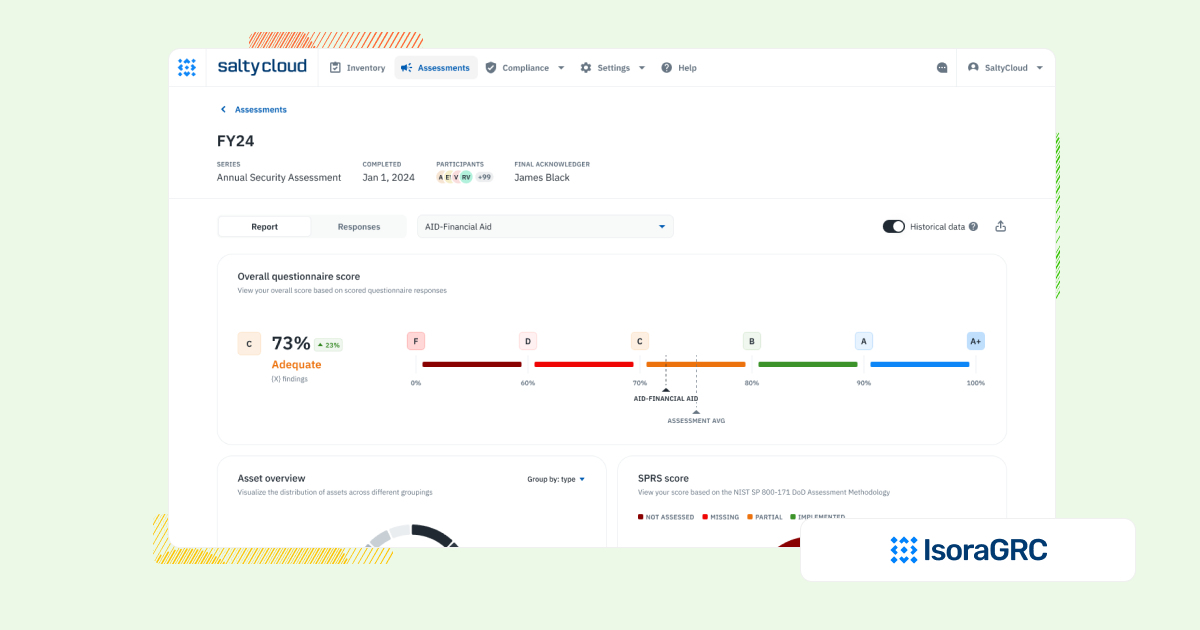
| Isora GRC | |
| Strengths | Built for workflows, not checklists
✅ Supports assessments, inventory tracking, risk registers, and exceptions in a unified experience. Designed for org-wide adoption ✅ WCAG-compliant UX built for respondents outside security, which makes risk everyone’s job. Fast time-to-value ✅ Live in days or weeks, with no-code setup and minimal lift from IT. Flexible by default ✅ Customizable assessments and framework-aligned questionnaires without heavy configuration. Scales across teams and vendors ✅ Assesses internal teams and third-party vendors from one place. |
| Limitations | ⚠️ Not designed for legal, audit, or finance teams seeking one platform for enterprise-wide GRC
⚠️ May be too structured for teams looking to build one-off surveys or lightweight audits without repeatable workflows |
Vanta vs. Drata
Drata is a compliance automation tool focused on fast audit prep. It automates evidence collection, and its product pages describe a centralized risk register, vendor inventory and recurring vendor reassessments, as of September 2026.
Best for: Startups and growing companies automating SOC 2, ISO 27001, and other compliance frameworks quickly.
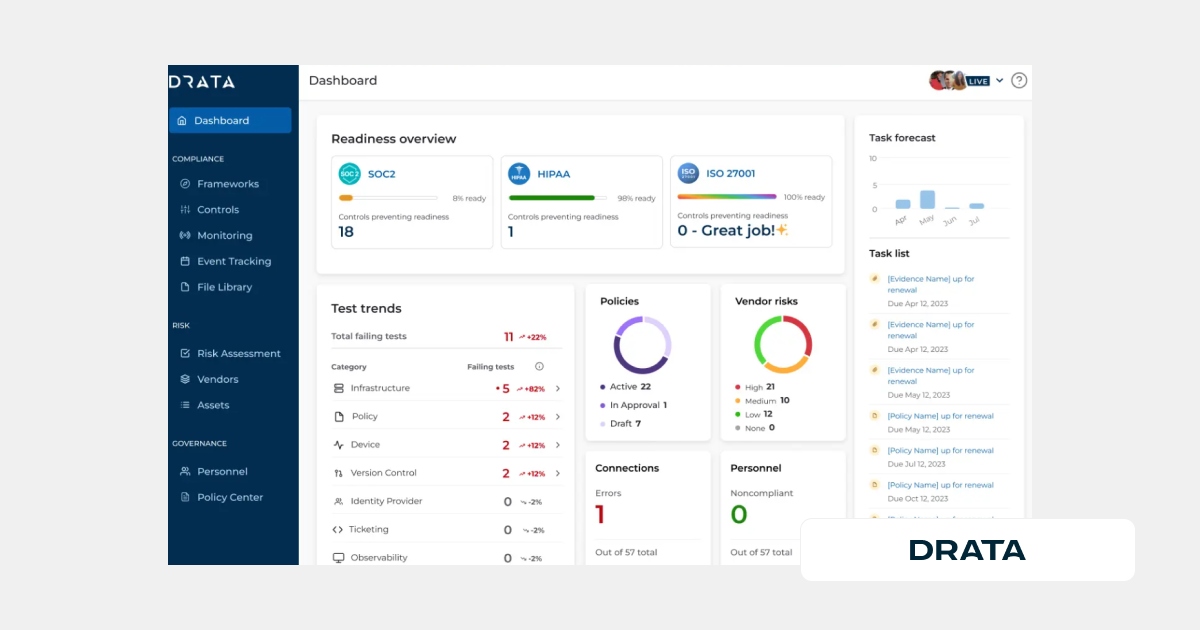
| Drata | |
| Strengths | ✅ Fast-track to audit readiness with automated control monitoring
✅ Integrates with popular cloud tools and frameworks |
| Limitations | ⚠️ No dedicated exception register is named on Drata’s product pages or help center as of September 2026 |
| Other Comparisons | Drata vs OneTrust vs Isora GRC |
Vanta vs. Hyperproof
Hyperproof focuses on control management and compliance task tracking. It helps maintain audit readiness, and its Risk Management product lists risk assessments, a risk register and vendor management with questionnaires and remediation action plans. Hyperproof’s Policy Management product also lists policy exception tracking, including who requested and who accepted each exception.
Best for: Compliance teams managing multiple frameworks and tracking evidence across controls.
| Hyperproof | |
| Strengths | ✅ Tracks controls across multiple compliance frameworks
✅ Automates evidence collection and status monitoring ✅ Lists risk assessments, a risk register, vendor remediation plans and policy exception tracking, as of September 2026 ✅ Lists a central vendor list with documents and renewal dates |
| Limitations | ⚠️ IT asset assessments are not stated on Hyperproof’s published surfaces as of September 2026 |
| Other Comparisons | Hyperproof vs Drata vs Isora GRC |
Vanta vs. Optro
Optro (formerly AuditBoard) describes itself as AI-powered GRC software with audit, compliance, IT risk and risk solutions. It is strong at managing evidence and compliance reports, and it also lists IT & Cyber Risk Management, Risk Management and Third-Party Risk Management products, with asset-level assessments and documented risk acceptance with sign-off. Optro says its WorkStream feature collects risk information from the business through a survey-based workflow.
Best for: Internal audit and SOX teams managing control documentation and audit trails.
| Optro | |
| Strengths | ✅ Great for internal audit processes and control testing
✅ User-friendly for auditors and compliance officers ✅ Lists IT & Cyber Risk Management and Third-Party Risk Management products, and describes risk and control self-assessments for business units ✅ Lists asset-level assessments and risk acceptance with sign-off. Optro’s product pages address risk owners, and its blog describes owner assignment and escalation |
| Limitations | ⚠️ Optro’s pricing page asks buyers to request pricing and lists no price, as of October 2026
⚠️ HECVAT is not named on the Optro product pages checked, as of October 2026 |
| Other Comparisons | AuditBoard vs ServiceNow GRC vs Isora GRC |
Vanta vs. OneTrust GRC
OneTrust GRC is strong in privacy compliance and vendor documentation. It also lists IT Risk Management, an asset inventory, issue workflows from intake through remediation and third-party risk treatment, with owners assigned across internal and external teams. OneTrust’s privacy operations checklist says to send simple questionnaires to teams and gather details from business owners, as of September 2026.
Best for: Legal, privacy, and vendor compliance teams managing documentation and regulatory frameworks.
| OneTrust GRC | |
| Strengths | ✅ Includes out-of-the-box templates for third-party risk assessments
✅ Strong privacy and regulatory compliance features ✅ Lists IT risk assessments and policy exception tracking, and OneTrust’s privacy operations checklist says to send simple questionnaires to teams, as of September 2026 |
| Limitations | ⚠️ Aimed at privacy and third-party programs
⚠️ OneTrust’s pricing page says each solution package has one or more usage meters, as of October 2026 |
| Other Comparisons | OneTrust vs ServiceNow GRC vs Isora GRC |
Vanta vs. LogicGate
LogicGate is a customizable GRC platform that lets users build their own processes for risk, compliance, and audit. It offers more flexibility than Vanta, and its Applications catalog lists prebuilt third-party risk, cyber risk and exception management applications as of September 2026.
Best for: Teams that want to design and control their own GRC workflows using a flexible, no-code builder.
| LogicGate | |
| Strengths | ✅ Highly flexible platform with visual workflow builder
✅ Supports frameworks like NIST, ISO, and SOC 2 with customizable mapping ✅ Lists prebuilt Applications for third-party risk, asset management, cyber risk and exceptions, and LogicGate’s Cyber Risk Management page lists customizable risk registers |
| Limitations | ⚠️ LogicGate’s services description lists typical implementation timelines of 30 to 150 days |
| Other Comparisons | LogicGate vs Archer IRM vs Isora GRC |
Vanta vs. ZenGRC
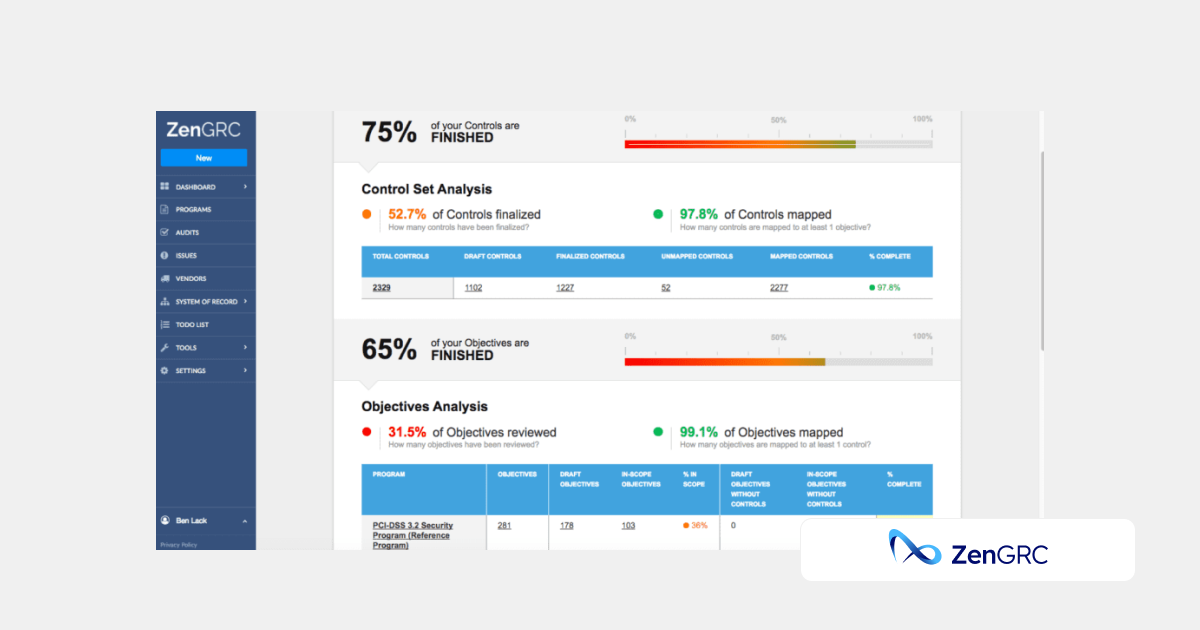
ZenGRC helps teams get organized for audits and compliance, and it lists Risk Management and Vendor Management modules with third-party risk assessments, questionnaires and continuous monitoring through a vendor portal. ZenGRC describes its interface as intuitive. ZenGRC’s API documentation also lists questionnaire schedules, with an IT department as its example recipient, as of September 2026.
Best for: Small teams or early-stage companies managing audit tasks and basic compliance frameworks.
| ZenGRC | |
| Strengths | ✅ Quick setup and simple UI for compliance tracking
✅ Framework templates for SOC 2, ISO, and others ✅ Lists risk assessments, and ZenGRC’s API documentation lists Data Assets, Systems and Exceptions objects, as of September 2026 ✅ Lists vendor management with a vendor portal, and ZenGRC’s API lists questionnaire schedules that can target a System record, as of September 2026 |
| Limitations | ⚠️ ZenGRC does not publish a fixed public price list. Its pricing post says each quote is a custom single flat rate with no separate fees for users, frameworks, or vendors, as of October 2026 |
| Other Comparisons | ZenGRC vs AuditBoard vs Isora GRC |
Vanta vs. Onspring
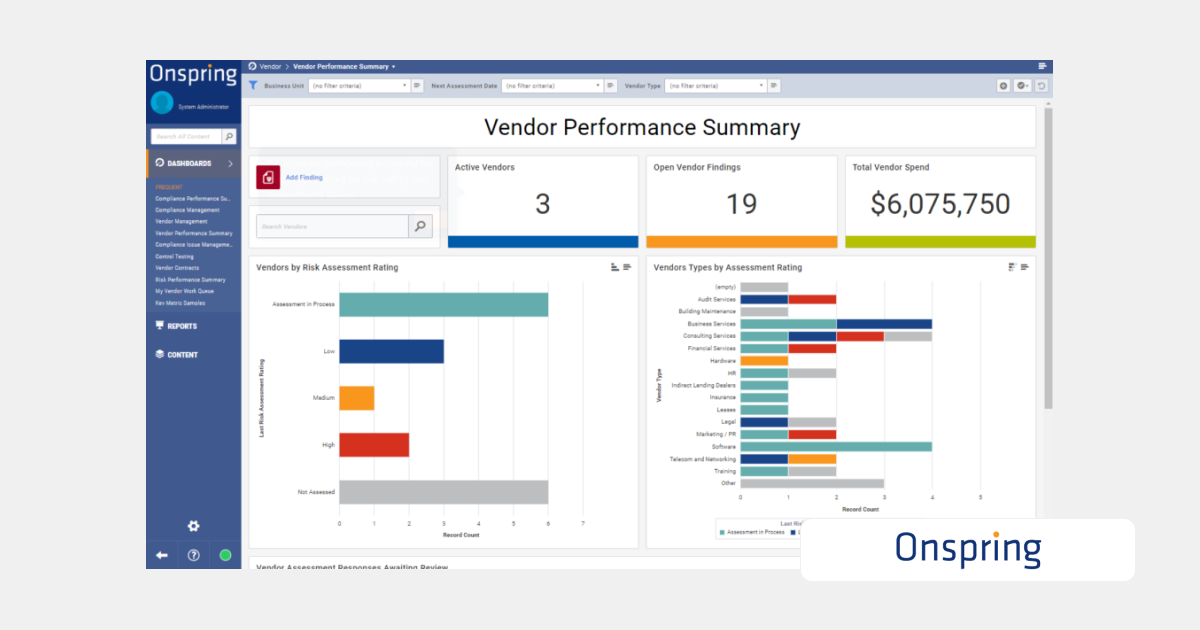
Onspring lets organizations design their own governance workflows from scratch. It is more flexible than Vanta, and it lists Risk Management and Third-Party Risk Management products with a risk register and exception management. Onspring states that it does not include prebuilt risk register content for your industry.
Best for: Legal, audit, or compliance teams looking for a no-code platform to build custom GRC processes.
| Onspring | |
| Strengths | ✅ Fully customizable, visual process builder
✅ Suitable for legal and compliance-led GRC initiatives ✅ Lists risk assessments, exception and risk acceptance management and third-party risk tracking |
| Limitations | ⚠️ Self-implementation requires a trained administrator; Onspring states most customers have Onspring implement for them
⚠️ Onspring’s FAQ says it does not include risk register content for your industry, as of October 2026 |
| Other Comparisons | Onspring vs AuditBoard vs Isora GRC |
Vanta vs. Archer IRM
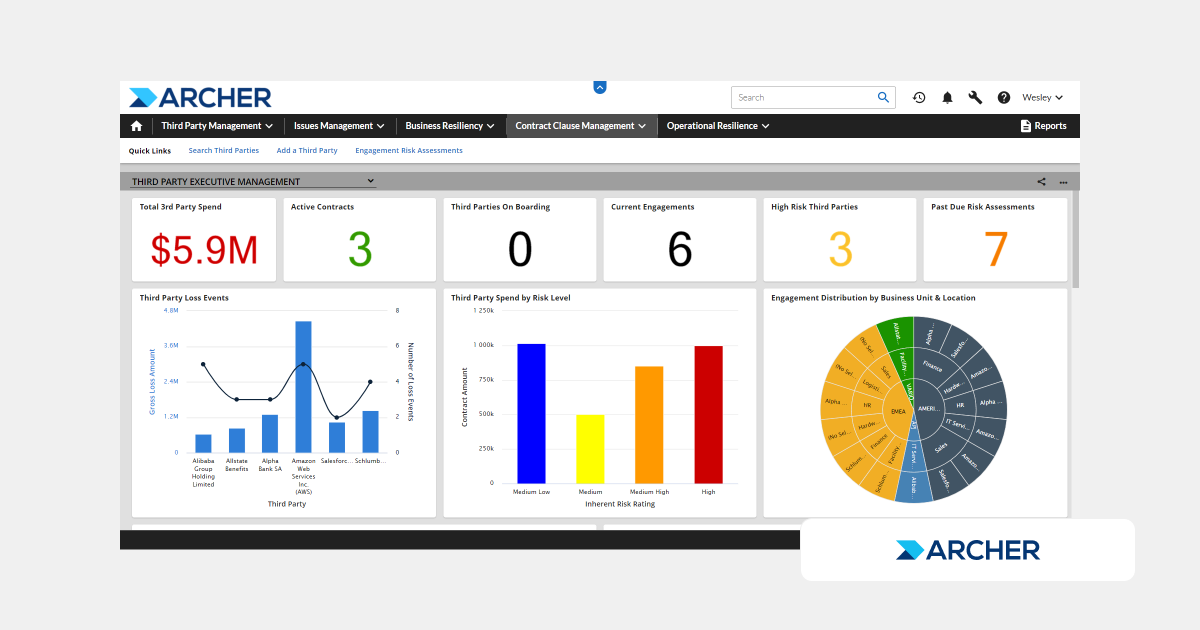
Archer IRM is a long-established GRC platform with broad features and high configurability, offered on-premises or as SaaS. The tool offers strong capabilities, and its IT & Security Risk Management use case ships with an IT asset catalog, a risk register and framework content including the ISO 27000 and NIST 800 series. Archer says it configures to the process you run today, and that your team maps its own workflow during scoping, and its public sector page says most enterprise deployments go live in 8–12 weeks.
Best for: Large enterprises with formalized GRC programs and dedicated governance teams.
| Archer IRM | |
| Strengths | ✅ Deep compliance functionality with support for complex governance programs
✅ Highly configurable across audit, risk, and compliance domains ✅ Lists IT & Security Risk Management and Third-Party Governance solution areas |
| Limitations | ⚠️ Archer’s public sector page says most enterprise deployments go live in 8–12 weeks, as of September 2026
⚠️ Archer says pricing scales with modules, users, and deployment model, as of October 2026 |
| Other Comparisons | Archer IRM vs ServiceNow GRC vs Isora GRC
LogicGate vs Archer IRM vs Isora GRC ZenGRC vs Archer IRM vs Isora GRC |
What Customers Say About Isora GRC
Security teams use Isora GRC to replace manual processes with intuitive workflows and actionable insight.
SaltyCloud makes Isora GRC, one of the products compared here. The assessments are our own, so confirm current features and pricing with each vendor before you decide.
FAQs
What are some alternatives to Vanta?
Vanta is a security compliance automation platform focused on helping companies achieve compliance with frameworks like SOC 2 and ISO 27001. Alternatives like Isora GRC support broader IT and vendor risk management—enabling teams to run internal and external assessments, track exceptions, and maintain risk registers beyond the audit cycle.
Why do teams switch from Vanta to platforms like Isora GRC?
Vanta is effective for audit readiness, and teams that need questionnaire-based assessments across their own units should confirm Vanta covers them. Vanta lists a risk register and a Third Party Risk Management product for vendors. Vanta’s help center describes risk registers organized by team or business unit, an Advanced Risk Management feature available as an upgrade or add-on, with risk assessments assigned to owners. Isora GRC offers purpose-built tools for operationalizing risk through assessments, inventories, and exception tracking.
Does Isora GRC replace tools like Vanta or complement them?
Isora GRC runs alongside Vanta rather than replacing it. Vanta proves the security team’s own posture to an auditor, and Isora GRC runs assessments across the departments and systems the security team does not operate, so the two cover different populations. Isora GRC does not name SOC 2, so a team that needs a SOC 2 report should keep a compliance automation platform such as Vanta.
Which platform is better for managing ongoing IT and vendor risk?
Vanta’s lead products are compliance frameworks, and it also lists a Risk Management product. Isora GRC is designed for managing risk over time—delivering repeatable assessment workflows, exception resolution, and vendor due diligence in a single platform that supports long-term security goals.
What should I look for in a Vanta alternative?
Look for a platform that enables continuous risk workflows, not just point-in-time compliance. Features like collaborative assessments, asset and vendor inventories, exception management, and risk visualization are essential. Isora GRC checks all those boxes—and scales as your program grows.
For a framework to evaluate GRC platforms before a demo, download our GRC Buyer’s Guide for Information Security Teams.


This content is for informational purposes only and does not constitute legal or compliance advice. See our full disclaimer.
 Other Relevant Content
