





OneTrust GRC Alternatives: Compare GRC Platforms for IT and Vendor Risk
OneTrust is best known for its privacy, compliance, and data governance tools. Its GRC platform extends into risk and third-party management, but it’s still largely rooted in regulatory workflows.
For security teams, that can mean working inside a platform built for many other functions first, including privacy, consent, AI governance and compliance. When your job is to assess risk, manage vendors, and track exceptions across your organization, a suite that broad can feel out of step.
OneTrust belongs to a category of privacy-centric GRC platforms: broad tools where information security risk is one workflow among privacy, AI governance, compliance and third-party management.
Why Teams Look for OneTrust GRC Alternatives
Teams look for an alternative to OneTrust GRC after running into one or more common limitations.
| Common Limitation | Why It’s a Problem | What to Look for Instead |
| Built as a broad suite spanning privacy, AI governance, compliance, tech risk and third-party management | Security risk is one workflow among many, and OneTrust’s pricing page says each solution package has one or more usage meters, as of October 2026 | Purpose-built for information security risk |
| Configuration across a multi-solution suite | Workflows and frameworks are configured within a platform that also runs privacy, consent and AI governance programs | Intuitive experience with fast deployment |
What to Look for in a OneTrust GRC Alternative
When evaluating an OneTrust GRC alternative, the factors an organization can consider depend on its use case. Still, here’s what an alternative should cover:
- Support for internal and vendor risk assessments
- Centralized IT asset and vendor inventories
- Exception management and risk registers that stay up to date
- Collaboration features to drive organization-wide adoption
- A platform designed for security teams—not just compliance officers
Make sure to ask potential vendors about each of these capabilities, before you sign a contract.
Top OneTrust GRC Alternatives
OneTrust GRC vs. Isora GRC
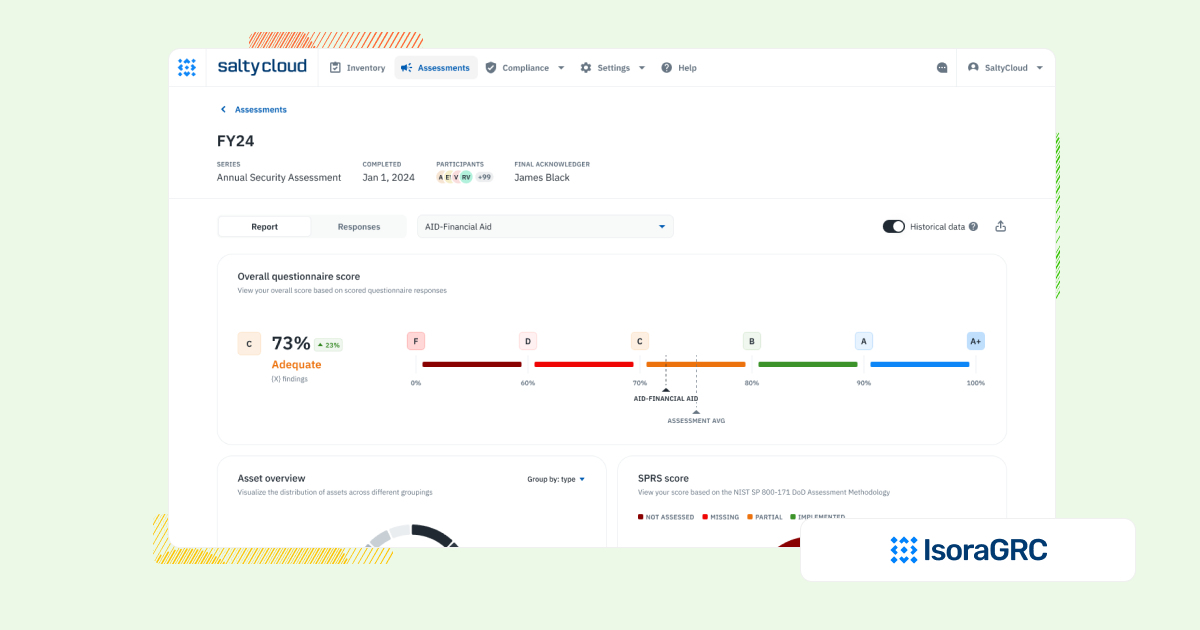
Isora GRC is the GRC Assessment Platform™ built specifically for information security teams. It supports the full risk workflow, from assessments and questionnaires to risks, inventory, and reporting.
Best for: Security teams that need to operationalize IT and third-party risk management across assets, third-party vendors, and business units.
| Isora GRC | |
| Strengths | Built for workflows, not checklists
✅ Supports assessments, inventory tracking, risk registers, and exceptions in a unified experience. Designed for org-wide adoption ✅ WCAG-compliant UX built for respondents outside security, which makes risk everyone’s job. Fast time-to-value ✅ Live in days or weeks, with no-code setup and minimal lift from IT. Flexible by default ✅ Customizable assessments, scalable categories, and framework-aligned questionnaires without heavy configuration. Scales across teams and vendors ✅ Assesses internal teams and third-party vendors from one place. |
| Limitations | ⚠️ Not designed for legal, audit, or finance teams seeking one platform for enterprise-wide GRC
⚠️ May be too structured for teams looking to build one-off surveys or lightweight audits without repeatable workflows |
OneTrust GRC vs. Archer IRM
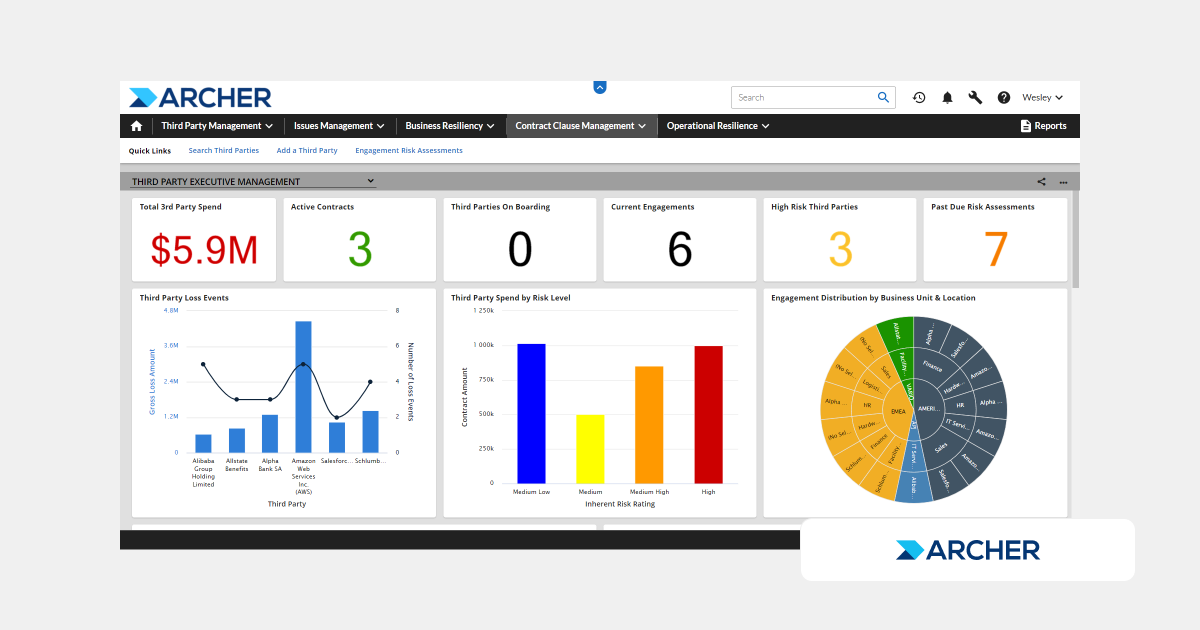
Archer IRM is an enterprise GRC platform designed for broad, cross-departmental risk and compliance management. It is highly customizable; its site says scope drives the implementation timeline and that most programs start with one IT and security risk use case.
Best for: Large organizations that need enterprise-wide governance across risk, compliance, audit and third-party programs.
| Archer IRM | |
| Strengths | ✅ Supports deep governance and compliance programs
✅ Highly configurable for large, centralized risk programs |
| Limitations | ⚠️ Implementation is scoped and phased; Archer’s site says scope drives the timeline and most programs start with one use case |
| Other Comparisons | Archer IRM vs ServiceNow GRC vs Isora GRC
LogicGate vs Archer IRM vs Isora GRC ZenGRC vs Archer IRM vs Isora GRC |
OneTrust GRC vs. ServiceNow GRC
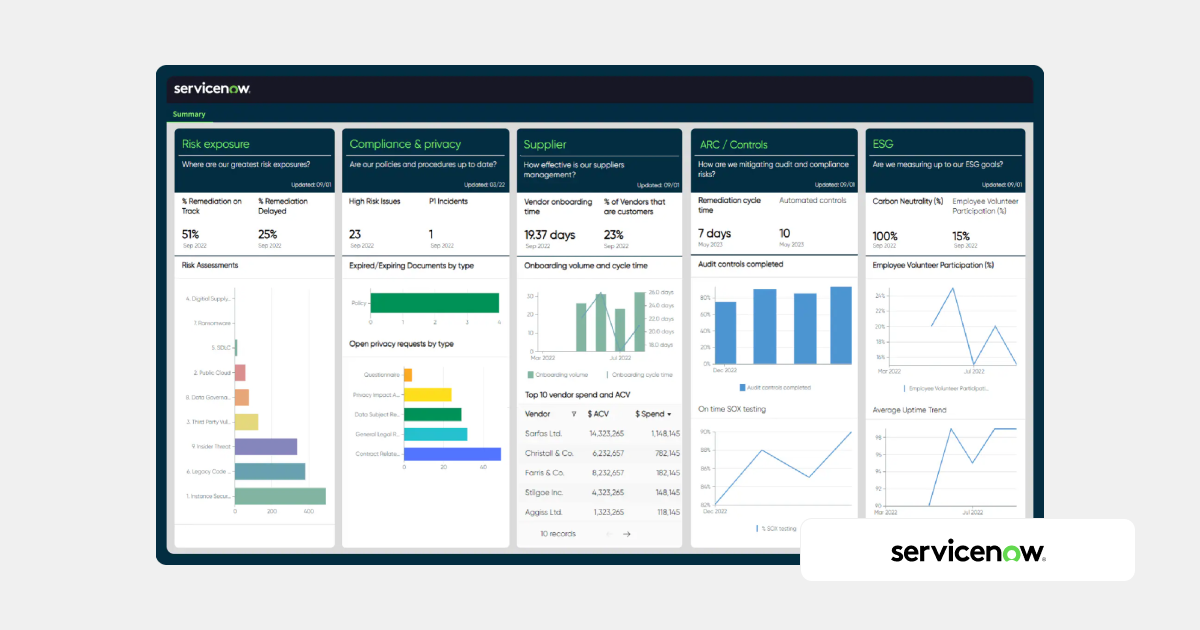
ServiceNow GRC adds risk and compliance tools on top of the core ServiceNow platform. Its risk and compliance records share one data model with the customer’s IT service, asset, and security data.
Best for: Organizations already using ServiceNow for IT operations that want to integrate risk and compliance into existing workflows.
| ServiceNow GRC | |
| Strengths | ✅ Tightly integrated with ServiceNow’s ITSM and business service workflows
✅ Supports structured compliance tracking and reporting |
| Limitations | ⚠️ That shared data model assumes a populated configuration management database (CMDB) |
| Other Comparisons | Archer IRM vs ServiceNow GRC vs Isora GRC
OneTrust vs ServiceNow GRC vs Isora GRC |
OneTrust GRC vs. SAP GRC
SAP GRC is tightly integrated with SAP’s financial and operational systems, offering governance and compliance tools tailored to that ecosystem.
Best for: Enterprises heavily invested in SAP products that need compliance and controls embedded in business systems.
| SAP GRC | |
| Strengths | ✅ Strong for enforcing policies and controls across SAP environments
✅ Designed to meet regulatory and audit standards in large organizations |
| Limitations | ⚠️ SAP says its GRC solutions are “integrated with SAP S/4HANA and available with additional licensing,” as of October 2026 |
| Other Comparisons | MetricStream vs SAP GRC vs Isora GRC |
OneTrust GRC vs. LogicGate
LogicGate offers flexible, no-code workflow building for risk and compliance teams. Its site lists purpose-built applications, including cyber risk management, third-party risk management, asset management and exceptions management, each configured in a no-code builder.
Best for: Teams that want to build and control their own risk processes in a visual, no-code environment.
| LogicGate | |
| Strengths | ✅ Flexible visual builder for creating custom workflows and dashboards
✅ Supports use cases across risk, compliance, and third-party management |
| Limitations | ⚠️ Cyber risk, third-party risk, asset and exception workflows ship as separate applications on the Risk Cloud platform |
| Other Comparisons | LogicGate vs Archer IRM vs Isora GRC |
OneTrust GRC vs. Optro
Optro (formerly AuditBoard) makes it easy to document controls, collect evidence, and manage compliance tasks. Its site also lists a Cyber Risk Management product and a third-party risk management product with automated vendor assessments and remediation tasks. Optro’s IT risk and compliance page lists exceptions management for managing and remediating policy exceptions, as of September 2026.
Best for: Internal audit and compliance teams that need structured tools to manage controls, evidence, and audit readiness.
| Optro | |
| Strengths | ✅ Great for tracking controls and managing audit documentation
✅ Simple, guided workflows for compliance teams and auditors |
| Limitations | ⚠️ Vendor reviews and cyber risk management are separate products from the audit and controls modules
⚠️ A broad platform spanning audit, compliance, risk, infosec and AI governance, so a security team adopts more than its own workflows ⚠️ Optro’s pricing page asks buyers to request pricing and lists no price, as of October 2026 |
| Other Comparisons | AuditBoard vs ServiceNow GRC vs Isora GRC |
OneTrust GRC vs. ZenGRC
ZenGRC is a GRC platform designed to help teams stay on top of compliance obligations like SOC 2, ISO, or NIST. Its site also lists risk management with real-time monitoring and vendor management with questionnaires, continuous monitoring and a vendor portal.
Best for: Smaller teams looking to organize compliance documentation and track audit progress with minimal overhead.
| ZenGRC | |
| Strengths | ✅ Easy to use and fast to set up for basic compliance tracking
✅ Useful for organizing audit evidence and framework mappings ✅ ZenGRC’s frameworks page lists an inventory of all the systems that control data assets, as of September 2026 ✅ ZenGRC announced pre-loaded risk registers, and its API documentation lists an Exceptions object, as of September 2026 |
| Limitations | ⚠️ ZenGRC does not publish a fixed public price list. Its pricing post says each quote is a custom single flat rate with no separate fees for users, frameworks, or vendors, as of October 2026 |
| Other Comparisons | ZenGRC vs AuditBoard vs Isora GRC |
OneTrust GRC vs. MetricStream
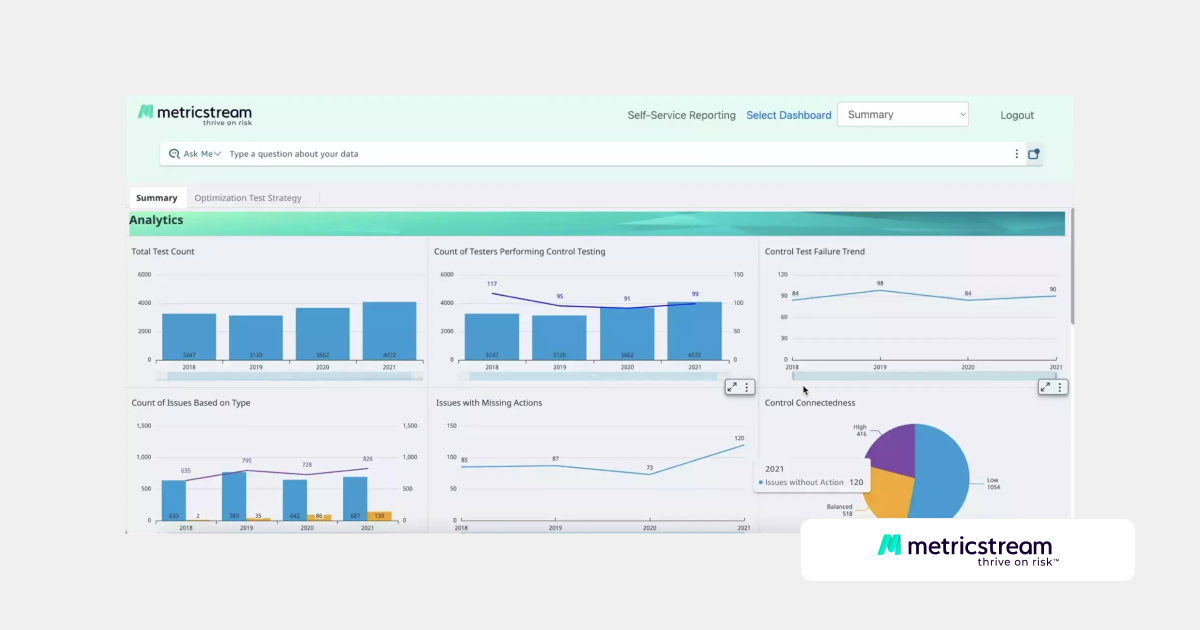
MetricStream is an enterprise GRC platform built to manage risk, audit, and compliance across large organizations. Its site lists IT and cyber risk assessments, vulnerability-based remediation for security teams and third-party assessments among its enterprise modules.
Best for: Large enterprises needing a centralized GRC system to manage complex, cross-departmental risk and compliance programs.
| MetricStream | |
| Strengths | ✅ Supports complex compliance programs and regulatory frameworks like NIST 800-53
✅ Centralized governance tools with deep reporting capabilities ✅ MetricStream says its Survey Management software manages surveys across business units and locations, as of September 2026 |
| Limitations | ⚠️ An enterprise platform where IT and cyber risk is one module among audit, compliance, enterprise risk and third-party programs
⚠️ IT and cyber risk and IT vendor risk run as separate MetricStream products, as of October 2026 |
| Other Comparisons | MetricStream vs SAP GRC vs Isora GRC |
OneTrust GRC vs. Onspring
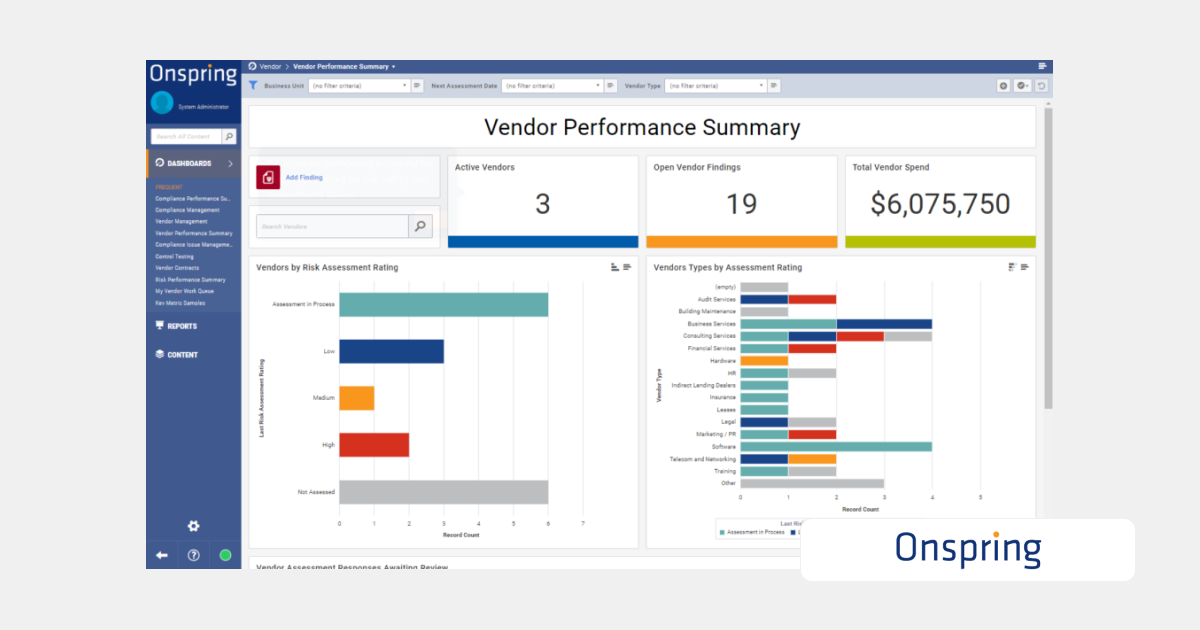
Onspring is a no-code GRC platform that allows users to design their own workflows for risk, compliance, and audits. Onspring’s site says most customers choose to have Onspring run the implementation.
Best for: Process-heavy departments like legal or audit that want to build custom GRC workflows without code.
| Onspring | |
| Strengths | ✅ No-code customization across audit, risk, and compliance use cases
✅ Good for teams with unique process needs and in-house ownership |
| Limitations | ⚠️ Onspring’s GRC Suite page says implementation is included “with some licensing models,” and a team that implements on its own needs a designated administrator to complete training, as of October 2026 |
| Other Comparisons | Onspring vs AuditBoard vs Isora GRC |
What Customers Say About Isora GRC
Security teams use Isora GRC to replace manual processes with intuitive workflows and actionable insight.
SaltyCloud makes Isora GRC, one of the products compared here. The assessments are our own, so confirm current features and pricing with each vendor before you decide.
FAQs
What are some alternatives to OneTrust GRC?
OneTrust GRC is a privacy-centric GRC platform, built privacy-first and extended into GRC, third-party risk, and AI governance. Isora GRC fits security teams that need structured tools for security risk management, including assessments, inventories, and exception tracking.
Why do teams switch from OneTrust GRC to platforms like Isora GRC?
OneTrust is built privacy-first and extended into GRC, third-party risk, and AI governance. Isora GRC provides a focused, easy-to-use platform that supports the work security teams actually do—without the overhead.
Does Isora GRC replace tools like OneTrust, or complement them?
Isora GRC provides workflows for assessments, exception tracking, vendor inventories, and risk registers. Whether it replaces OneTrust or runs alongside it depends on which of those workflows a team runs in OneTrust today.
Which platform is better for managing vendor and IT risk?
OneTrust is strong in privacy compliance and data governance, and its site also lists third-party risk assessments, IT risk management and issue remediation workflows. OneTrust’s IT Risk Management page also lists assessments that engage the business and collect information, as of September 2026. Isora GRC is purpose-built to handle these workflows—helping teams manage vendor and IT risk collaboratively and continuously.
What should I look for in a OneTrust GRC alternative?
Choose a platform that supports repeatable assessment workflows, centralized risk and exception tracking, and fast deployment. Look for usability beyond GRC teams—so you can engage stakeholders across your organization. Isora GRC checks all of these boxes.
For a framework to evaluate GRC platforms before a demo, download our GRC Buyer’s Guide for Information Security Teams.


This content is for informational purposes only and does not constitute legal or compliance advice. See our full disclaimer.
