




Every security team needs a hands-on, scalable way to manage IT risk—not just monitor outside scores.
Platforms like Bitsight and SecurityScorecard provide vendor intelligence, helping organizations spot potential risks through external ratings and benchmarks.
External scores can highlight issues, and Bitsight and SecurityScorecard both also list workflows to track and resolve them, so compare how far each one goes.
Isora GRC creates a simpler, more efficient process. It’s purpose-built for security teams who need to run real assessments, manage inventories, and track risks, without relying solely on surface-level insights.
Let’s take a more detailed glance.
Choosing the Right Platform for IT Risk Management
Bitsight and SecurityScorecard are both built around external risk scoring. They scan vendors for signals like exposed services or leaked credentials and assign a numerical score. That’s helpful for monitoring, and both vendors also list tools for managing risk. Bitsight lists vendor assessments, documentation requests and remediation tracking, and SecurityScorecard lists questionnaires, documentation requests and Action Plans with owners.
Isora GRC is built to help security teams manage vendor risk from end to end. That means issuing custom or framework-based questionnaires (like HECVAT or SIG), logging findings, assigning ownership, and maintaining a dynamic, auditable risk register. If you’re ready to run active risk management, Isora gives you the structure to make it repeatable.
The Workflow That Matters: Managing IT Risks and Compliance
Knowing that a vendor has a low score doesn’t mean you’ve managed the risk. That takes context, documentation, stakeholder input, and follow-up. Bitsight and SecurityScorecard tell you what’s exposed, and both also list vendor evidence review and remediation tracking.
Isora GRC supports that full workflow. From assessment to resolution, every step is structured, trackable, and repeatable. Whether you’re managing a dozen vendors or hundreds, Isora makes it easy to keep risk visible, decisions documented, and progress measurable.
How Each Platform Supports IT Risk Management Workflows
| Workflow Area | Bitsight | SecurityScorecard | Isora GRC |
| Assessment Management | Bitsight tracks security ratings and third-party risks. Its Vendor Risk Management product automates vendor assessments mapped to SIG Lite, NIST CSF 2.0, ISO 27001, HECVAT and more. Its Framework Intelligence also evaluates internal controls from uploaded documents. | SecurityScorecard focuses on rating and checking outside companies for security risks. It says the platform also assesses your own systems with the same rigor used for vendors. Its help center documents sending questionnaires to different teams in your organization. | Centralized, intuitive assessment dashboard across business units, vendors, and assets. Built specifically for security teams. |
| Questionnaire Delivery & Completion | Bitsight’s Vendor Risk Management product sends tiered questionnaire sets, including SIG, NIST CSF, ISO 27001 and CAIQ, with automatic reassessment reminders. It validates vendor responses against its ratings data. | SecurityScorecard runs automatic checks on third-party risks. Its pricing page lists templated questionnaire management, with custom questionnaires on the Premium and Elite plans. | Customizable and prebuilt questionnaires for frameworks like NIST, ISO, GLBA, HIPAA, and more. Designed for internal and external collaboration. |
| Inventory Tracking | Bitsight builds a third-party inventory and discovers internet-facing assets by scanning. Its Ratings Tree gives a hierarchical view of your subsidiaries and business units. An inventory of internal assets is not stated on Bitsight’s product pages or help center as of September 2026. | SecurityScorecard works mostly on security ratings for outside vendors. Its pricing page lists a vendor system of record, and free accounts include digital footprint management for your own domain. | Centralized tracking of assets, vendors, and organizational units with integration support for existing data sources. |
| Risk Register & Exception Management | Bitsight scores vendor risk with Impact, Trust and Risk Scores and tracks vendor remediation progress. Its issue tracking also lets a team mark its own findings Risk Accepted. A risk register is not stated on Bitsight’s product pages or help center as of September 2026. | SecurityScorecard gives insight into third-party risks, and its help center lists a Risk Register report widget for your organization. It also documents an Accept Risk action that formally accepts a vendor finding without requiring remediation. | Flexible, collaborative risk register with scoring, status, evidence, and ownership tied directly to assessments. Exception management is built-in and intuitive—no extra modules or configuration required. |
| Scoring, Reporting & Risk Visualization | Security ratings come with insights and board-level reporting. | SecurityScorecard does well with external security ratings and reports. Its help center also lists report widgets for your own organization, such as a NIST Cybersecurity Framework maturity score. | Automated scorecards, risk maps, and executive-friendly reports with actionable insights—no manual config required. |
| Collaboration & User Experience | The interface suits security pros. Bitsight’s help center documents private finding comments and @mentions of colleagues for internal discussion. | The design is clean and works well for security teams checking outside risks. Its Action Plans assign owners to issues and track progress in real time. Its TITAN Secure product adds an Exchange Hub to request remediation or documentation from third parties. | WCAG-compliant, award-nominated interface with built-in commenting, team workflows, and fast onboarding. |
| Implementation & Setup | Setup feels simple for security-focused teams. For GRC workflows Bitsight lists integrations with ServiceNow, Archer, OneTrust, ProcessUnity and Aravo. | Setup is simple for companies focused on vendor risks. Its pricing page lists basic and advanced integrations and APIs for custom integrations. Its help center documents Jira tickets for findings, with automated finding-level tickets in early access. | No-code setup in days or weeks. Minimal IT lift required. Designed to go live quickly across teams and vendors. |
What Sets Isora GRC Apart?
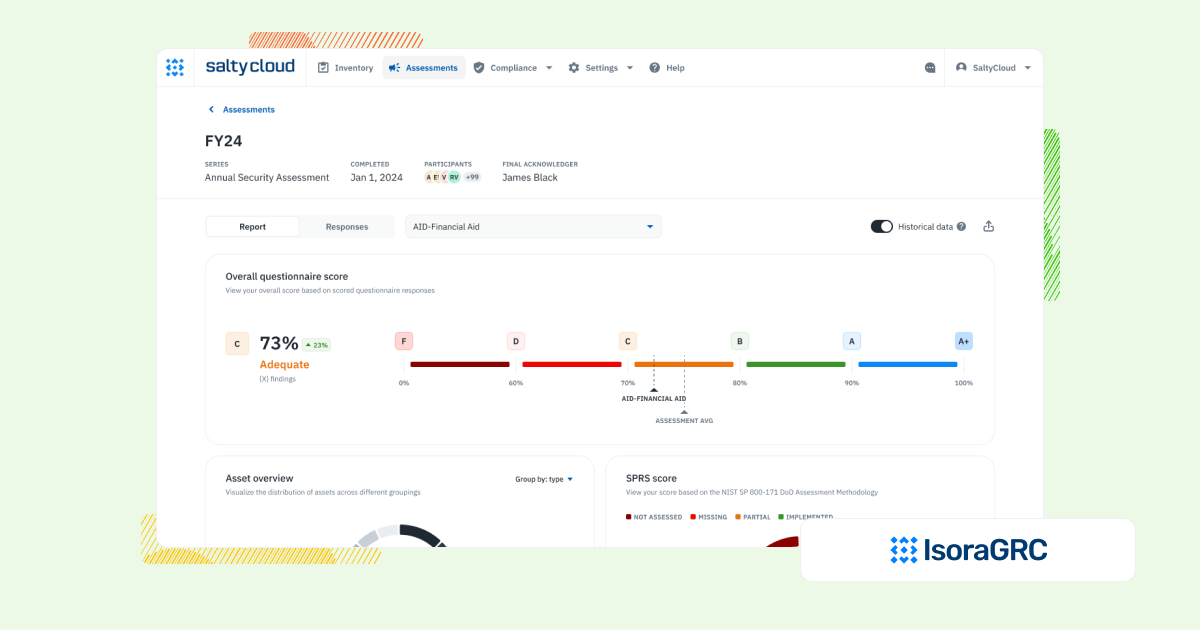
Isora GRC was purpose-built for information security teams—designed to support the real workflows behind risk and compliance, not just generate reports. While legacy GRC platforms require months of configuration and rigid processes, Isora takes a modern, scalable approach:
- Purpose-built for security and third-party risk teams
- No extra modules or cross-department bloat—just the workflows that matter.
- Easy for anyone to use
- Clean UI, no complex training, and built to drive adoption across the org.
- Streamlined for action, not just documentation
- Assessments, questionnaires, inventories, risk tracking, and reporting—all in one place.
- Fast, no-code implementation
- Go live in weeks, not quarters, with minimal IT lift.
- Scales with your program
- Whether you’re running a lean risk function or supporting a large institution, Isora grows with you—without getting in the way.
Who Each Platform Is Best For
| Platform | Who It’s For |
| Bitsight | Companies tracking security ratings for vendors, with vendor assessment workflows in Bitsight’s Vendor Risk Management product. |
| SecurityScorecard | Seeing how vendors stack up at a glance. Its site also lists templated questionnaires, Action Plans and self-monitoring of your own external posture. |
| Isora GRC | Security teams that need a scalable, usable IT risk management program across their organization. |
What Our Customers Say About Isora GRC
Security teams at top institutions are using Isora GRC to replace legacy tools and manual processes with intuitive workflows and actionable insight.
SaltyCloud makes Isora GRC, one of the products compared here. The assessments are our own, so confirm current features and pricing with each vendor before you decide.
FAQs
What’s the difference between Bitsight, SecurityScorecard, and Isora GRC?
Bitsight and SecurityScorecard provide external security ratings based on publicly observable data, and both also list vendor questionnaires and a vendor inventory. Isora GRC supports third-party risk management workflows, including sending security questionnaires, managing vendor inventories, tracking exceptions, and maintaining a centralized risk register.
Are Bitsight and SecurityScorecard considered vendor risk management platforms?
Both sell vendor risk products built on their ratings, and Bitsight says its Vendor Risk Management product manages the entire vendor lifecycle in one platform. Both list document collection, owner assignment and remediation tracking.
Does Isora GRC replace platforms like Bitsight or SecurityScorecard?
For many teams, yes. Isora GRC allows organizations to assess vendors directly, manage third-party data in one place, and drive follow-up.
Which platform is better for managing vendor risk across the organization?
Isora GRC is designed for full third-party risk workflows. It supports frameworks like HECVAT, SIG, and CAIQ, while also providing vendor inventory, assessment, and exception tracking capabilities. Bitsight and SecurityScorecard both name HECVAT in their vendor-assessment coverage, and both anchor on outside-in ratings. Both also describe assessing your own organization, through Bitsight’s Framework Intelligence and SecurityScorecard’s self-assessment.
Can Isora GRC be used alongside Bitsight or SecurityScorecard?
Yes. Some organizations use Bitsight or SecurityScorecard for initial vendor screening or continuous monitoring and use Isora GRC for assessment management and ongoing collaboration with vendors.
What should I look for in a platform to manage vendor risk effectively?
Look for tools that support vendor assessments, evidence collection, exception tracking, and collaboration—not just surface-level risk scores. Isora GRC delivers those workflows in a centralized platform security teams can own.
For a framework to evaluate GRC platforms before a demo, download our GRC Buyer’s Guide for Information Security Teams.


This content is for informational purposes only and does not constitute legal or compliance advice. See our full disclaimer.
