





IT Risk Management Software for Hospitals and Health Systems: Compare GRC Platforms
For hospitals and health systems that are HIPAA covered entities, the HIPAA Security Rule sets the core of the IT risk program. Under 45 CFR 164.308, a covered entity or business associate must “conduct an accurate and thorough assessment of the potential risks and vulnerabilities to the confidentiality, integrity, and availability of electronic protected health information” it holds. The next required specification calls for “security measures sufficient to reduce risks and vulnerabilities to a reasonable and appropriate level.”
The same section calls for “a periodic technical and nontechnical evaluation,” based first on the rule’s standards and later “in response to environmental or operational changes affecting the security of electronic protected health information.” It also lets a covered entity permit a business associate to handle that information only if it obtains “satisfactory assurances” that the business associate “will appropriately safeguard the information,” documented through a written contract or other arrangement.
Under 45 CFR 164.316, the required documentation is kept “for 6 years from the date of its creation or the date when it last was in effect, whichever is later,” and reviewed “periodically.”
That makes a documented risk analysis, a record of how each risk is reduced, recurring evaluations and assurances from business associates the core of the program. This guide compares IT risk management software for hospitals and health systems against that work.
What to Look For in an IT Risk Management Tool for Healthcare Organizations
When evaluating IT risk management software for hospitals and health systems, the factors an organization can consider depend on its use case. Still, here’s what a platform should cover:
- Structured security risk assessments across departments, systems, and business associates
- Questionnaire delivery and completion tracking for business units and third-party vendors
- An inventory of IT systems, clinical applications, medical devices, and vendors, each with a named owner
- A risk register and exception tracking that follow each finding to closure
- Dated records of each assessment and evaluation that the organization can keep for six years
- Reports that leadership and auditors can read
- An interface that clinical, IT, and administrative staff outside security can use
- A clear implementation timeline and the internal effort it requires
Make sure to ask potential vendors about each of these capabilities, before you sign a contract.
Top IT Risk Management Platforms for Hospitals and Health Systems
Isora GRC
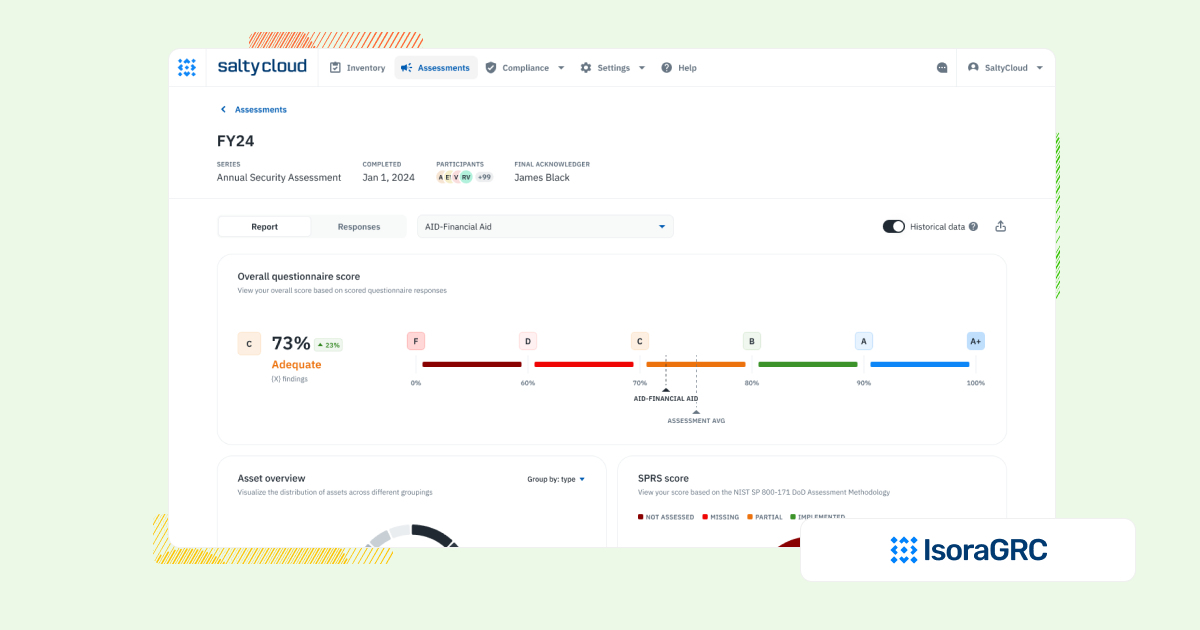
Isora GRC is the GRC Assessment Platform™ built specifically for information security teams. It supports the full risk workflow, from assessments and questionnaires to risks, inventory, and reporting. Isora names HIPAA on its HIPAA Security Rule compliance software page.
Best for: Security teams that need to operationalize IT and third-party risk management across assets, third-party vendors, and business units.
| Isora GRC | |
| Strengths | Built for workflows, not checklists
✅ Supports assessments, inventory tracking, risk registers, and exceptions in a unified experience. Designed for org-wide adoption ✅ WCAG-compliant UX built for respondents outside security, which makes risk everyone’s job. Fast time-to-value ✅ Live in days or weeks, with no-code setup and minimal lift from IT. Flexible by default ✅ Customizable assessments, scalable categories, and framework-aligned questionnaires without heavy configuration. Scales across teams and vendors ✅ Assesses internal teams and third-party vendors from one place. |
| Limitations | ⚠️ Not designed for legal, audit, or finance teams seeking one platform for enterprise-wide GRC
⚠️ May be too structured for teams looking to build one-off surveys or lightweight audits without repeatable workflows |
Archer IRM
Archer IRM is an enterprise GRC platform used to manage risk, audit, and compliance across large organizations. Its healthcare page says Archer “helps health systems unify HIPAA, privacy, and quality obligations so patient care never waits on paperwork,” and according to its public sector page, most enterprise deployments go live in 8–12 weeks.
Best for: Large health systems with centralized GRC teams and the budget to support deep customization.
| Archer IRM | |
| Strengths | ✅ Deep governance and compliance functionality
✅ Highly configurable for enterprise-wide programs ✅ Security and vendor risk use cases ship with prebuilt content ✅ Archer’s healthcare page describes tracking “every vendor’s certifications, audits, and BAAs in one portal,” as of October 2026 |
| Limitations | ⚠️ Archer says pricing scales with modules, users, and deployment model, as of October 2026 |
| Other Comparisons | Archer IRM vs ServiceNow GRC vs Isora GRC
LogicGate vs Archer IRM vs Isora GRC ZenGRC vs Archer IRM vs Isora GRC |
OneTrust
OneTrust extends the privacy platform with compliance and third-party risk tools. Its HIPAA compliance page says OneTrust helps “safeguard protected health information with comprehensive scoping, HIPAA toolkits, and easy tracking and reporting,” and its Tech Risk and Compliance solution lists IT Risk Management, an evergreen asset inventory and issue workflows from intake through remediation.
Best for: Organizations focused on privacy, data governance, and third-party risk. OneTrust also lists IT Risk Management.
| OneTrust | |
| Strengths | ✅ Good for vendor risk reviews and privacy-focused compliance programs
✅ Its HIPAA compliance page lists a library of pre-built policies and a scoping survey to help identify security risks, as of October 2026 ✅ Lists IT risk management, an evergreen asset inventory and policy exception tracking, and OneTrust’s Tech Risk and Compliance page says UI-driven configuration simplifies configuration updates without the need for IT resources, as of October 2026 |
| Limitations | ⚠️ OneTrust’s pricing page says each solution package has one or more usage meters, as of October 2026 |
| Other Comparisons | OneTrust vs ServiceNow GRC vs Isora GRC |
LogicManager
LogicManager describes itself as a holistic Enterprise Risk Management platform that connects day-to-day risk activity to strategic goals, business performance, and Board-level oversight. Its healthcare page says its pre-built risk library tracks requirements “including the Joint Commission, HIPAA, Medicare and Medicaid, the Affordable Care Act, and more,” and names Winona Health as a LogicManager customer. LogicManager pairs each customer with a dedicated advisory analyst from day one.
Best for: Hospitals and health systems that run risk management as an enterprise-wide program reporting to the board.
| LogicManager | |
| Strengths | ✅ Job-to-be-Done pricing with unlimited internal and external users
✅ Risk Ripple links vulnerabilities to assets, controls to policies, and incidents to downstream consequences ✅ Its HIPAA compliance page lists pre-built HIPAA risk assessment templates for Information Security, Data Privacy, and Incident Management |
| Limitations | ⚠️ LogicManager’s pricing page asks buyers to fill out a form and lists no prices, as of October 2026 |
| Other Comparisons | Quantivate vs LogicManager vs Isora GRC |
LogicGate
LogicGate is built for teams that want to design their own GRC workflows without code. Its Applications catalog lists 30+ purpose-built applications, and its healthcare page says Risk Cloud helps healthcare providers “protect patient data, ensure compliance with industry regulations like HIPAA and GDPR, and mitigate cybersecurity, operational, and third-party risks.”
Best for: Healthcare organizations that want a flexible, no-code way to build their own GRC workflows over time.
| LogicGate | |
| Strengths | ✅ Highly configurable and adaptable to different risk processes
✅ Its frameworks page lists HIPAA (Security Standards – Subpart 3) alongside NIST 800-53, NIST CSF and ISO 27001-2, as of October 2026 |
| Limitations | ⚠️ LogicGate’s services description lists typical implementation timelines of about 30 to 150 days, depending on the implementation package, as of October 2026 |
| Other Comparisons | LogicGate vs Archer IRM vs Isora GRC |
What Customers Say About Isora GRC
Security teams use Isora GRC to replace manual processes with intuitive workflows and actionable insight.
SaltyCloud makes Isora GRC, one of the products compared here. The assessments are our own, so confirm current features and pricing with each vendor before you decide.
FAQs
What’s the best IT risk management software for HIPAA compliance in hospitals?
The right platform depends on the program’s main job. Archer IRM fits large health systems that want one enterprise GRC system across risk, compliance, and audit, and its healthcare page says Archer “helps health systems unify HIPAA, privacy, and quality obligations.” OneTrust fits programs centered on privacy, data governance, and third-party risk. LogicManager fits organizations that run risk management as an enterprise-wide program reporting to the board, and LogicGate fits teams that want to design their own GRC workflows without code. Isora GRC fits security teams that need to organize, distribute, and track security risk assessments across departments, systems, and vendors from one place. Compare each section above against the capabilities listed earlier, and ask each vendor to demonstrate them.
How do hospitals manage security risk assessments for clinical systems?
The HIPAA Security Rule’s risk analysis covers the potential risks and vulnerabilities to electronic protected health information “held by the covered entity or business associate,” so clinical systems that hold that information fall inside it. Start with a record of those systems, each with a named owner. Then send each owner a structured assessment, collect responses and evidence in one place, and record each finding with an owner and a due date. The rule then calls for security measures that reduce those risks “to a reasonable and appropriate level,” and for evaluations after “environmental or operational changes.” Isora’s HIPAA Security Rule page describes grouping HIPAA assessments “into a recurring series” that target every department, system, and business associate that handles ePHI.
What’s the difference between IT GRC tools and traditional cybersecurity software for healthcare organizations?
IT GRC tools manage the governance, risk, and compliance work around security: assessments, inventories of systems and vendors, risk registers, exceptions, and audit records. Cybersecurity software applies technical protections, such as threat detection, firewalls, and endpoint security. In HIPAA terms, a GRC tool can hold the records of the risk analysis and the periodic evaluation that 45 CFR 164.308 calls for, while the technical protections themselves come from security tools.
How do hospitals manage IT asset inventories and use asset assessments to support cybersecurity compliance?
A risk analysis under the Security Rule covers the electronic protected health information an organization holds, so the program needs to know which systems hold it and who owns each one. The platforms on this page approach inventory in different ways. OneTrust’s Tech Risk and Compliance page lists maintaining “an evergreen asset inventory,” LogicManager’s Security Risk Management Program says it can “catalog cybersecurity assets, applications, infrastructure, and technology services,” and Isora GRC supports inventory tracking alongside assessments. Ask each vendor to show one asset record with its owner, its last assessment and its open findings.
How do platforms support third-party risk management for hospitals?
Start with what the Security Rule requires. A covered entity may permit a business associate to create, receive, maintain, or transmit electronic protected health information on its behalf only if it obtains “satisfactory assurances” that the business associate “will appropriately safeguard the information.” Under 45 CFR 164.308(b)(3), those assurances are documented “through a written contract or other arrangement with the business associate.” Software keeps the vendor records and reviews that sit alongside those agreements. For example, Archer’s healthcare page describes tracking “every vendor’s certifications, audits, and BAAs in one portal,” OneTrust offers a Third-Party Management solution, and Isora GRC assesses internal teams and third-party vendors from one place.
What should healthcare IT teams look for in an IT risk and compliance platform?
Look for assessments that people outside security can answer, an inventory of the systems and vendors that handle electronic protected health information with named owners, a risk register with exception tracking, and dated records of each assessment and evaluation. Check how the platform handles the frameworks the organization follows, such as the HIPAA Security Rule. In a demo, ask to see an assessment request exactly as a respondent receives it, and one finding moving from assessment to closure.
For a framework to evaluate GRC platforms before a demo, download our GRC Buyer’s Guide for Information Security Teams.


This content is for informational purposes only and does not constitute legal or compliance advice. See our full disclaimer.
