TAC 202 Compliance Software
The GRC Assessment Platform™ for Texas Administrative Code §202 compliance

Isora GRC gives Texas state agencies and higher education institutions one connected workspace to operationalize Texas Administrative Code Chapter 202, with security assessments aligned to DIR control standards, system and vendor inventories, risk tracking and documented exceptions, and scorecards and reporting for DIR biennial submissions, all in one place.
Trusted by established organizations & partners
https://vt.eduhttps://www.af.milhttps://utexas.eduhttps://yale.eduhttps://www.tdi.texas.govhttps://www.ttuhsc.eduhttps://aws.amazon.comhttps://www.osu.eduhttps://www.wilcotx.govhttps://www.utoronto.cahttps://www.tdcj.texas.govhttps://www.uchicago.edu/enhttps://www.utah.eduhttps://dir.texas.govhttps://www.dps.texas.govhttps://www.berkeley.eduhttps://www.techstars.comhttps://cccs.eduhttps://www.iwu.eduhttps://msu.eduhttps://www.auburn.eduhttps://www.stthomas.eduhttps://www.getezmoney.comhttps://www.sait.cahttps://www.ubc.cahttps://www.cuanschutz.eduhttps://www.tjc.eduhttps://marymount.eduhttps://www.umt.eduhttps://www.pdx.eduhttps://www.tccd.eduhttps://ltu.eduhttps://morantechnology.comhttps://www.merit.eduhttps://www.tccd.eduhttps://www.gonzaga.eduhttps://www.bhc.eduhttps://www.dallascollege.edu
Problem
TAC 202 is one of many frameworks for Texas institutions

Meeting Texas Administrative Code Chapter 202 is challenging when security assessments consist of annual checklists and system inventories that are maintained separately, if at all. Texas universities also manage GLBA, HIPAA, NIST 800-53, and FERPA, each in its own spreadsheet on its own reporting timeline. But DIR only ever sees the TAC 202 slice.

Solution

One platform for the TAC 202 compliance lifecycle
Isora GRC structures the workflows for Texas state agencies and higher education institutions to meet TAC 202 compliance requirements. In Isora, teams can conduct security assessments aligned to DIR control standards, system and vendor inventories, risk tracking, and reporting. Assessment findings flow into the risk register, vendor records link to their questionnaire results, and reports pull from live data. Because TAC 202 maps to NIST, teams managing multiple frameworks can share one set of inventories and risk registers across every program.
Assessment Management
Run structured assessments aligned to TAC 202 control standards

Launch security assessments using questionnaires aligned to TAC 202 requirements, including access controls, risk management, incident response, change management, and the control categories that map to NIST. Target departments, divisions, and campus units, and collect evidence inline so every response carries the documentation DIR reporting requires. Set recurring cycles on the biennial timeline.

Learn More
Inventory Management
Maintain a connected inventory of every system and vendor in scope

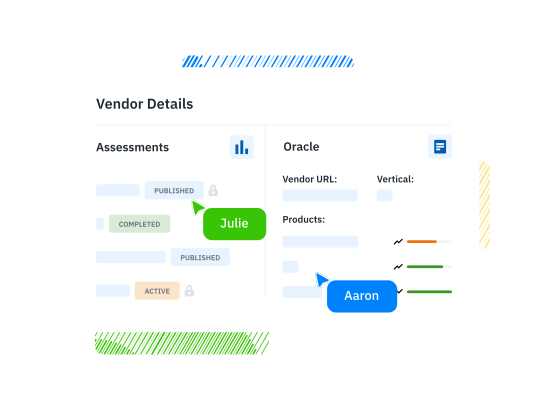
Track every system, application, and vendor within TAC 202 scope, with each record linked to its assessments, risks, data classifications, and contract documentation. When DIR asks what systems handle sensitive data and which controls are in place, the answer is a filtered report drawn from current records.
Learn More
Risk Management
Turn assessment gaps into tracked risks with owners, deadlines, and remediation plans

When a TAC 202 assessment identifies a control gap, Isora publishes it to the risk register with full lineage back to the control standard it maps to, the question that surfaced it, and the department or system it applies to. Assign owners, set remediation deadlines, and track progress in one view of institutional risk posture that stays current through the reporting cycle.

Learn More
Reports & Scorecards
Produce compliance documentation from live assessment data

Generate reports for assessment completion, control effectiveness, risk status, and remediation progress by department, control category, or institution-wide, with drill-down from every metric to the response and evidence behind it. An append-only audit log creates a time-stamped record of compliance activity between cycles. Export documentation packages for DIR biennial reporting, internal audit, and institutional leadership.

Learn More
Let’s Chat
See the GRC Assessment Platform in action
Isora GRC is the GRC Assessment Platform™ that gives security teams one connected workspace to run assessments, manage vendors and assets, track risks, and prove compliance.
Book a Demo
Latest News
Our latest content
Stay ahead of the curve with our latest research on a diverse range of topics exploring the ever-changing world of governance, risk, and compliance.

Third-Party Risk Management Frameworks: How to Build and Govern a TPRM Program A third-party risk management (TPRM) framework is the structure an...

TPRM Maturity Model: How to Score Third-Party Risk A TPRM maturity model is a self-assessment framework to score how developed a third-party risk...

NIST CSF vs Other Frameworks: Comparison Guide and Mapping Resources The NIST Cybersecurity Framework (CSF) is a voluntary, risk-based cybersecurity...

NIST 800-53 Vendor Management: How to Manage Third-Party Risk NIST 800-53 vendor management uses the NIST 800-53 System and Services Acquisition (SA)...

NIST 800-53 Data Classification: How It Determines Your Controls Before selecting the right NIST 800-53 controls, organizations must classify their...

NIST 800-53 Controls: Complete List and How They Work NIST 800-53 contains 1,196 security and privacy controls organized across 20 control families,...

Frequently Asked Questions
TAC 202 Compliance Software FAQs
Find the answers you need here, or chat with us.
Contact Sales
What is TAC 202?

Texas Administrative Code Title 1, Part 10, Chapter 202 establishes information security standards for Texas state agencies and institutions of higher education. It requires organizations to implement security programs with documented policies, risk assessments, incident response procedures, and control implementations aligned to standards that map to NIST frameworks. The Department of Information Resources (DIR) provides oversight and requires biennial compliance reporting.

How does TAC 202 relate to NIST frameworks?

TAC 202’s security control standards align to NIST frameworks, particularly NIST 800-53 and NIST CSF. Isora supports TAC 202 alongside NIST in the same workspace, with shared inventories, a shared risk register, and shared reporting. Organizations managing TAC 202 and NIST compliance assess once against mapped controls rather than running separate assessment programs.

Does Isora support other frameworks Texas institutions manage?

Yes. Texas universities and agencies frequently manage TAC 202 alongside GLBA (financial aid data), HIPAA (health center records), NIST 800-53 (federal research), FERPA, and HECVAT (vendor assessments). Isora supports all of these in one workspace. Assessment results, inventories, and risks are shared across frameworks, so a single data model serves every program.

How does Isora help with DIR biennial reporting?

Isora generates compliance reports from live assessment data. Reports show assessment completion, control effectiveness, risk posture, and remediation progress. Because the data is structured and time-stamped, biennial reporting becomes an export rather than a weeks-long project. The audit log gives DIR verifiable evidence of continuous compliance activity between reporting periods.