




Security teams today need more than checklists—they need flexible, collaborative workflows that support real-world risk management.
ZenGRC and Optro (formerly AuditBoard) are part of a growing class of all-in-one GRC platforms. They offer broad compliance and audit coverage across the enterprise, but that breadth often comes with tradeoffs: rigid workflows, siloed modules, and low adoption among the people doing the actual work.
Security teams need platforms that simplify—not complicate—risk management. When GRC tools are designed to serve everyone, they often fail to serve security well.
Isora GRC takes a focused approach. It’s built specifically for IT and third-party risk workflows, helping security teams run assessments, manage inventories, and track risks—without the friction of bloated GRC suites.
Choosing the Right Platform for IT Risk Management
ZenGRC and Optro offer robust functionality for compliance and audit programs, and both also sell risk management and third-party risk products. Long setup times, audit-first design, and complex interfaces often get in the way of adoption and impact.
Isora GRC is different. It’s purpose-built for information security risk management and third-party risk management—providing structured workflows for assessments, inventories, exception management, and risk registers. It’s fast to deploy, intuitive to use, and easy to adopt across technical and non-technical teams alike.
The Workflow That Matters: Managing IT Risks and Compliance
Security teams face a continuous stream of tasks: assessing internal departments and third parties, collecting and reviewing evidence, maintaining inventories, identifying risks, and coordinating remediation. None of that works without structured workflows and shared visibility.
Many traditional GRC tools weren’t designed to support this kind of cross-functional, real-time work. Their audit-centric foundations and generalized configurations make it harder to keep pace with risk.
Isora GRC brings these workflows together in a single, focused platform—giving teams the tools they need to move quickly, stay aligned, and manage risk proactively.
How Each Platform Supports IT Risk Management Workflows
| Workflow Area | ZenGRC | Optro | Isora GRC |
| Assessment Management | ZenGRC makes assessments simple to set up and track. Templates help speed things up. ZenGRC says teams can tailor it to their organization’s unique risk posture and scoring requirements. | Optro handles assessments well, and its IT & Cyber Risk Management product uses a configurable assessment process with out-of-the-box templates. Optro says OpsAudit’s audit logs record who changed what and the before-and-after state of the data. | Centralized, intuitive assessment dashboard across business units, vendors, and assets. Built specifically for security teams. |
| Questionnaire Delivery & Completion | Questionnaire management feels smooth for small projects. ZenGRC lets teams customize and send vendor questionnaires and collaborate on designing security questionnaires. | Survey tools link into the platform, which helps. Optro’s WorkStream feature collects risk information from the business through survey-based workflows. OpsAudit manages document requests, follow-ups and stakeholder reporting. | Customizable and prebuilt questionnaires for frameworks like NIST, ISO, GLBA, HIPAA, and more. Designed for internal and external collaboration. |
| Inventory Tracking | Asset and vendor inventories are easy to start but can become siloed. ZenGRC’s API documentation lists Data Assets and Systems objects, and vulnerabilities can be mapped to both and to risks. | The system connects to many apps, which is helpful. Optro’s IT & Cyber Risk Management product takes in new IT assets through native integrations and runs business impact assessments at the asset level. | Centralized tracking of assets, vendors, and organizational units with integration support for existing data sources. |
| Risk Register & Exception Management | ZenGRC handles basic risk and exception tracking well. Its API documents exception records with owners, status, and effective and stop dates, and each exception can be mapped to risks. | Optro links risk, compliance, and audit. Its IT risk and compliance page lists exceptions management, and its FAQ calls the platform highly configurable. | Flexible, collaborative risk register with scoring, status, evidence, and ownership tied directly to assessments. Exception management is built-in and intuitive—no extra modules or configuration required. |
| Scoring, Reporting & Risk Visualization | ZenGRC lists customizable dashboards, risk reporting, and a risk timeline and heatmap. It also offers a Business Intelligence Portal and a Tableau integration. | Reports and risk visuals work. Optro offers customizable, role-based dashboards that track audit progress, findings, requests and issue remediation. | Automated scorecards, risk maps, and executive-friendly reports with actionable insights—no manual config required. |
| Collaboration & User Experience | The interface is clean and simple to learn. ZenGRC says teams can engage with vendors and each other through comments and detailed transaction histories. | The layout feels clean and simple. Teams can share files in the cloud. Optro says OpsAudit draws on a unified GRC data core so teams can collaborate across all lines. | WCAG-compliant, award-nominated interface with built-in commenting, team workflows, and fast onboarding. |
| Implementation & Setup | Setup is faster for companies sticking to out-of-the-box workflows. ZenGRC’s onboarding page says a designated Customer Success Manager leads onboarding, which typically takes 4-8 weeks, as of September 2026. | Setup goes fast, and support feels strong. Still, users want deeper training to unlock the tool’s full power. | No-code setup in days or weeks. Minimal IT lift required. Designed to go live quickly across teams and vendors. |
What Sets Isora GRC Apart?
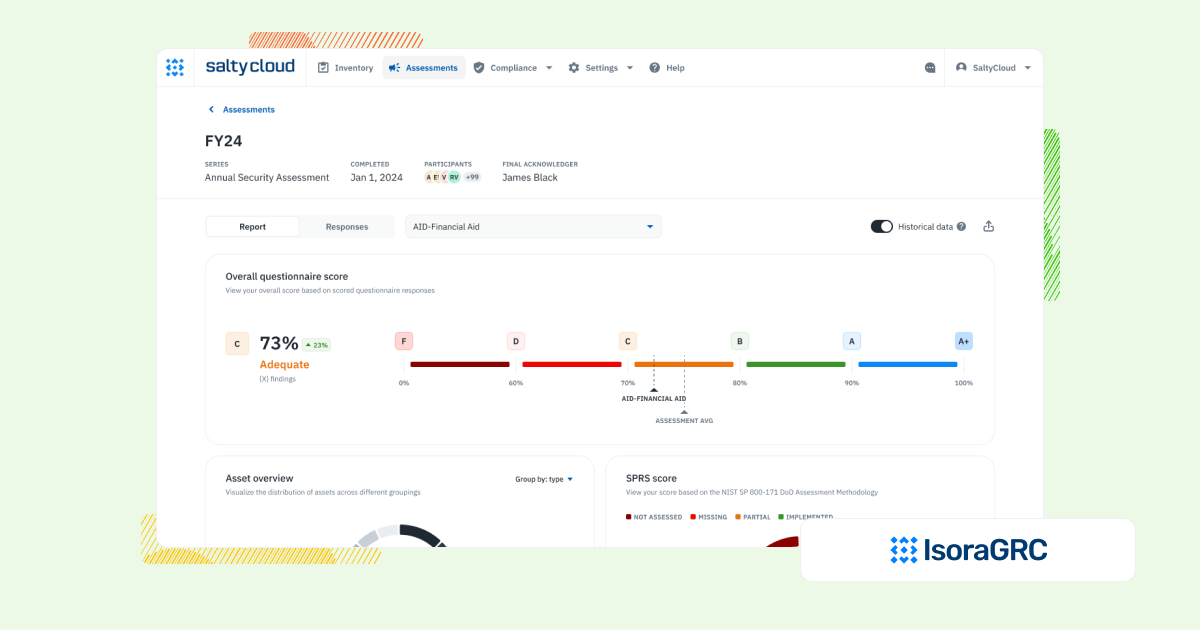
Isora GRC was purpose-built for information security teams—designed to support the real workflows behind risk and compliance, not just generate reports. While legacy GRC platforms require months of configuration and rigid processes, Isora takes a modern, scalable approach:
- Purpose-built for security and third-party risk teams
- No extra modules or cross-department bloat—just the workflows that matter.
- Easy for anyone to use
- Clean UI, no complex training, and built to drive adoption across the org.
- Streamlined for action, not just documentation
- Assessments, questionnaires, inventories, risk tracking, and reporting—all in one place.
- Fast, no-code implementation
- Go live in weeks, not quarters, with minimal IT lift.
- Scales with your program
- Whether you’re running a lean risk function or supporting a large institution, Isora grows with you—without getting in the way.
Who Each Platform Is Best For
| Platform | Who It’s For |
| ZenGRC | Teams focused on passing audits like SOC 2 or ISO. Easier to start than big platforms. ZenGRC also lists Risk Management and Vendor Management modules with real-time risk monitoring. |
| Optro | Mid to large teams doing audits and tracking controls. Simple for auditors, and Optro also lists an Infosec solution and an IT & Cyber Risk Management product. |
| Isora GRC | Security teams that need a scalable, usable IT risk management program across their organization. |
What Our Customers Say About Isora GRC
Security teams at top institutions are using Isora GRC to replace legacy tools and manual processes with intuitive workflows and actionable insight.
FAQs
What’s the difference between ZenGRC, AuditBoard, and Isora GRC?
ZenGRC and Optro are designed as broad GRC platforms, often focused on audit, SOX, and enterprise compliance. Isora GRC is built specifically for IT and vendor risk workflows, giving security teams purpose-built tools to assess, track, and respond to risk across the organization.
Are ZenGRC and AuditBoard considered all-in-one GRC platforms?
Yes. They offer features for multiple departments—compliance, audit, finance, legal—which can make them harder to adopt for security teams focused on assessments, inventories, and exceptions.
Does Isora GRC replace platforms like ZenGRC or AuditBoard?
Yes, especially for teams that want a faster, more focused way to manage IT risk. While ZenGRC and Optro support audit-heavy use cases, Isora GRC streamlines workflows security teams actually use—without the extra overhead.
Which platform is better for managing IT risk and security assessments?
Isora GRC is purpose-built for that exact use case. It supports questionnaires, asset inventories, exception management, and risk tracking in a clean, usable platform. ZenGRC and Optro are often geared toward audit teams first, and both also sell risk and third-party risk products.
Can Isora GRC be used alongside a platform like AuditBoard?
Yes. Some organizations use Isora for operational risk management and keep Optro for SOX or audit compliance. Others transition fully to Isora when audit coverage isn’t their primary focus.
What should I look for in a GRC platform to manage IT and vendor risk?
Look for usability, cross-functional adoption, and workflow coverage. Isora GRC helps teams manage assessments, inventories, and exceptions in one system—without relying on spreadsheets or manual follow-up.


This content is for informational purposes only and does not constitute legal or compliance advice. See our full disclaimer.
