


Woot!
We got your request. Hang on tight and we'll get back to you!

 Assessment Management
Run structured security assessments across systems, teams, and vendors—all from one place.
 Questionnaires & Surveys
Launch structured questionnaires and collect evidence from the people closest to each control.
 Reports & Scorecards
Turn assessments into audit-ready reports and actionable insights your team can actually use.
 Inventory Management
Maintain a connected inventory of vendors, assets, and systems linked to assessments and risks.
 Exception Management
Log, track, and resolve policy exceptions so nothing falls through the cracks during audits.
 Risk Management
Turn assessment findings into a living risk register with owners, remediation plans, and full lineage.
 Information Security Risk Management (ISRM)
Run assessments across units and systems, maintain IT asset inventories, and collaborate on a shared risk register—all in one place.
 Third-Party Security Risk Management (TPSRM)
Track vendors, send security questionnaires, and manage third-party risk with built-in workflows and a centralized inventory.





Import vendor-completed HECVAT spreadsheets with the one-click uploader, which matches responses to questions, computes scores, and links results to the vendor's inventory record. In Isora, each vendor carries a defensible assessment history with product deployments, data classifications, contracts, and risk ratings, so procurement can see a vendor's current status, on demand.
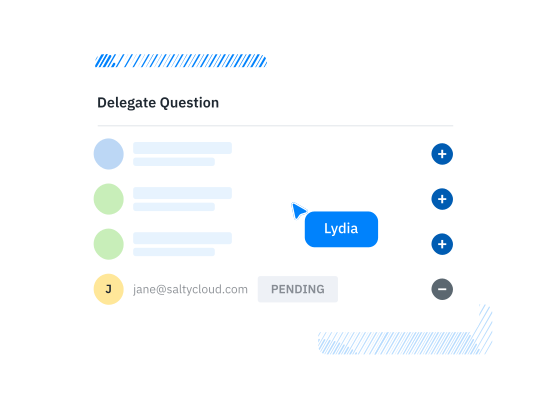
Target every organizational unit from one dashboard. Security teams assign questionnaires to department heads and IT liaisons, who respond without GRC training. Prebuilt questionnaires cover GLBA, NIST CSF, NIST 800-53, and HIPAA, and custom assessments handle institution-specific requirements. In Isora, completion tracking updates in real time, and each cycle reuses the same assessment.

Turn GLBA and HECVAT findings into tracked risks with full lineage back to the questionnaire item, the department or vendor it applies to, and the framework requirement it maps to. Assign owners, set remediation deadlines, and track progress in a risk register that gives the whole institution one current view of its security posture.

Generate reports and scorecards from live assessment data for completion, control effectiveness, risk ratings, and remediation progress by department, framework, or institution-wide. Drill-down into every response and the evidence behind it with figures that stay current from the moment the report opens. Export findings for IT governance committees, CIO briefings, and board presentations, in just a few clicks.

