




IT Risk Management Software for State and Local Government Agencies: Compare GRC Platforms
A state or local government IT risk program assesses departments, systems, and vendors that the central security team does not run itself. The people who answer those assessments, and the evidence they provide, sit across the agency.
Some states publish their own security requirements. In California, the Department of Technology publishes the Statewide Information Management Manual (SIMM), which it calls “California’s central source for statewide technology policies, standards, instructions, forms, and templates.” Its SIMM 5300 information security series includes the SIMM 5300-B Foundational Framework, the SIMM 5300-C Cybersecurity Maturity Metrics, and a SIMM 5305-C Risk Register and Plan of Action and Milestones Worksheet.
In Texas, the Department of Information Resources (DIR) says the Texas Risk and Authorization Management Program (TX-RAMP) “provides a standardized approach for security assessment, certification, and continuous monitoring of cloud computing services that process the data of Texas state agencies.” DIR’s site notes that House Bill 150 (89R) transferred DIR’s cybersecurity functions to the Texas Cyber Command. GovRAMP, a nonprofit membership organization that brings governments and technology providers together, says it was built to establish “a common framework for verifying the security of cloud services and third-party technologies.”
Across these programs, the recurring work is assessing departments, systems, and cloud vendors, keeping a risk register with plans of action, and reporting the results. This guide compares IT risk management software for state and local government agencies against that work.
What to Look For in IT Risk Management Software for Public Sector Agencies
When evaluating IT risk management software for state and local government agencies, the factors an organization can consider depend on its use case. Still, here’s what a platform should cover:
- Structured security risk assessments against the frameworks the agency uses, such as NIST 800-53
- Questionnaire delivery and completion tracking for agency business units and third-party vendors
- A central inventory of IT assets, applications, and vendors, each with a named owner
- A risk register and exception tracking that follow each finding to closure, with plans of action and milestones
- Scoring and reports that leadership, auditors, and oversight bodies can read
- An interface that staff across departments, outside IT and security, can use
- A clear implementation timeline and the internal effort it requires
Make sure to ask potential vendors about each of these capabilities, before you sign a contract.
Top IT Risk Management Tools for State and Local Government Agencies
Isora GRC
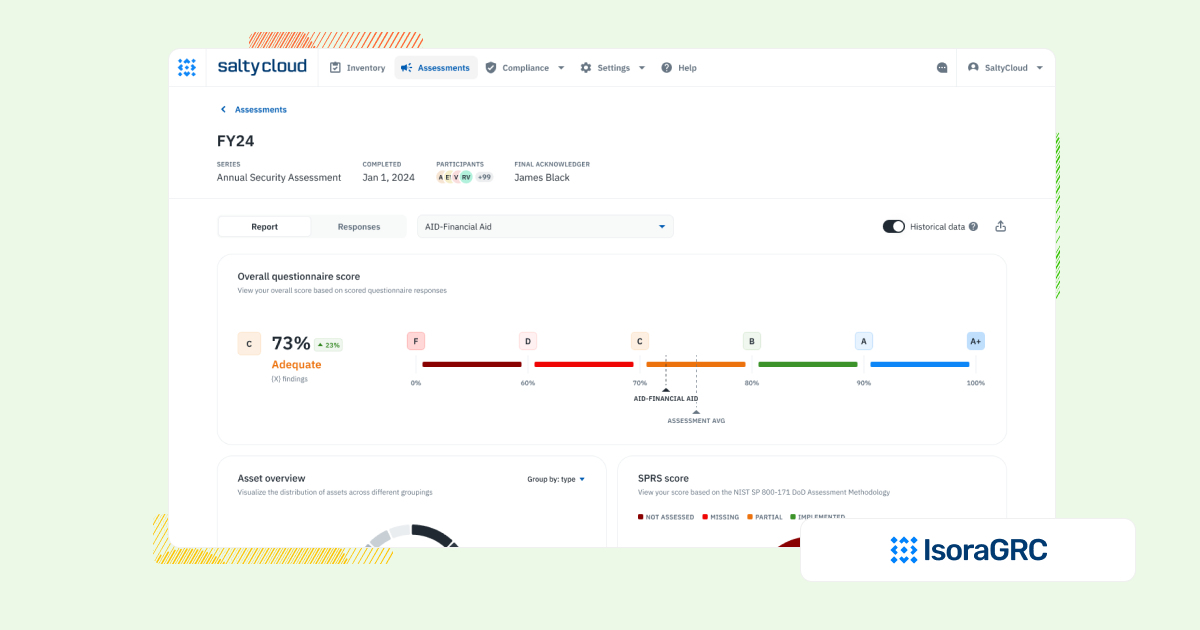
Isora GRC is the GRC Assessment Platform™ built specifically for information security teams. It supports the full risk workflow, from assessments and questionnaires to risks, inventory, and reporting. Its public sector page describes prebuilt NIST 800-53 questionnaires, with custom questionnaires for TAC 202, SIMM 5300, state security policies, and agency-specific requirements.
Best for: Security teams that need to operationalize IT and third-party risk management across assets, third-party vendors, and business units.
| Isora GRC | |
| Strengths | Built for workflows, not checklists
✅ Supports assessments, inventory tracking, risk registers, and exceptions in a unified experience. Designed for org-wide adoption ✅ WCAG-compliant UX built for respondents outside security, which makes risk everyone’s job. Fast time-to-value ✅ Live in days or weeks, with no-code setup and minimal lift from IT. Flexible by default ✅ Customizable assessments and framework-aligned questionnaires without heavy configuration. Scales across teams and vendors ✅ Assesses internal teams and third-party vendors from one place. |
| Limitations | ⚠️ Not designed for legal, audit, or finance teams seeking one platform for enterprise-wide GRC
⚠️ May be too structured for teams looking to build one-off surveys or lightweight audits without repeatable workflows |
Archer IRM
Archer IRM is an enterprise GRC platform used to manage risk, audit, and compliance across large organizations. Its public sector page says Archer helps government agencies “unify FedRAMP, CMMC, and FISMA obligations so compliance keeps pace with new mandates,” and that most enterprise deployments go live in 8–12 weeks.
Best for: Large government agencies with centralized GRC teams and the budget to support deep customization.
| Archer IRM | |
| Strengths | ✅ Deep governance and compliance functionality
✅ Highly configurable for enterprise-wide programs ✅ Security and vendor risk use cases ship with prebuilt content ✅ Its public sector page describes “one connected system of record for federal and state obligations, risks, controls, and issues across every agency,” as of October 2026 |
| Limitations | ⚠️ TX-RAMP, GovRAMP and CA SIMM 5300 are not named on Archer’s public sector page, as of October 2026 |
| Other Comparisons | Archer IRM vs ServiceNow GRC vs Isora GRC
LogicGate vs Archer IRM vs Isora GRC ZenGRC vs Archer IRM vs Isora GRC |
ServiceNow GRC
ServiceNow GRC extends ServiceNow’s ITSM platform with risk and compliance capabilities. It integrates well with IT operations, and ServiceNow describes IRM as connecting risk and compliance across IT, cyber and business operations.
Best for: Agencies already using ServiceNow for IT operations that want to layer in GRC functionality.
| ServiceNow GRC | |
| Strengths | ✅ Strong integration with ServiceNow’s service desk and incident response tools
✅ Lists security risk assessments under Tech and Cyber Risk Management ✅ Its Continuous Authorization and Monitoring app on the ServiceNow Store supports the NIST Risk Management Framework and automates tasks across Plans of Action and Milestones (POA&Ms), as of October 2026 |
| Limitations | ⚠️ Built on the same platform as its ITSM products, and IRM’s depth across inventory, risk and compliance assumes a populated configuration management database (CMDB) |
| Other Comparisons | Archer IRM vs ServiceNow GRC vs Isora GRC
OneTrust vs ServiceNow GRC vs Isora GRC |
OneTrust
OneTrust extends its privacy platform with compliance and third-party risk tools. It is useful for regulatory reviews and vendor questionnaires, and it also lists IT Risk Management and an evergreen asset inventory.
Best for: Organizations focused on privacy, data governance, and third-party risk. OneTrust also lists IT Risk Management.
| OneTrust | |
| Strengths | ✅ Good for vendor risk reviews and privacy-focused compliance programs
✅ Includes out-of-the-box templates for third-party risk assessments ✅ Lists IT risk management, an evergreen asset inventory and exception tracking, and OneTrust’s Tech Risk and Compliance page says UI-driven configuration simplifies configuration updates without the need for IT resources, as of September 2026 |
| Limitations | ⚠️ OneTrust’s pricing page says each solution package has one or more usage meters, as of October 2026 |
| Other Comparisons | OneTrust vs ServiceNow GRC vs Isora GRC |
MetricStream
MetricStream is an enterprise GRC platform. Its IT & Cyber Risk Management product says it “enables users to conduct IT risk assessments, implement controls, and take necessary mitigation actions,” and it keeps IT risks, assets, threats, vulnerabilities, processes, and controls in a central repository.
Best for: Large organizations that need to manage complex regulatory programs and cross-functional GRC at scale.
| MetricStream | |
| Strengths | ✅ Enterprise-grade GRC with strong reporting and audit tools
✅ Supports frameworks like NIST 800-53, ISO 27001, and SOX ✅ Lists IT risk assessments, an asset and threat repository and closed-loop remediation, as of October 2026 ✅ Its IT & Cyber Risk Management page says the product integrates with Configuration Management Databases (CMDBs) and security intelligence feeds, as of October 2026 |
| Limitations | ⚠️ IT and cyber risk and IT vendor risk run as separate MetricStream products, as of October 2026
⚠️ Government and the public sector are not among the eight industries in MetricStream’s site menu (banking and financial services, energy, healthcare, insurance, life sciences, technology, telecom, and utilities), as of October 2026 |
| Other Comparisons | MetricStream vs SAP GRC vs Isora GRC |
What Customers Say About Isora GRC
Security teams use Isora GRC to replace manual processes with intuitive workflows and actionable insight.
SaltyCloud makes Isora GRC, one of the products compared here. The assessments are our own, so confirm current features and pricing with each vendor before you decide.
FAQs
What is the best IT GRC tool for state and local government agencies to manage cybersecurity compliance?
It depends on where the agency’s program runs today and what it has to produce. For an agency already standardized on ServiceNow for IT operations, ServiceNow GRC adds risk and compliance records to the same platform, and its depth assumes a populated configuration management database (CMDB). For a large agency with a centralized GRC team and budget for configuration, Archer’s public sector page describes one connected system of record for federal and state obligations. MetricStream fits large organizations running complex regulatory programs across functions, and OneTrust fits programs centered on privacy, data governance, and third-party risk. For a security team that runs recurring assessments of departments, systems, and vendors, Isora GRC supports assessments, inventory tracking, risk registers, and exceptions in one place. Ask each vendor to show a populated inventory and a single finding moving from recorded to closed.
How do state and local government agencies perform NIST 800-53 security assessments?
NIST publishes the controls and the assessment method separately. NIST SP 800-53 Rev. 5 “provides a catalog of security and privacy controls for information systems and organizations,” and NIST SP 800-53A Rev. 5 “provides a methodology and set of procedures for conducting assessments of security and privacy controls.” Software supports this work by assigning assessments to the people who run each system, collecting their answers and evidence, and recording each gap as a finding with an owner. Isora GRC’s public sector page describes prebuilt NIST 800-53 questionnaires, and the release notes for ServiceNow’s Continuous Authorization and Monitoring app describe a NIST SP 800-53 Rev 5.2 content library.
What’s the difference between general compliance software and specialized IT risk software for public sector agencies?
They are organized around different jobs. Compliance automation software is built to prove an organization’s own controls to an auditor. IT risk software for an agency runs assessments of departments, systems, and vendors that the security team does not operate, which is a different population of respondents. Enterprise GRC platforms such as Archer IRM and MetricStream form a third group, consolidating enterprise risk, audit, policy, and compliance on one system. Match the category to the job before comparing features.
How does a centralized IT asset inventory support state and local government risk programs?
The inventory is the list the assessment program works from. When each department, system, and vendor has a named owner, the security team knows who should answer each assessment and which systems still need one. The platforms on this page approach the inventory differently. OneTrust’s Tech Risk and Compliance page lists an “evergreen asset inventory,” MetricStream keeps IT assets, threats, and vulnerabilities in a central repository and integrates with CMDBs, and ServiceNow IRM shares one data model with the customer’s IT service and asset data. In Isora GRC, inventory, findings, risks, exceptions, and reports all attach to assessment data.
How can state and local agencies manage third-party vendor risk?
For cloud services, some states run their own security programs. TX-RAMP, as Texas DIR describes it, covers cloud computing services that process the data of Texas state agencies, and GovRAMP describes a common framework for verifying the security of cloud services and third-party technologies. An agency’s own vendor program adds a vendor inventory, security questionnaires, evidence, and findings tracked to closure. OneTrust’s Third-Party Management solution lists ways to “contextually tier and triage third parties to guide workflow priority and assessment depth.” Isora GRC assesses internal teams and third-party vendors from one place, and its public sector page says FedRAMP, GovRAMP, and TX-RAMP requirements “are supported through customizable assessments.” Where vendors rather than internal units are the main problem, a dedicated vendor risk platform adds continuous external monitoring, larger questionnaire libraries, and portfolio reporting.
What features should state and local agencies look for in IT risk management software?
Start with the list above: structured assessments against the frameworks the agency uses, questionnaire delivery to business units and vendors, an inventory with named owners, a risk register and exception tracking, reports for leadership and auditors, and an interface for staff outside security. Then ask each vendor for its full framework catalog rather than its total, and ask which frameworks ship pre-mapped and which arrive as a services engagement. In a demo, ask to see a populated inventory and a single finding moving from recorded to closed.
How do IT risk management platforms help state and local government agencies prepare for audits and compliance reporting?
They keep the record that auditors and oversight bodies ask for. In California, the SIMM 5330 series covers “Information Security and Privacy Program Compliance,” including the SIMM 5330-B Information Security and Privacy Program Compliance Certification and the SIMM 5330-C Information Security Compliance Reporting Schedule. A platform that holds assessment results, evidence, the risk register, and plans of action in one place lets the team build that material from its working records. Isora GRC’s SIMM 5300 page describes POA&M tracking, documented exceptions, and “the SIMM 5330-B certification packages produced from that same record.”
For a framework to evaluate GRC platforms before a demo, download our GRC Buyer’s Guide for Information Security Teams.


This content is for informational purposes only and does not constitute legal or compliance advice. See our full disclaimer.
 Other Relevant Content
