NSPM-33 Compliance Software

The GRC Assessment Platform™ for NSPM-33 compliance

Isora GRC gives security teams one connected workspace to assess cybersecurity practices across research departments, applications, and vendors as part of their institution’s NSPM-33 research security program.
Trusted by established organizations & partners
https://vt.eduhttps://www.af.milhttps://utexas.eduhttps://yale.eduhttps://www.tdi.texas.govhttps://www.ttuhsc.eduhttps://aws.amazon.comhttps://www.osu.eduhttps://www.wilcotx.govhttps://www.utoronto.cahttps://www.tdcj.texas.govhttps://www.uchicago.edu/enhttps://www.utah.eduhttps://dir.texas.govhttps://www.dps.texas.govhttps://www.berkeley.eduhttps://www.techstars.comhttps://cccs.eduhttps://www.iwu.eduhttps://msu.eduhttps://www.auburn.eduhttps://www.stthomas.eduhttps://www.getezmoney.comhttps://www.sait.cahttps://www.ubc.cahttps://www.cuanschutz.eduhttps://www.tjc.eduhttps://marymount.eduhttps://www.umt.eduhttps://www.pdx.eduhttps://www.tccd.eduhttps://ltu.eduhttps://morantechnology.comhttps://www.merit.eduhttps://www.tccd.eduhttps://www.gonzaga.eduhttps://www.bhc.eduhttps://www.dallascollege.edu

Problem

Research cybersecurity evidence is spread across campus

Your research security office needs to know which departments have documented their cybersecurity practices, but responses arrive as lab spreadsheets, central IT policy links, application-owner emails, and separate vendor reviews. The security team has to reconcile those answers, locate supporting evidence, and identify the gaps that still need an owner. When research leadership asks for status, the assessment, evidence, and follow-up have to be assembled from different records.

Solution

Turn research cybersecurity requirements into a connected assessment process
Isora GRC connects research cybersecurity assessments, departmental and application inventories, vendor reviews, risk tracking, and reporting in one workspace. Build custom questionnaires from your institution’s approved requirements, collect evidence alongside responses, and publish findings to the risk register with their assessment context intact. Reviewers can see what was assessed, who contributed, and what needs follow-up.
Assessment Management
Assess research cybersecurity practices with evidence attached to responses

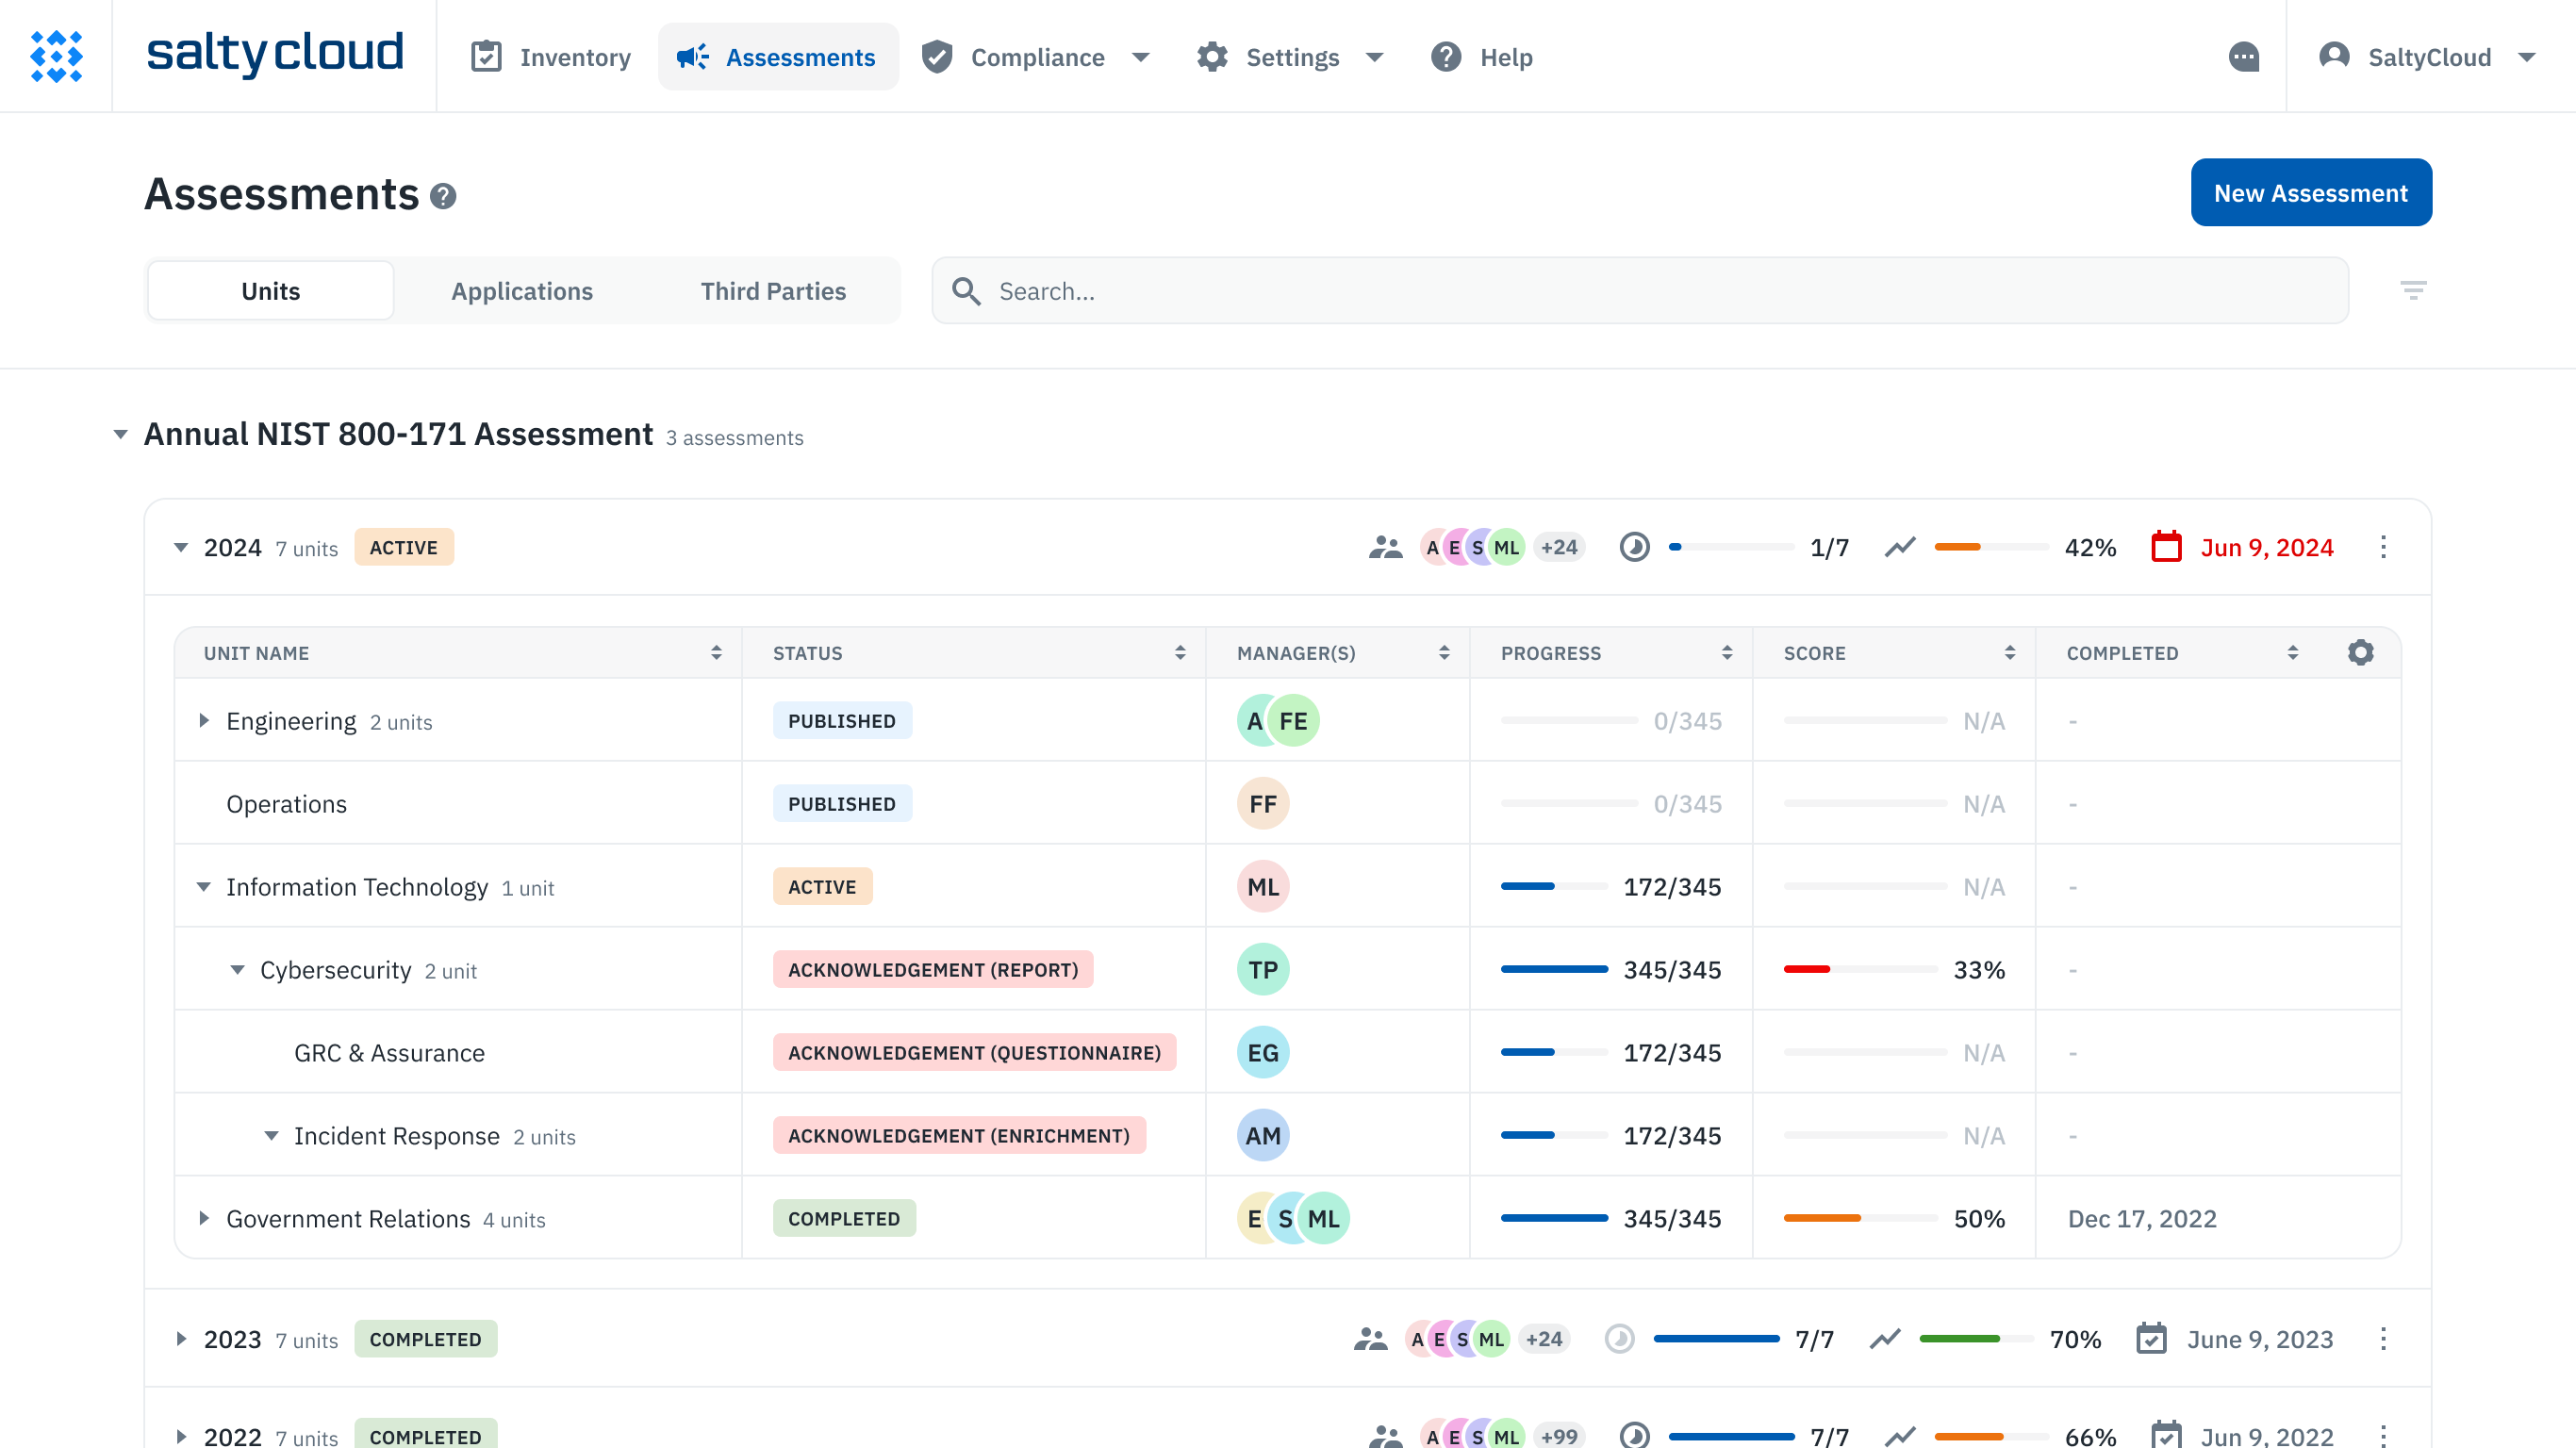
Launch assessments using custom questionnaires built around the research cybersecurity requirements your institution has approved. Department leads, application owners, and vendor contacts contribute responses and supporting evidence. Track completion, deadlines, and reminders across the campaign so reviewers can see which responses still need attention and examine the evidence behind those already submitted.
Learn More
Inventory Management
Define the research departments, applications, and vendors in scope

Maintain connected records for the departments, applications, and vendors included in your research cybersecurity reviews. Record ownership and data classification, then link each record to its assessments, risks, and exceptions. When research leadership asks what was covered, reviewers can identify the assessed units and systems and inspect the results associated with each record.

Learn More
Risk Management
Track research cybersecurity findings through remediation

Publish assessment findings to the risk register with the source question and assessment still connected. Assign an owner, document a remediation plan and milestones, and track progress against the identified gap. Where institutional policy permits an exception, record its justification, compensating controls, and expiration in the exceptions register so the follow-up decision remains documented alongside the affected record.

Learn More
Reports & Scorecards
Show research security leadership the evidence behind assessment results

Generate reports and scorecards from live assessment data to review completion and results across research departments, applications, and vendors. Drill into responses and supporting evidence, then export reports for program reviews. Leadership can examine the underlying assessment record while the security team maintains the findings and follow-up in the same workspace.

Learn More
Let’s Chat
See the GRC Assessment Platform in action
Isora GRC is the GRC Assessment Platform™ that gives security teams one connected workspace to run assessments, manage vendors and assets, track risks, and prove compliance.
Book a Demo
Related NSPM-33 content

Learn how NSPM-33 impacts research institutions and explore compliance strategies, including cybersecurity, export controls, and disclosure requirements.

Frequently Asked Questions
NSPM-33 Compliance Software FAQs
Find the answers you need here, or chat with us.
Contact Sales
How does Isora GRC support an NSPM-33 research security program?

Isora supports the cybersecurity assessment work within your institution’s research security program. Teams can collect responses and evidence from research departments, applications, and vendors, then connect findings to risks, remediation plans, and exceptions in the same workspace.

Does Isora GRC include a prebuilt NSPM-33 questionnaire?

Use custom questionnaires built around the requirements and policies your institution has approved. Your research security and sponsored research teams determine the applicable agency requirements; Isora provides the assessment, evidence collection, and follow-up workflow.

Can research departments and application owners contribute to assessments?

Yes. Multiple contributors can collaborate on questionnaire responses and attach supporting evidence to the questions they answer. Security reviewers can track completion and review the responses and evidence together.

Does an Isora GRC report certify NSPM-33 compliance?

No. Isora reports document assessment responses and supporting evidence. Institutional officials remain responsible for agency certifications and the broader research security program, including foreign travel security, research security training, and export control responsibilities.