


Woot!
We got your request. Hang on tight and we'll get back to you!

 Assessment Management
Run structured security assessments across systems, teams, and vendors—all from one place.
 Questionnaires & Surveys
Launch structured questionnaires and collect evidence from the people closest to each control.
 Reports & Scorecards
Turn assessments into audit-ready reports and actionable insights your team can actually use.
 Inventory Management
Maintain a connected inventory of vendors, assets, and systems linked to assessments and risks.
 Exception Management
Log, track, and resolve policy exceptions so nothing falls through the cracks during audits.
 Risk Management
Turn assessment findings into a living risk register with owners, remediation plans, and full lineage.
 Information Security Risk Management (ISRM)
Run assessments across units and systems, maintain IT asset inventories, and collaborate on a shared risk register—all in one place.
 Third-Party Security Risk Management (TPSRM)
Track vendors, send security questionnaires, and manage third-party risk with built-in workflows and a centralized inventory.





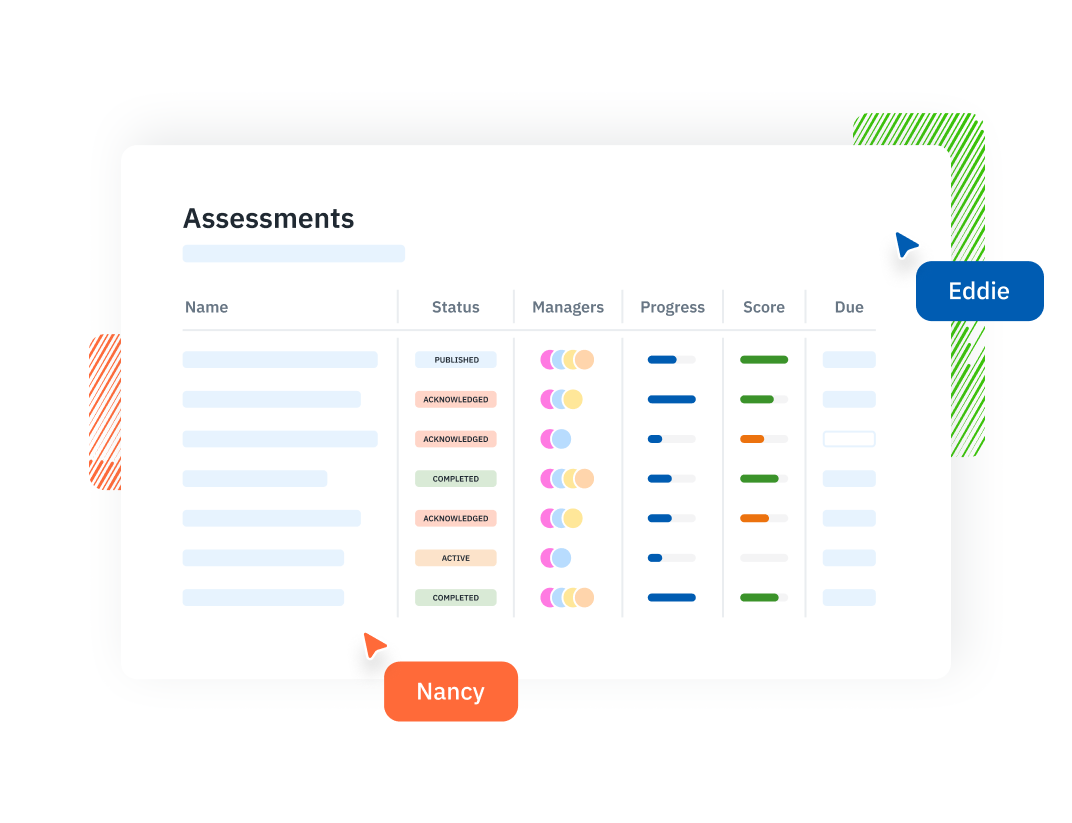
Launch assessments using prebuilt questionnaires aligned to Florida's Cybersecurity Standards (Chapter 60GG-2) and NIST CSF Functions. Target every agency unit, system, and data repository in scope, and collect access control policies, encryption documentation, and training records inline so responses and proof stay connected. Recurring cycles document continuous compliance between audit periods.
Every asset, application, and vendor record links to its assessments, risks, and documentation. Classify systems by FIPS 199 impact level, low through high, to drive assessment scoping and control selection, and track vendor relationships with linked questionnaires and attestations. When DMS or FDLE asks which systems handle sensitive data, the answer is structured and current.

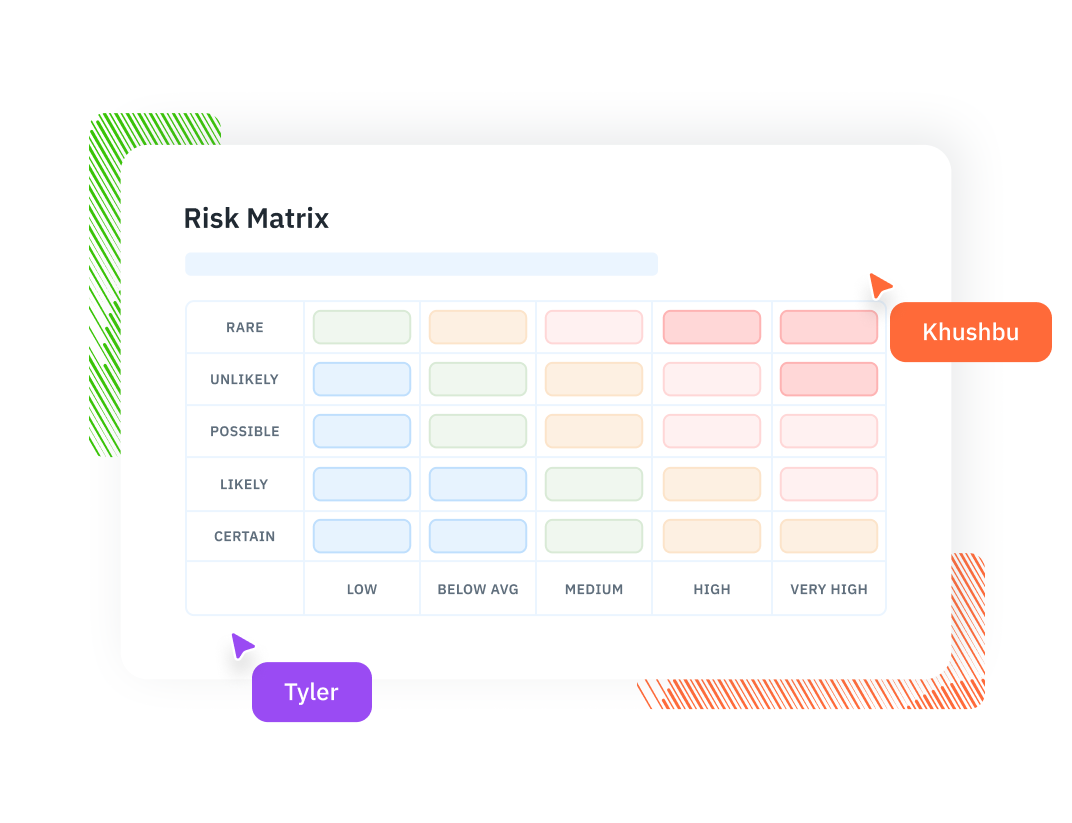
Publish a control gap to the risk register as soon as an assessment identifies it, and each risk carries lineage back to the Chapter 60GG-2 control it maps to and the system it applies to. Assign owners, set deadlines, and track remediation while an append-only audit log documents every action.
Generate reports and scorecards that pull from live assessment data, risk register entries, and inventory records to show assessment completion, control effectiveness, risk ratings by system, and remediation progress. Export packages aligned to DMS submission requirements, FDLE notification documentation, and agency leadership briefings.
