CMMC Compliance Software

The GRC Assessment Platform™ for CMMC Compliance

Isora GRC structures the self-assessments workflows for defense contractors and their subcontractors to meet Cybersecurity Maturity Model Certification (CMMC) Level 1 and Level 2 requirements. In Isora, teams can maintain in-scope CUI and FCI system inventories, link evidence to assessment responses, and route applicable findings into POA&Ms with practice-level lineage. Then, they can produce an SPRS score and assessment documentation from that same record, all in one place.

Trusted by established organizations & partners
https://vt.eduhttps://www.af.milhttps://utexas.eduhttps://yale.eduhttps://www.tdi.texas.govhttps://www.ttuhsc.eduhttps://aws.amazon.comhttps://www.osu.eduhttps://www.wilcotx.govhttps://www.utoronto.cahttps://www.tdcj.texas.govhttps://www.uchicago.edu/enhttps://www.utah.eduhttps://dir.texas.govhttps://www.dps.texas.govhttps://www.berkeley.eduhttps://www.techstars.comhttps://cccs.eduhttps://www.iwu.eduhttps://msu.eduhttps://www.auburn.eduhttps://www.stthomas.eduhttps://www.getezmoney.comhttps://www.sait.cahttps://www.ubc.cahttps://www.cuanschutz.eduhttps://www.tjc.eduhttps://marymount.eduhttps://www.umt.eduhttps://www.pdx.eduhttps://www.tccd.eduhttps://ltu.eduhttps://morantechnology.comhttps://www.merit.eduhttps://www.tccd.eduhttps://www.gonzaga.eduhttps://www.bhc.eduhttps://www.dallascollege.edu

Problem

CMMC evidence is disconnected from self-assessments

Assessing 15 CMMC Level 1 practices for FCI or 110 Level 2 requirements for CUI is challenging when the assessment spreadsheet, the POA&M, and the evidence files stay disconnected. When an SPRS score cannot be traced to the responses behind it, an inaccurate annual affirmation can become False Claims Act exposure.

Solution

One platform for the full CMMC self-assessment lifecycle
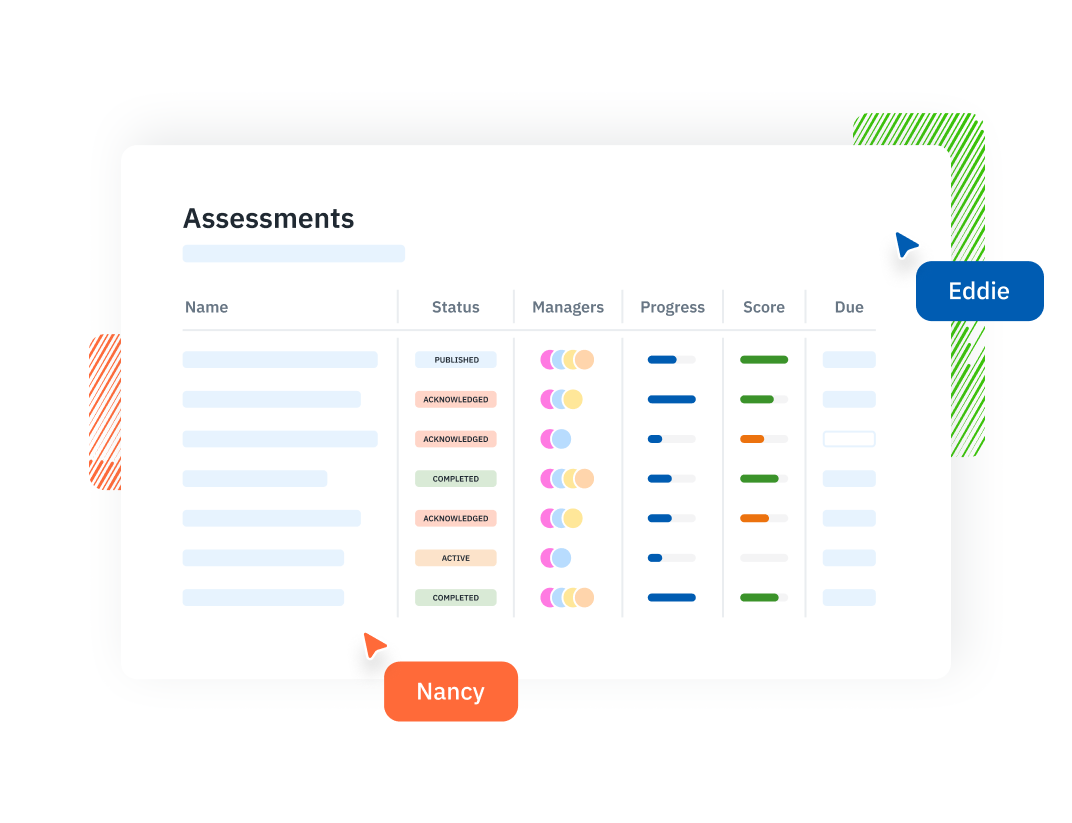
Isora GRC structures the workflows CMMC self-assessment requires in one connected workspace, with self-assessments mapped to Level 1 and Level 2 practices, CUI and FCI system inventories, Level 2 POA&M management, and documentation generation. Responses, evidence, findings, and in-scope systems stay linked, so the documentation behind an SPRS score and annual affirmation stays traceable.
Assessment Management
Run Level 1 FCI and Level 2 CUI self-assessments

Launch CMMC Level 1 and Level 2 self-assessments with questionnaires mapped to the applicable FCI and CUI practices. System owners and security leads attach policies, configurations, and training records to each practice as they respond. The finished assessment shows status by practice, domain, and system boundary with the evidence still attached.

Learn More
Inventory Management
Inventory every system within CMMC scope

Build the CMMC scope by inventorying every system and application that stores, processes, or transmits CUI or FCI. At Level 2, include the assets that protect CUI systems or can handle CUI. In Isora, each record links to its assessment results, applicable level, and risks. The result shows which systems were assessed, what information they handle, and where each boundary begins and ends.

Learn More
Risk Management
Track Level 2 POA&Ms through the 180-day closeout window

Publish eligible Level 2 findings to the risk register as POA&M items. Each item keeps its CMMC practice, NIST SP 800-171 requirement, assessment question, evidence, remediation plan, and milestone dates. That gives a working closeout record for progress, SPRS scoring impact, and the 180-day window.

Learn More
Reports & Scorecards
Produce the evidence package behind every affirmation and SPRS score

Export the documentation behind the self-assessment, annual affirmation, and SPRS score straight from the assessment record, with every result traceable to its responses, evidence, and remediation history in an append-only audit log. The same package answers DIBCAC assessments and prime contractor flow-down requests.

Learn More
Let’s Chat
See the GRC Assessment Platform in action
Isora GRC is the GRC Assessment Platform™ that gives security teams one connected workspace to run assessments, manage vendors and assets, track risks, and prove compliance.
Book a Demo
Latest News
Our latest content
Stay ahead of the curve with our latest research on a diverse range of topics exploring the ever-changing world of governance, risk, and compliance.

CMMC 2.0: The Model, the Rules, and the Timeline CMMC 2.0 is the U.S. DoD restructured Cybersecurity Maturity Model Certification (CMMC) program that...

CMMC Requirements: What Defense Contractors Must Implement at Each Level CMMC requirements set the cybersecurity standard a company must meet to win...

CMMC Assessment & Audit: Types, Process, and How to Prepare A CMMC audit is the common name for a CMMC assessment. This formal evaluation checks...

CMMC Certification: How to Get Your Organization Certified CMMC certification is the formal determination that a U.S. Department of Defense (DoD)...

CMMC Compliance: How to Achieve and Maintain It CMMC compliance means a Department of Defense (DoD) contractor has implemented the cybersecurity...

All you need to know about the CMMC, its framework, compliance requirements, and practical tips for defense contractors.

Frequently Asked Questions
CMMC Compliance Software FAQs
Find the answers you need here, or chat with us.
Contact Sales
What are the three CMMC levels?

CMMC Level 1 requires self-assessment against 15 basic practices protecting Federal Contract Information (FCI). Level 2 requires assessment against 110 practices mapping to NIST SP 800-171 and protecting Controlled Unclassified Information (CUI). Level 3 adds enhanced requirements from NIST SP 800-172 with DIBCAC assessment. Isora GRC supports CMMC Level 1 and Level 2 self-assessment.

Does Isora GRC handle CMMC certification?

No, Isora does not offer CMMC certification for organizations. It structures Level 1 and Level 2 self-assessments, maintains system inventories, manages Level 2 POA&Ms, and generates assessment documentation. When a third-party or government-led assessment applies to a contract, the same evidence package supports review by a C3PAO or DIBCAC. Isora is the self-assessment engine, not the assessing or certifying body.

How does CMMC relate to NIST 800-171 and DFARS?

CMMC Level 2’s 110 practices map directly to NIST SP 800-171’s 110 security requirements. DFARS 252.204-7012 requires defense contractors to implement NIST SP 800-171 for CUI systems. CMMC adds structured assessment and affirmation requirements to those safeguarding obligations. Isora supports NIST SP 800-171 and CMMC in the same workspace (shared inventories, shared POA&Ms, shared evidence) because Level 2 evaluates the same 110 requirements.
Can Isora GRC track SPRS scores?

Yes, Isora GRC can produce and track SPRS scores. Because it structures CMMC workflows in one workspace, Isora connects responses, evidence, findings, and in-scope systems to keep the documentation behind SPRS scores and annual affirmations complete and traceable