


Woot!
We got your request. Hang on tight and we'll get back to you!

 Assessment Management
Run structured security assessments across systems, teams, and vendors—all from one place.
 Questionnaires & Surveys
Launch structured questionnaires and collect evidence from the people closest to each control.
 Reports & Scorecards
Turn assessments into audit-ready reports and actionable insights your team can actually use.
 Inventory Management
Maintain a connected inventory of vendors, assets, and systems linked to assessments and risks.
 Exception Management
Log, track, and resolve policy exceptions so nothing falls through the cracks during audits.
 Risk Management
Turn assessment findings into a living risk register with owners, remediation plans, and full lineage.
 Information Security Risk Management (ISRM)
Run assessments across units and systems, maintain IT asset inventories, and collaborate on a shared risk register—all in one place.
 Third-Party Security Risk Management (TPSRM)
Track vendors, send security questionnaires, and manage third-party risk with built-in workflows and a centralized inventory.





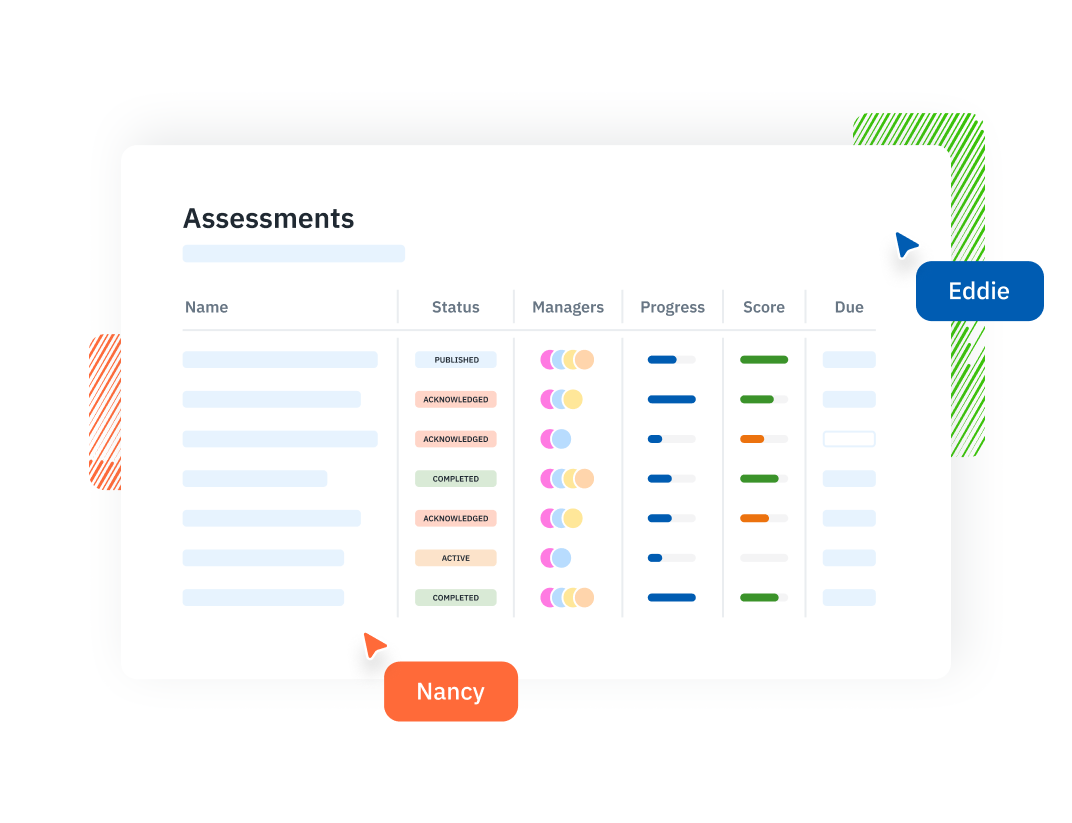
Launch risk assessments using prebuilt questionnaires aligned to NIST CSF and the CIS Controls, the two frameworks the statute names. Target departments, systems, and service providers, and collect policies, procedures, and training records inline so responses and proof stay connected. Recurring cycles keep the program current between audits.
Every system, application, and vendor record links to its assessments, risks, and documentation, with critical function designations, dependencies, and owners captured alongside it. ORC 9.64 lists identifying critical functions and cybersecurity risks as a program component, and a current system inventory supports that work. The inventory stays current because maintaining it is part of the assessment workflow.

Publish a gap to the risk register as soon as an assessment identifies it. Every finding carries lineage back to the program component it maps to, the assessment that surfaced it, and the system it affects. Assign owners, set completion dates, and track progress while an append-only audit log records every decision.

Generate reports and scorecards that pull from live assessment scores, risk register entries, inventory records, and training completion. Show coverage across all six program components without weeks of manual assembly, and drill into any metric to reach the assessment response behind it.

