IT Risk Management Software for State and Local Government
The GRC Assessment Platform™ for state and local agencies

Isora GRC gives security teams one connected workspace to operationalize federal and state requirements for public agencies, with assessments mapped to NIST 800-53 and state security policies, contractor and system inventories, risk tracking with assigned owners, and audit-ready reporting for legislators and oversight bodies, all in one place.
Trusted by established organizations & partners
https://vt.eduhttps://www.af.milhttps://utexas.eduhttps://yale.eduhttps://www.tdi.texas.govhttps://www.ttuhsc.eduhttps://aws.amazon.comhttps://www.osu.eduhttps://www.wilcotx.govhttps://www.utoronto.cahttps://www.tdcj.texas.govhttps://www.uchicago.edu/enhttps://www.utah.eduhttps://dir.texas.govhttps://www.dps.texas.govhttps://www.berkeley.eduhttps://www.techstars.comhttps://cccs.eduhttps://www.iwu.eduhttps://msu.eduhttps://www.auburn.eduhttps://www.stthomas.eduhttps://www.getezmoney.comhttps://www.sait.cahttps://www.ubc.cahttps://www.cuanschutz.eduhttps://www.tjc.eduhttps://marymount.eduhttps://www.umt.eduhttps://www.pdx.eduhttps://www.tccd.eduhttps://ltu.eduhttps://morantechnology.comhttps://www.merit.eduhttps://www.tccd.eduhttps://www.gonzaga.eduhttps://www.bhc.eduhttps://www.dallascollege.edu

Problem

Most agencies answer to federal and state mandates

State and local security teams face federal mandates, state requirements like TAC 202 and SIMM 5300, and legislative oversight, usually with staff who handle compliance alongside helpdesk and networking. Assessments, vendor oversight, and risk tracking end up in separate spreadsheets, and assembling evidence for an audit takes days.

Solution

One platform for state and local compliance
Isora GRC brings compliance workflows for state and local agencies into one connected workspace, with prebuilt assessments, connected contractor and system inventories, risk tracking, and reporting. In Isora, the documentation auditors and oversight bodies expect is a byproduct of doing the work.
Assessment Management
Send the first assessment within weeks of setup

Launch assessments using prebuilt NIST 800-53 questionnaires, with custom questionnaires for TAC 202, SIMM 5300, state security policies, and agency-specific requirements. Assign them to department leads and system owners across the agency and track completion without chasing email. In Isora, the first assessment goes out with no-code setup and no outside consultants.

Learn More
Inventory Management
Document vendor compliance for state contracts

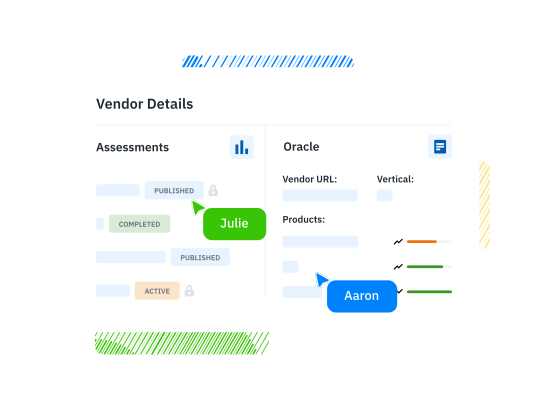
Maintain a vendor inventory linked to security questionnaires, assessment results, risk ratings, and contract documentation, and track which contractors access citizen data and when they were last assessed. When a state contract requires documented vendor security oversight, the evidence is already structured in Isora.
Learn More
Risk Management
Turn assessment findings into documented risks with owners

Assign owners and remediation deadlines as assessment findings flow into the risk register. Track high-risk areas across departments with an append-only audit log that documents every action. When oversight bodies ask about a specific risk, a simple query into Isora’s record shows the assessment that found it, the system it applies to, and every action taken since.

Learn More
Reports & Scorecards
Produce audit-ready reports for legislators, auditors, and oversight bodies

Generate agency-wide reports and scorecards for assessment completion, control effectiveness, risk status, and remediation progress. Drill down from any summary figure to the individual response behind it, with the evidence and comments attached. Export packages for legislative reviews, state auditor examinations, and compliance reporting, in just a few clicks. In Isora, dashboards pull from live assessment data to stay current.

Learn More
Let’s Chat
See the GRC Assessment Platform in action
Isora GRC is the GRC Assessment Platform™ that gives security teams one connected workspace to run assessments, manage vendors and assets, track risks, and prove compliance.
Book a Demo
Latest News
Our latest content
Stay ahead of the curve with our latest research on a diverse range of topics exploring the ever-changing world of governance, risk, and compliance.

CJIS Compliance: What It Requires and Where Agencies Fail Criminal Justice Information Services (CJIS) compliance means meeting the minimum security...

The CJIS Security Policy: What It Covers and What Changed The CJIS Security Policy is the FBI’s minimum security standard for protecting...

What Is CJIS? The FBI Division, the Security Policy, and What It Requires Criminal Justice Information Services (CJIS) is the FBI division that...

Third-Party Risk Management Software: Tools, Platforms & How to Choose Third-party risk management (TPRM) software is the system a security...

Third-Party Risk Management Frameworks: How to Build and Govern a TPRM Program A third-party risk management (TPRM) framework is the structure an...

Vendor Risk Assessment: How to Evaluate Third-Party Risk A vendor risk assessment is the process of evaluating the security, financial, operational,...

Frequently Asked Questions
IT Risk Management Software for State and Local Government FAQs
Find the answers you need here, or chat with us.
Contact Sales
What compliance frameworks does Isora support for government agencies?

Isora includes prebuilt questionnaires for NIST 800-53, NIST CSF 2.0, and supports state-specific frameworks including TAC 202, SIMM 5300, North Carolina SISM, Ohio ORC 9.64, and more. FedRAMP, StateRAMP, and TX-RAMP requirements are supported through customizable assessments. All frameworks share the same workspace and risk register.

How long does Isora take to deploy at a government agency?

Isora deploys in weeks with no-code setup, minimal IT lift, and no outside consultants. Prebuilt NIST 800-53 questionnaires mean the first assessment goes out without months of configuration. This matters for government teams where IT staff manage compliance alongside helpdesk, networking, and everything else.

Can Isora handle vendor oversight requirements for state contracts?

Yes. Isora maintains a centralized vendor inventory with linked security questionnaires, assessment results, and risk ratings. Agencies can track which vendors access sensitive systems, when they were last assessed, and what their current risk posture is, which is the documented oversight state contracts and federal partners require.

How does Isora work for agencies with lean security teams?

Isora is designed for teams managing compliance alongside other responsibilities, with no-code setup and questionnaires built for respondents who have no GRC training. Department leads complete assessments through an interface that works at current agency staffing levels.

Can Isora support FedRAMP and StateRAMP requirements?

Isora’s prebuilt 800-53 questionnaires and customizable assessment workflows support the control assessment requirements that underpin FedRAMP, StateRAMP, and TX-RAMP. The connected inventory and risk register provide the system-level documentation these programs require.

How does Isora compare to enterprise GRC tools for government?

Enterprise GRC platforms require months of implementation, dedicated administrators, and ongoing consultant support, which puts them beyond most state and local budgets and timelines. Isora deploys in weeks at a fraction of the cost, with prebuilt templates and no-code setup designed for teams without a dedicated GRC admin.